KMKazem Mortazaviinsecurityland.hashnode.dev·1m ago · 2 min readOne attacker, many AI agents: what the South Korean bank intrusions teach defendersFor years we have heard that AI would one day make attackers faster. A case published this week by CrowdStrike shows that day has arrived, not through some exotic super-weapon, but through freely avai00
KMKazem Mortazaviinsecurityland.hashnode.dev·2m ago · 2 min readEndpoint protection for organizations: EPP, EDR, XDR and what to evaluateAn email attachment, a USB stick brought in from home, a compromised website: that is how many attacks begin. For a network administrator, the useful question is not "is antivirus installed on every m00
MFMahir Faysalinmfaysaldev.hashnode.dev·24m ago · 13 min readWhat Is UAC in Windows? User Account Control Explained for BeginnersUAC (User Account Control) is the Windows security feature that makes even administrator accounts run programs with standard user rights, and asks you to approve or supply a password before anything g00
SLSarika Lalinsarikalal.hashnode.dev·13h ago · 7 min readDoes AI Create Trust or Uncertainty?During a conversation with a prospective customer, a question came up that stayed with me. They wanted to understand what would happen to their institution's data if AI were introduced into the softwa10
李李弘基inkd-agentic.hashnode.dev·6h ago · 10 min readAI Daily Digest October 12, 2026: Cloudflare Absorbs Deno, OpenAI Exposes Fake Journalists, Google Opens SynthID to E...Seven stories for Monday, October 12. Cloudflare folds the Deno team into Workers, OpenAI documents a fake-journalist influence network, a UK nonprofit finds most AI models fail terrorism safety tests00
MGMatin Ghorbaniinmatin-ghorbani.hashnode.dev·13h ago · 4 min readUnderstanding Subresource Integrity (SRI) in Web SecurityWhile learning about web security, I came across a security feature that I hadn't paid much attention to before: Subresource Integrity (SRI). I learned about SRI while reviewing how a website loaded a00
KMKazem Mortazaviinsecurityland.hashnode.dev·14h ago · 2 min readWhy a Green Antivirus Console Misses Most Modern Intrusions: EPP, EDR and XDR ExplainedIn incident reviews I keep seeing the same scene. The network manager opens the antivirus console and proudly shows that everything is green. A few hours later we find that the attacker logged in days00
KMKazem Mortazaviinsecurityland.hashnode.dev·1d ago · 2 min readAfter the vulnerability scan: from one-off scanning to continuous managementA good vulnerability scan hands you a long list of problems. The real question is what happens after the scan: who makes sure that list gets shorter month after month? Choosing between Tenable's produ00
KMKazem Mortazaviinsecurityland.hashnode.dev·1d ago · 3 min readYour backup server is a target, not a safety net: lessons from the AhsayCBS attacksWe tend to treat the backup server as the quiet box we only think about on the worst day. This week's attacks on AhsayCBS show that attackers see it very differently: a backup server means broad acces00
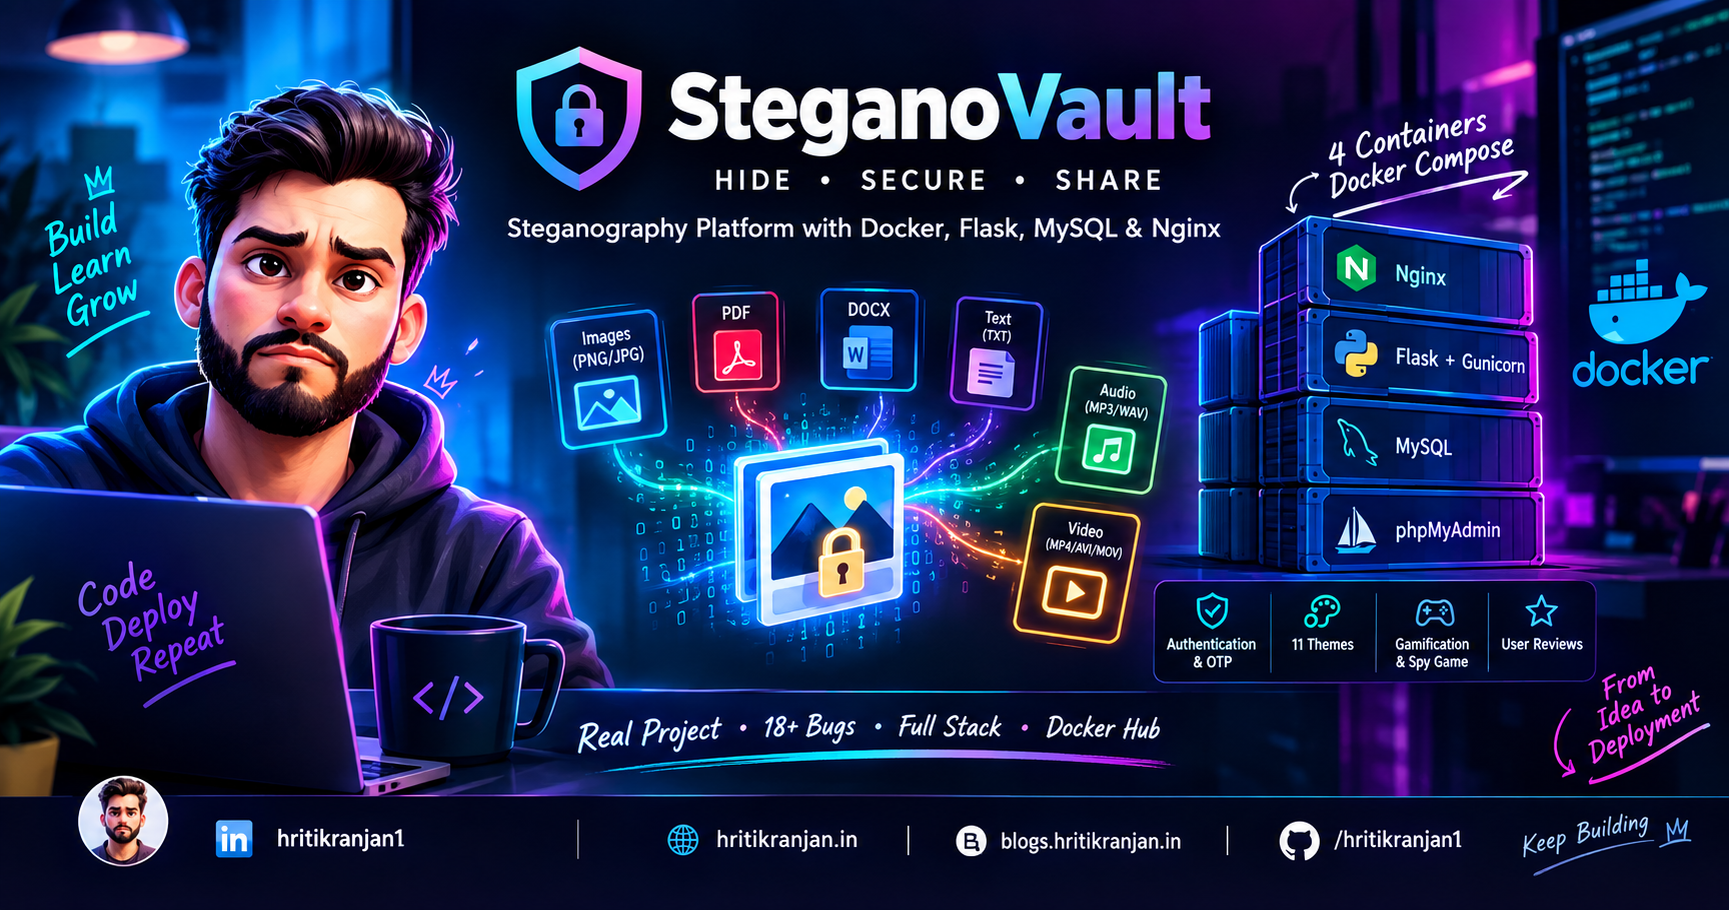
HRHritik ranjaninblogs.hritikranjan.in·1d ago · 54 min read🔐 Building SteganoVault: A Production-Grade Steganography Tool with Docker, Flask, MySQL, and Nginx📚 Table of Contents Introduction What is Steganography? Why I Built SteganoVault Project Overview Main Features Technology Stack How Steganography Works in SteganoVault System Architecture C00