The strongest part here is the separation between “the action was authorized,” “the action executed,” and “the intended outcome actually happened.” Those are three different guarantees, and agent systems often collapse them into one success signal.
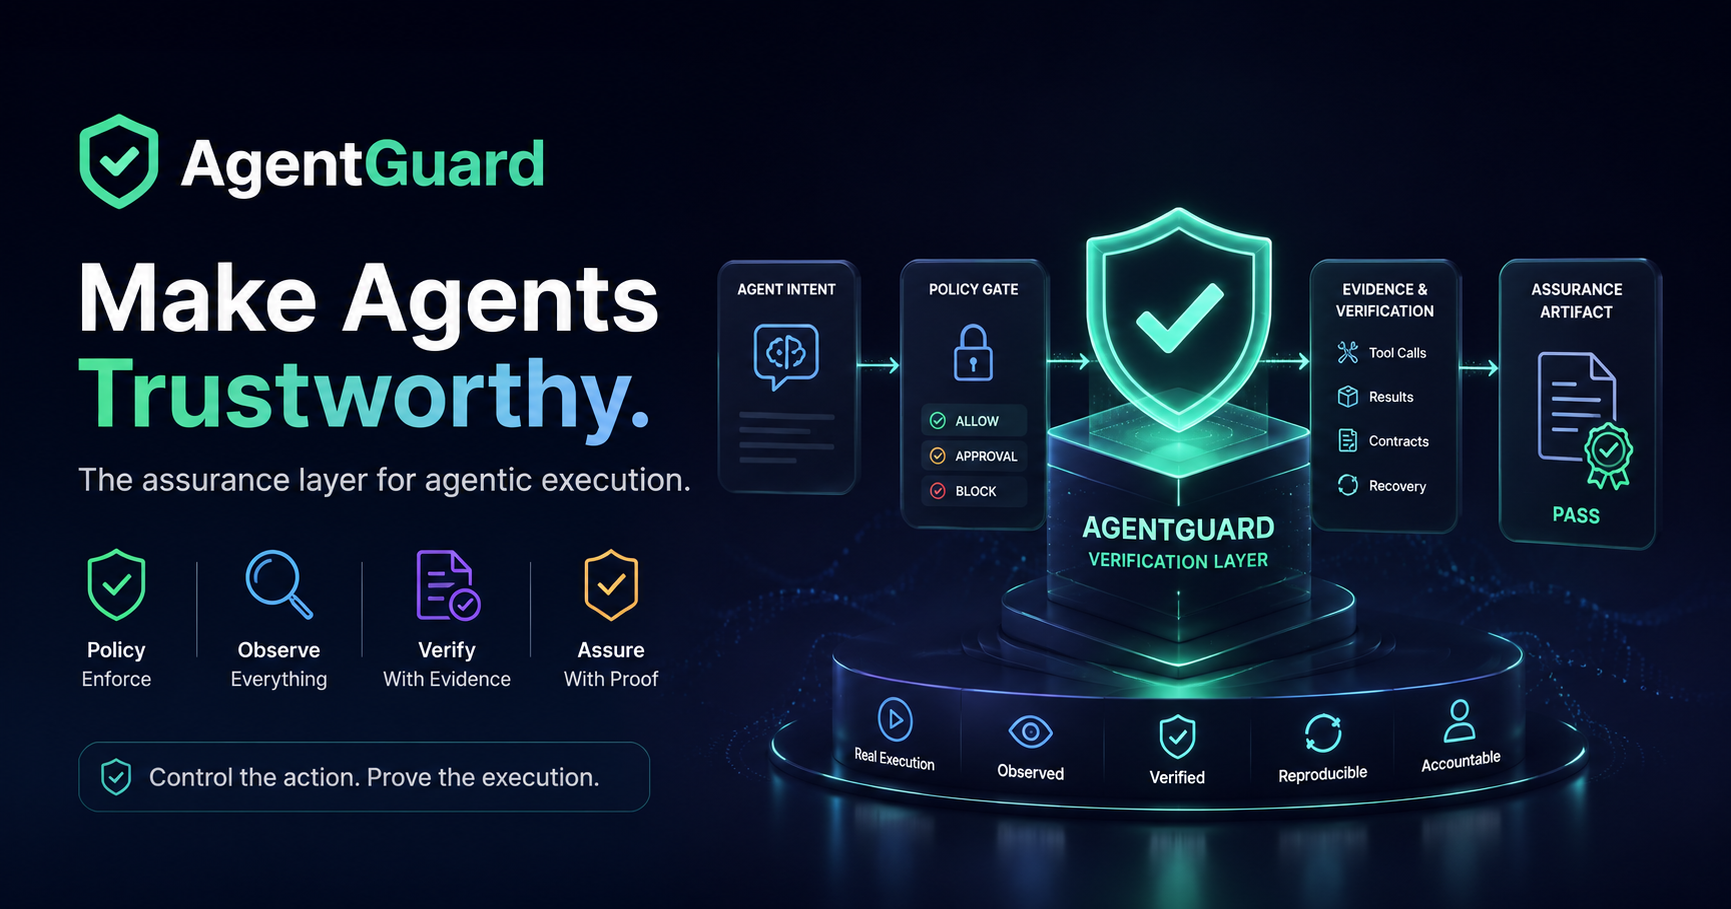
I’d go one step further and make that distinction a first-class invariant in any agent orchestration layer: every consequential action should have a provenance chain from intent → policy decision → execution → observed state → verified outcome. Retries then become part of that chain rather than overwriting the original event.
That model becomes especially valuable with MCP, where the tool boundary is standardized but the consequences behind the tool can be anything from a read-only query to a production mutation. The agent’s final message is just another observation not the source of truth.
Thanks Mateo, exactly the distinction I was aiming for. Treating authorization, execution, and outcome as separate guarantees is central to AgentGuard, especially at the MCP boundary. I really like your point about making the provenance chain a first-class invariant. That's a natural direction for future iterations.
The strongest part here is the separation between “the action was authorized,” “the action executed,” and “the intended outcome actually happened.” Those are three different guarantees, and agent systems often collapse them into one success signal.
I’d go one step further and make that distinction a first-class invariant in any agent orchestration layer: every consequential action should have a provenance chain from intent → policy decision → execution → observed state → verified outcome. Retries then become part of that chain rather than overwriting the original event.
That model becomes especially valuable with MCP, where the tool boundary is standardized but the consequences behind the tool can be anything from a read-only query to a production mutation. The agent’s final message is just another observation not the source of truth.