Better Auth with Next.js 16: proxy.ts, Prisma 7 and Server Actions (Tested Setup)
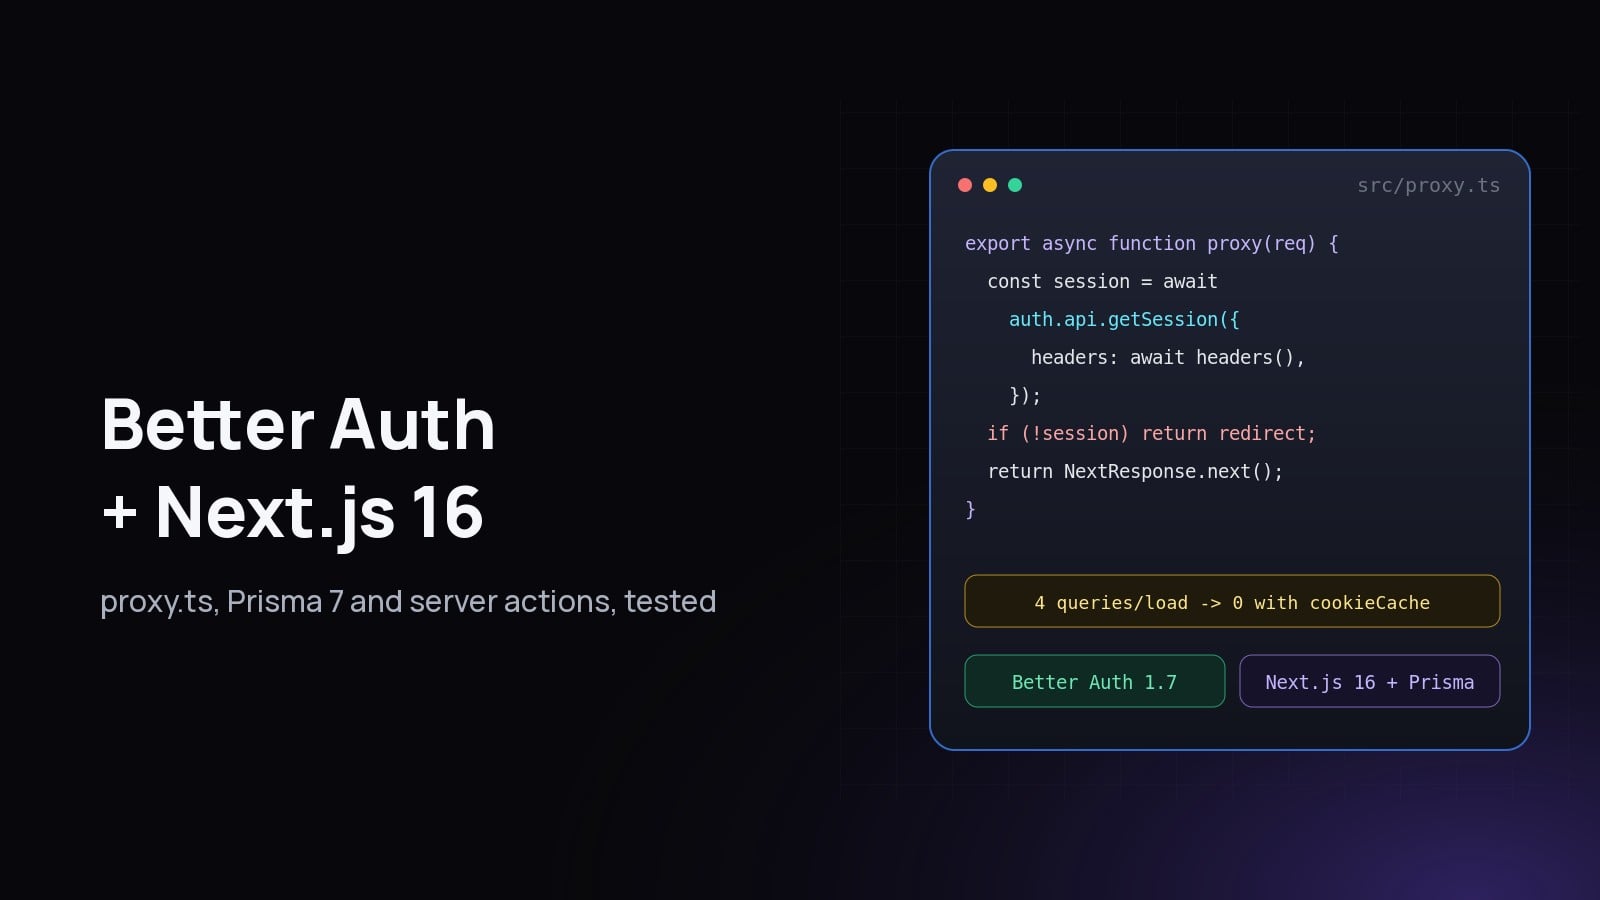
Better Auth is an open-source (MIT) TypeScript authentication library that runs inside your own app and stores users and sessions in your own database. With Next.js 16 you mount one route handler, cal
Responses
Markdown supported · ⌘↵ to post
Tarun Sharma
React.js Frontend Web Developer | Next.js Specialist
The forged-cookie test is a good one to include. On the 4 queries per load: wrapping getSession in React's cache() inside one small data access function lets the layout, page and any server components in the same render share a single lookup. The proxy runs outside that render so it still pays its own, which is another reason to keep it to an optimistic redirect.