The rate limiter is a good example to walk through, because it's exactly where specs earn their keep. One requirement worth adding to that requirements.md: who is exempt, and how the limiter knows.
We found this the hard way this week (I build Mythex, an AI app builder). Our API's per-IP limit counted our own internal services like single users. One sat behind a few shared Cloudflare IPs, another behind one container IP, and on production they started getting 429s on the requests that serve published sites. Nothing in the code was wrong. The spec just never said "internal callers carrying the service token aren't users".
That's the general case for spec-driven work: the bugs that survive are usually missing sentences, not wrong code.
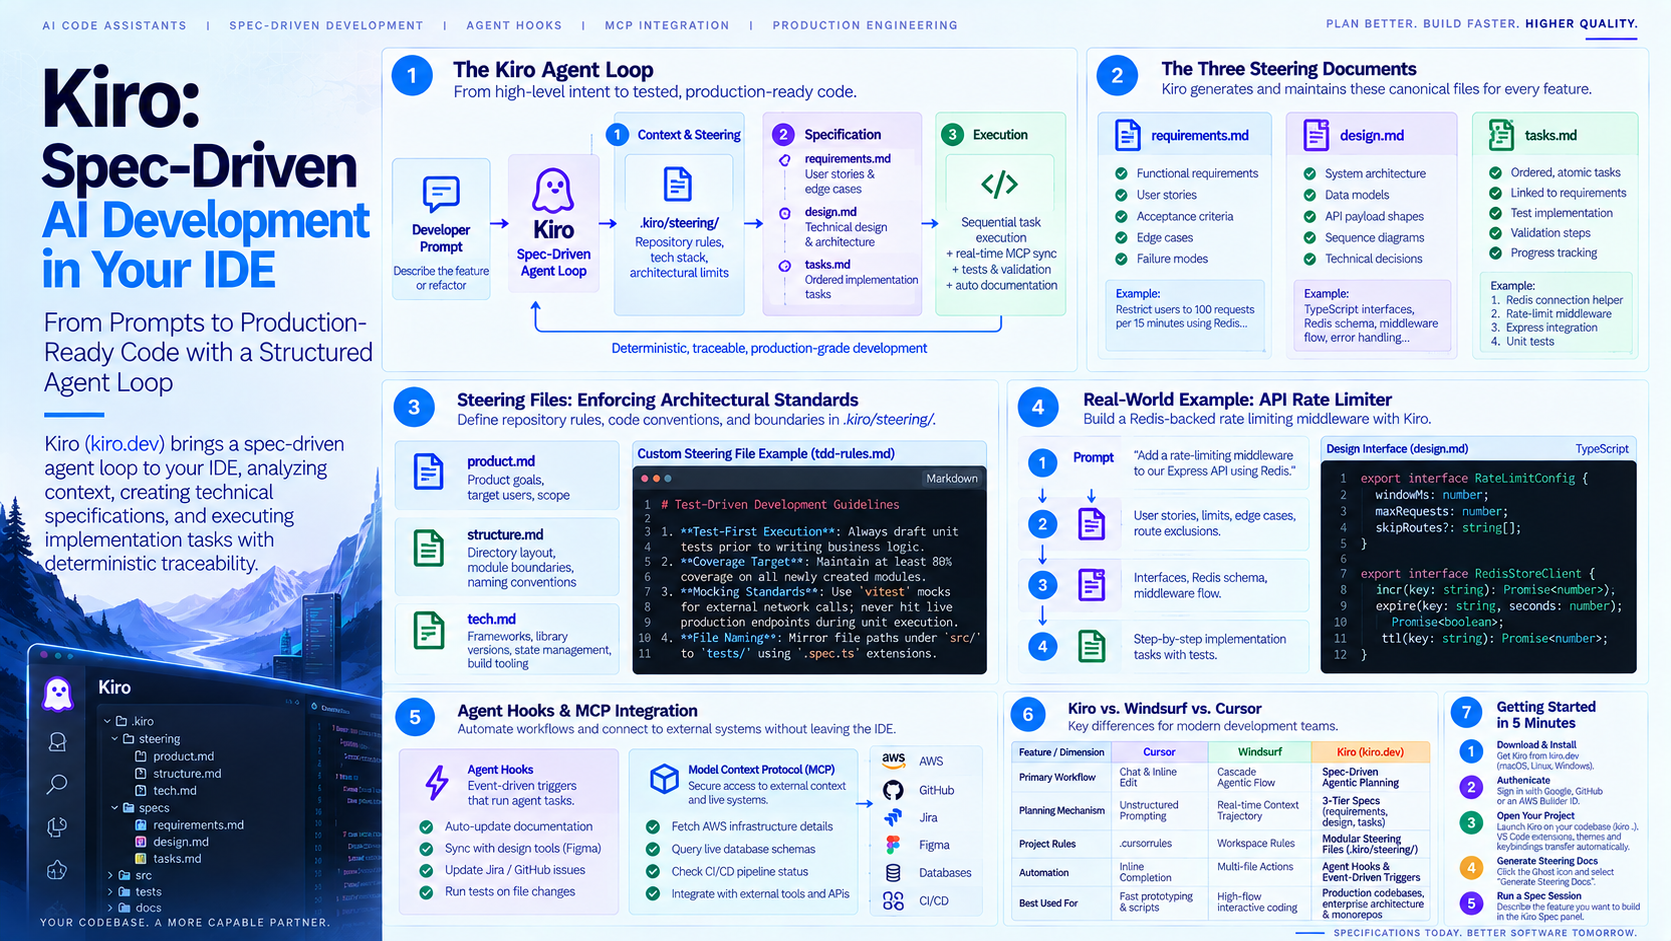
The rate limiter is a good example to walk through, because it's exactly where specs earn their keep. One requirement worth adding to that requirements.md: who is exempt, and how the limiter knows.
We found this the hard way this week (I build Mythex, an AI app builder). Our API's per-IP limit counted our own internal services like single users. One sat behind a few shared Cloudflare IPs, another behind one container IP, and on production they started getting 429s on the requests that serve published sites. Nothing in the code was wrong. The spec just never said "internal callers carrying the service token aren't users".
That's the general case for spec-driven work: the bugs that survive are usually missing sentences, not wrong code.