Feed
Discussion
Catching over-permissive IAM in the pull request, not in production
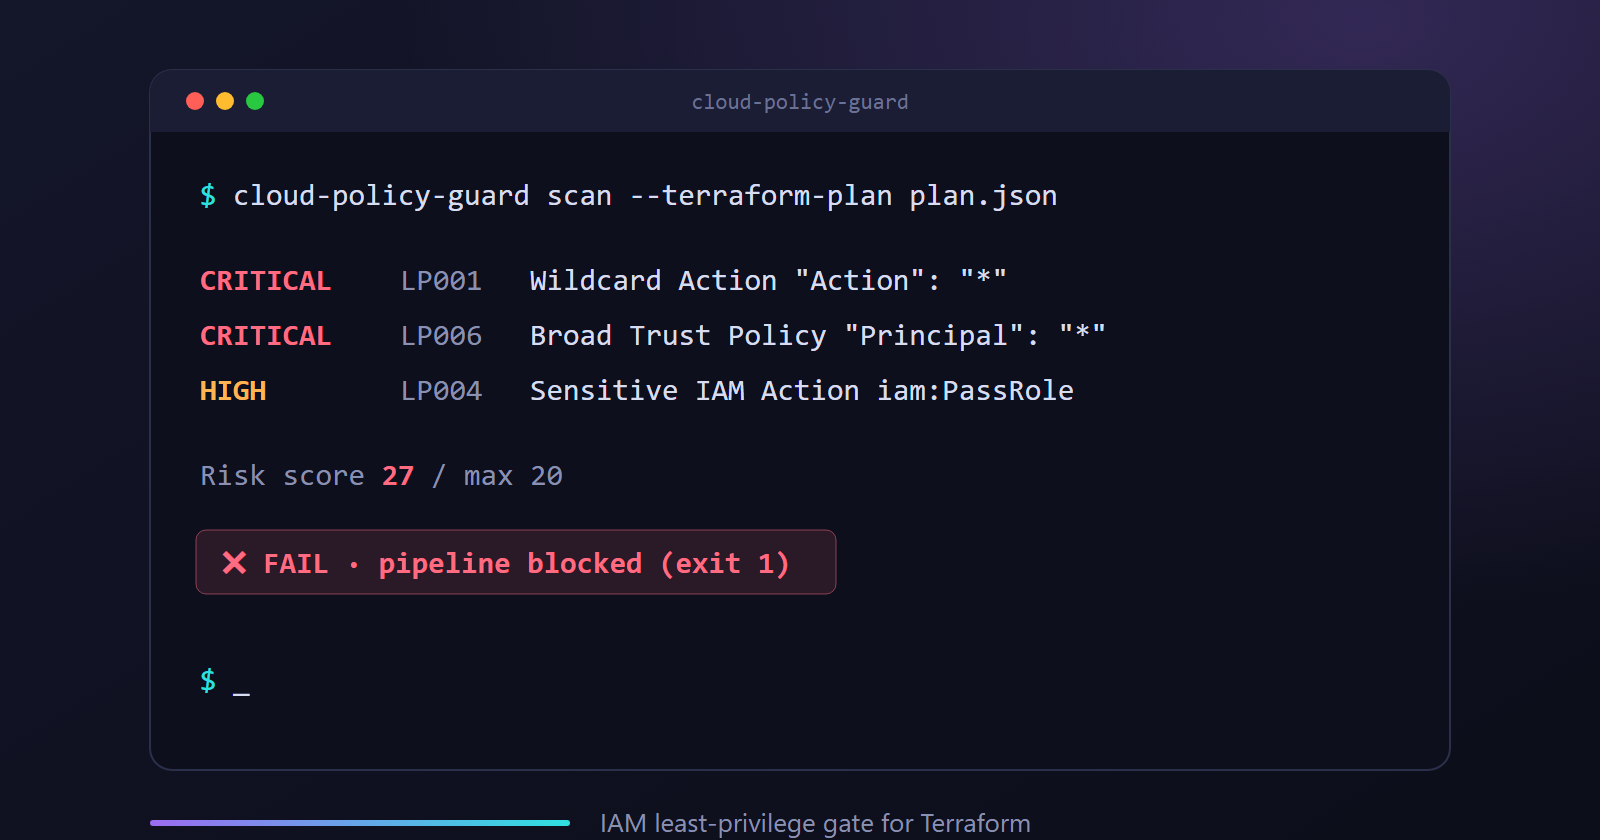
Over-permissive IAM is one of the most common AWS misconfigurations: "Action": "*", iam:PassRole granted on every resource, a trust policy with "Principal": "*". The problem is usually found during an
Responses
Markdown supported · ⌘↵ to post
No responses yet.