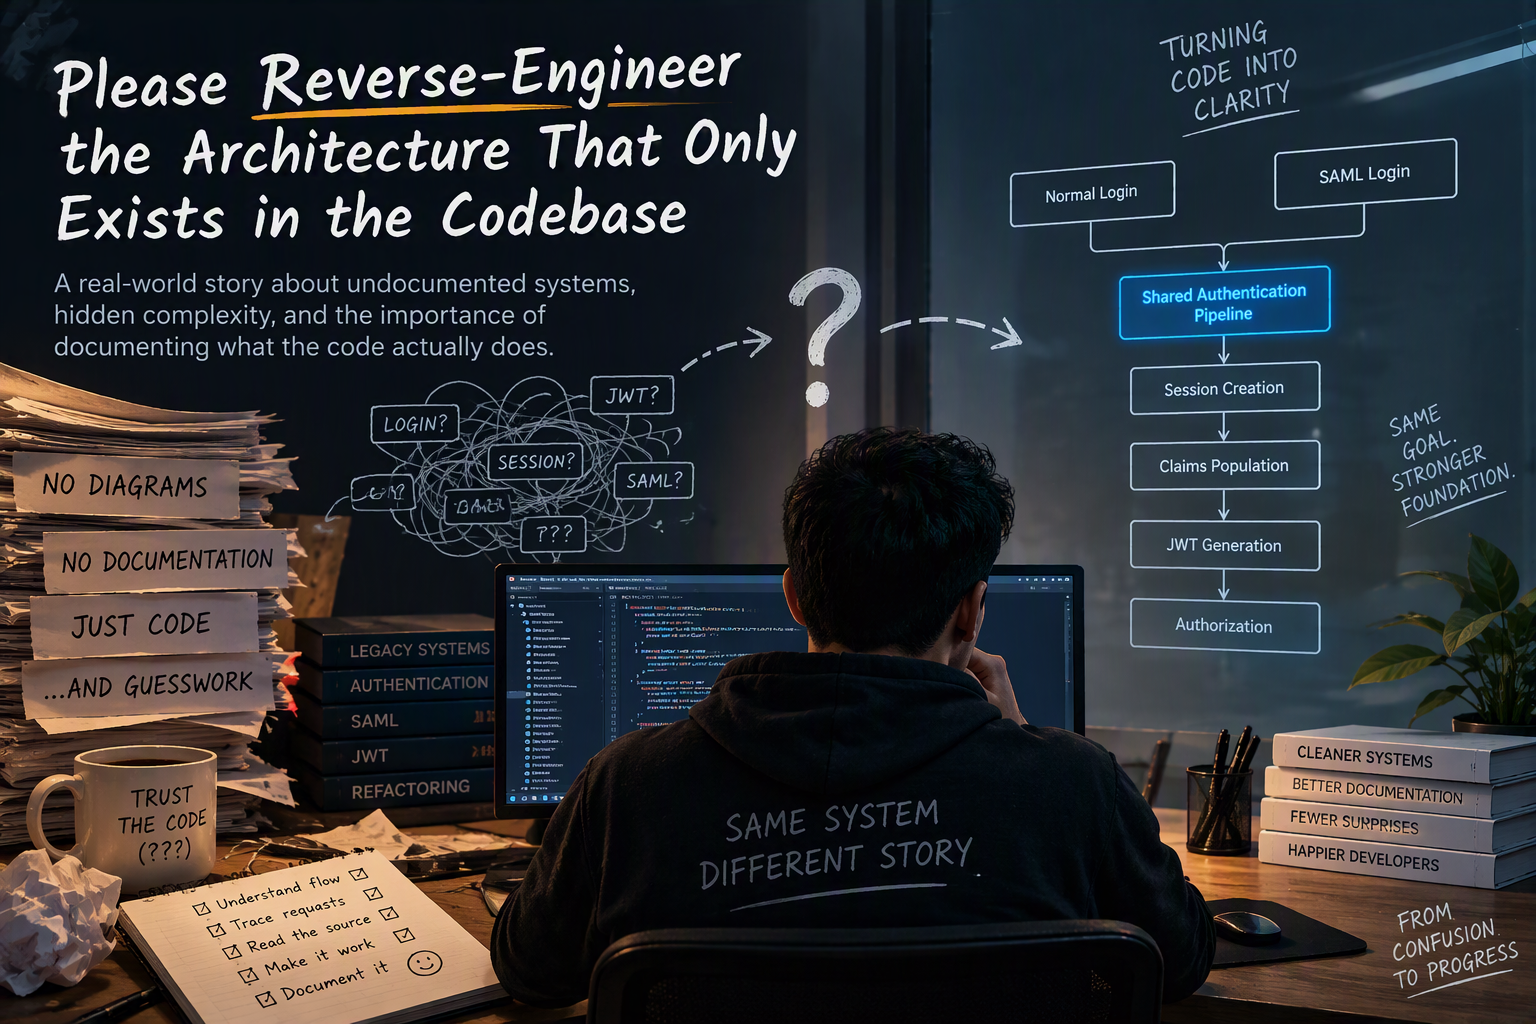
Please Reverse-Engineer the Architecture That Only Exists in the Codebase
I recently got assigned what sounded like a simple authentication task: Make tokens generated by a legacy API and a refactored API interoperable. I thought: JWT + Shared signing key + Shared validat
Written by
Amateurs practice till they get it right, professionals practice till they can't get it wrong -Unknown
I'm a highly motivated and experienced developer expertise in leveraging the power of .NET Core Technology. Currently collaborating with an Australian company based in Nusa Dua, Bali, Indonesia, to deliver innovative application development services that push the boundaries of what technology can achieve, and also contribute to the ever-evolving landscape of the global IT industry
Responses
Markdown supported · ⌘↵ to post
No responses yet.