I’ve found that giving an agent too much access is easy to overlook when you’re trying to ship fast. Keeping it locked to the project folder feels like a simple win.
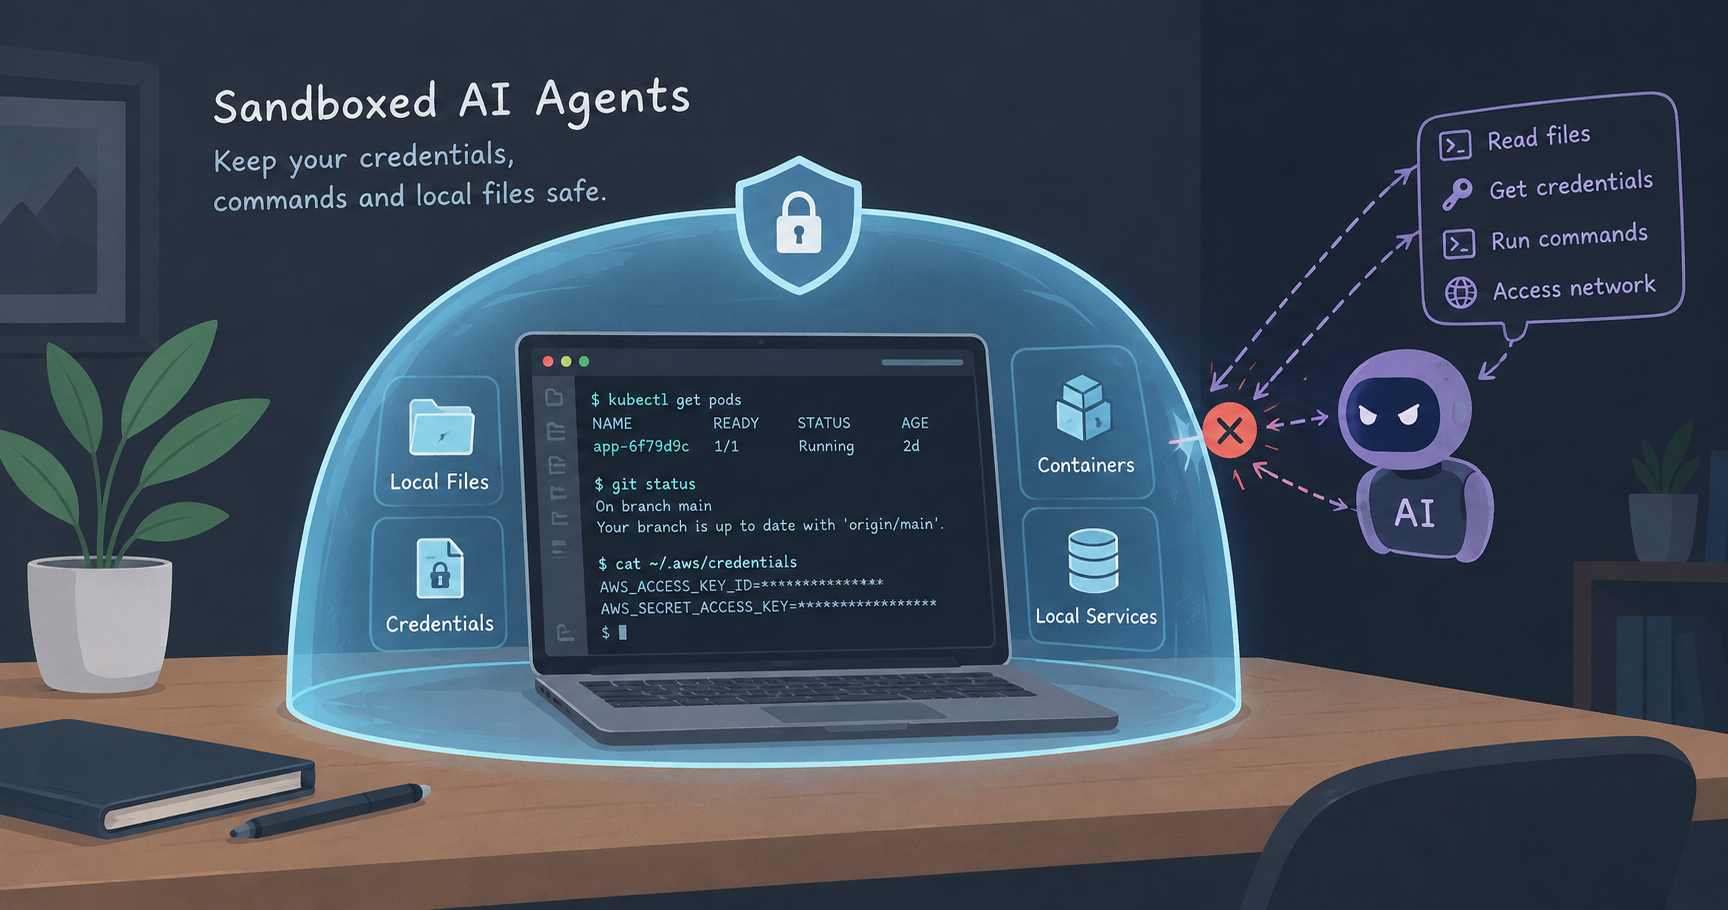
Thank for sharing this article. What convinces me most is exactly this: some rules should not be entrusted to the agent. If Claude Code must not read ~/.kube or touch certain directories, I would rather have the operating system prevent it than hope a policy in the prompt is always respected. A prompt injection or a misinterpreted command is enough to change the problem quite a bit. Here, sandboxing almost seems more important than the model itself.
Nube Colectiva
NC
Interesting, thanks for sharing 👍🏼