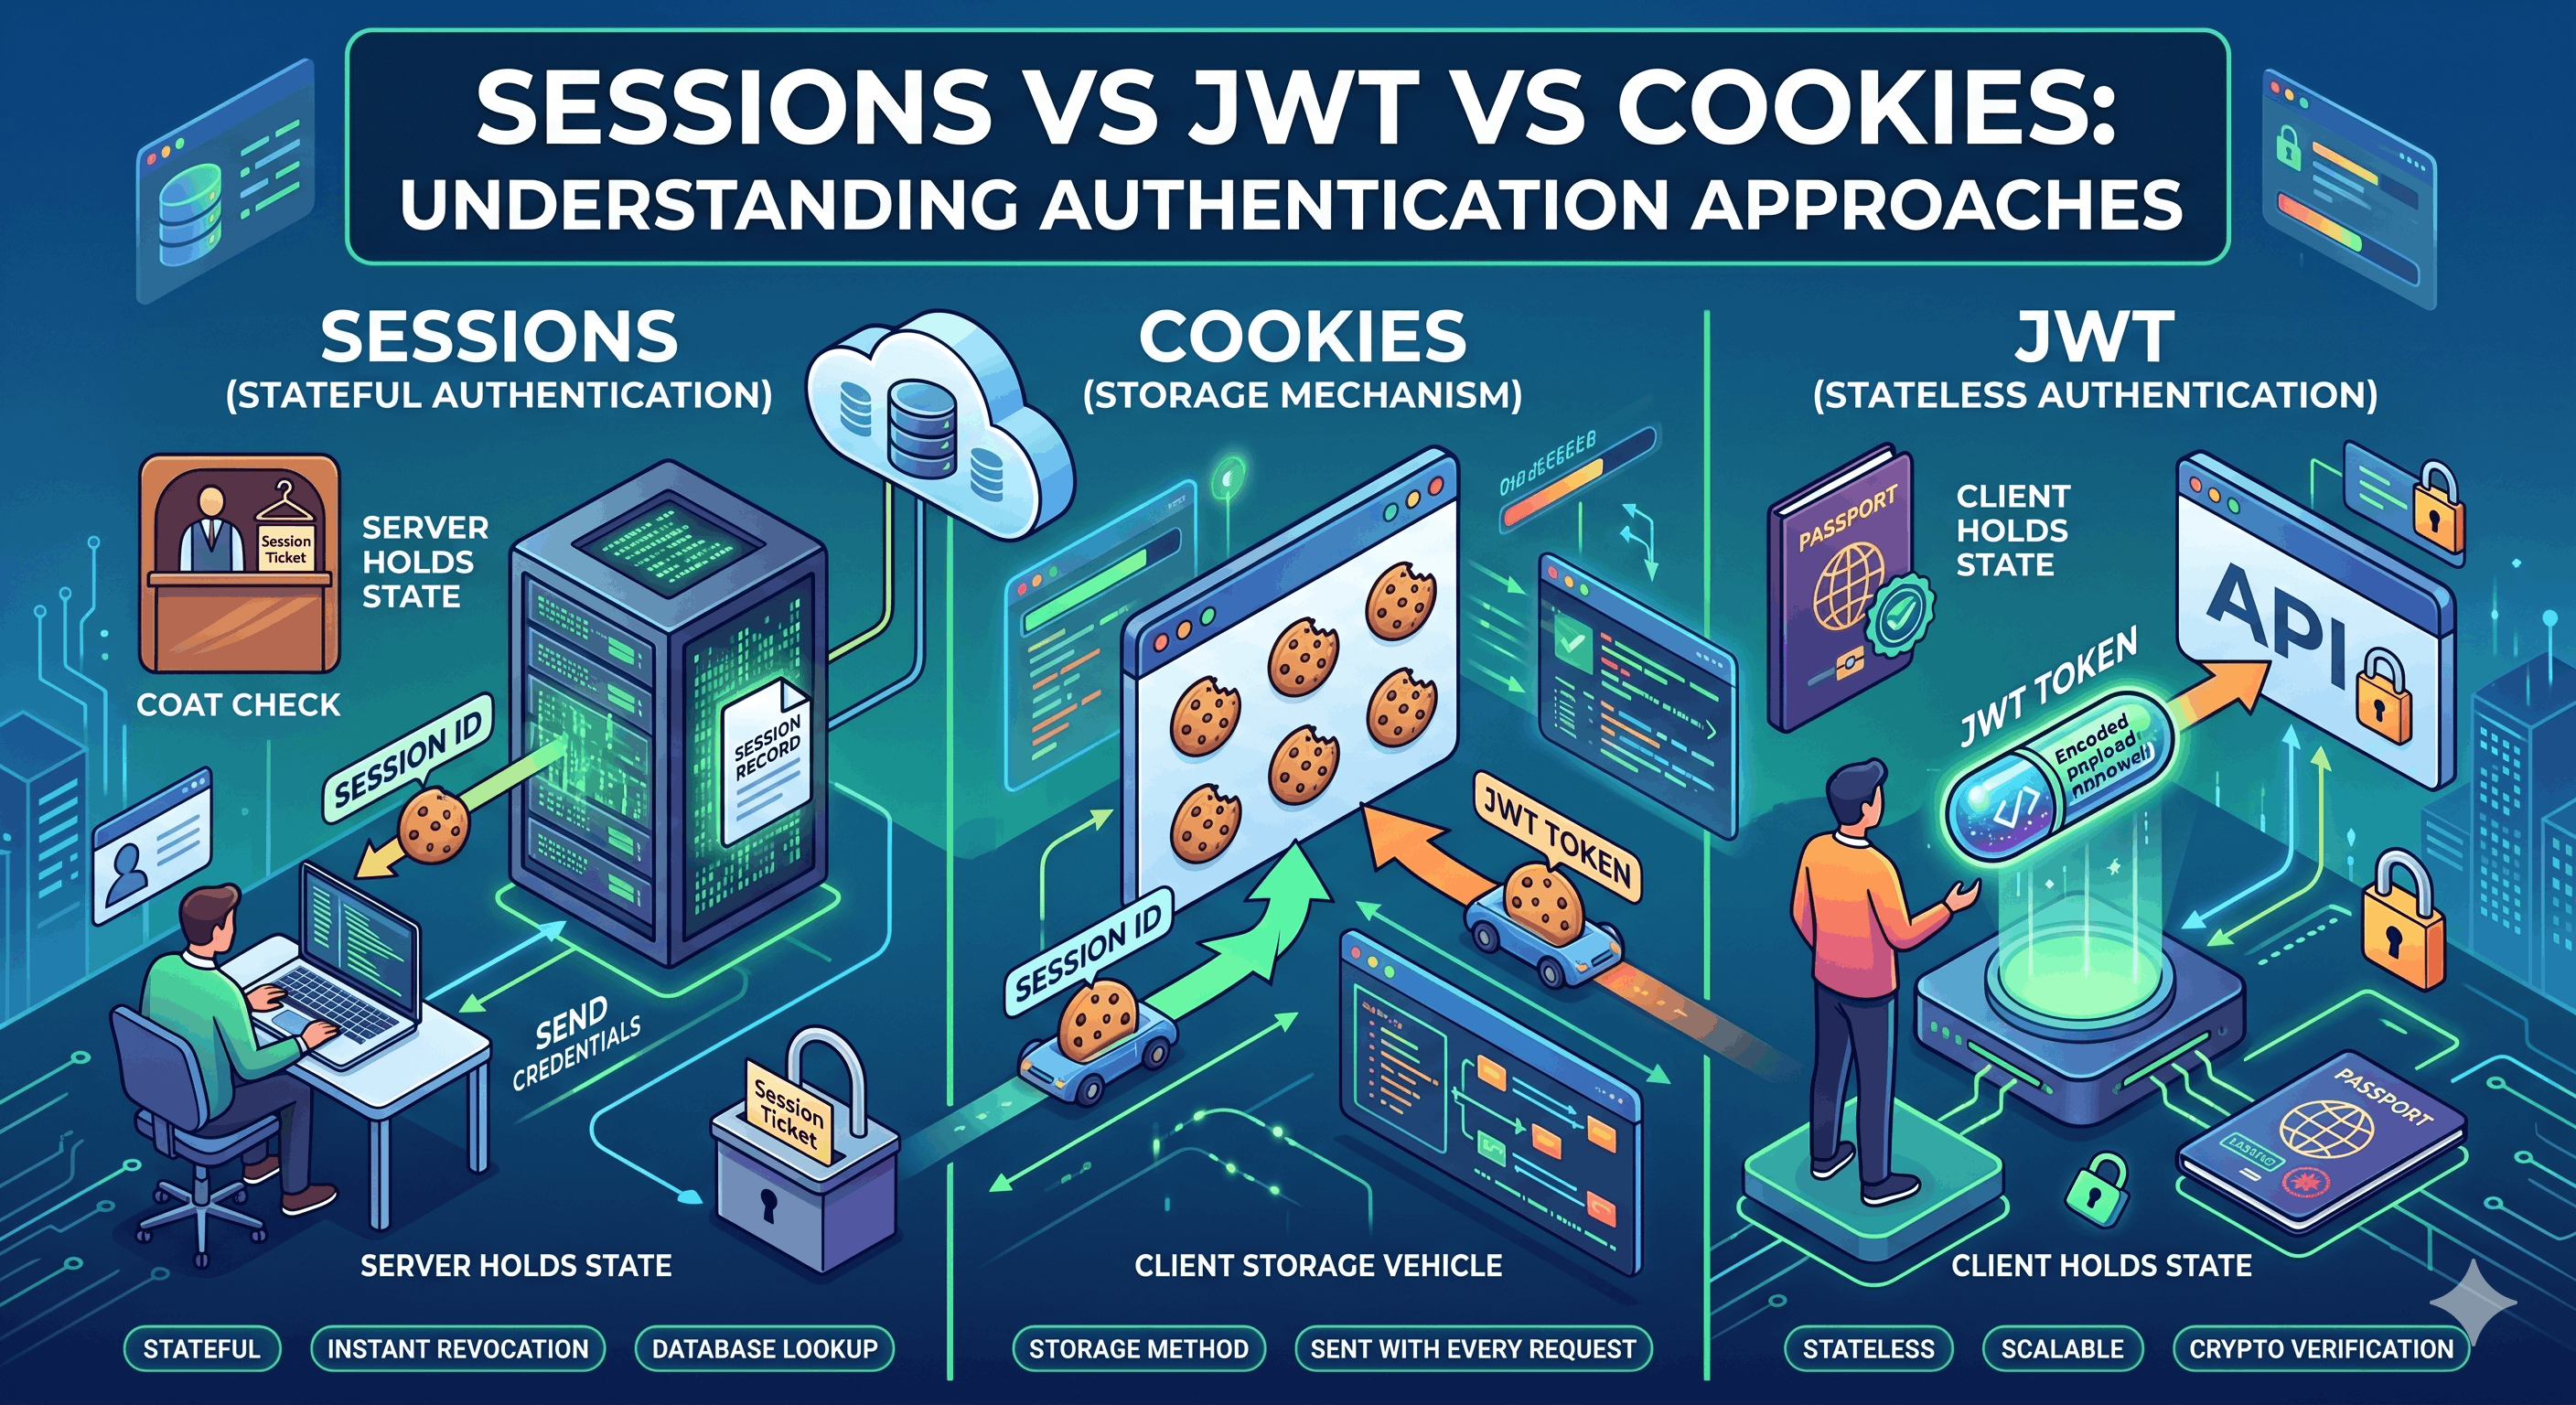
Sessions vs JWT vs Cookies: Understanding Authentication Approaches
In the early days of the web, every request was a fresh start. You’d log in, click a link, and the server would immediately forget who you were. This is because HTTP is stateless—it doesn't naturally
javascripttopics.hashnode.dev4 min read