Ppraveeninthecoderegistry.hashnode.dev·Sep 22 · 11 min readTop 20 Tools for Enterprises to Assess Overall Software RiskA codebase with zero open CVEs can still sink a release or stall an M&A deal. If your application has pristine vulnerability scan reports but runs on an unmaintained framework, relies on a single engi00
Ppraveeninthecoderegistry.hashnode.dev·Sep 19 · 36 min readTop 20 Software Due Diligence Tools Compared (2026)Executive Summary Software due diligence is frequently reduced to a single question: “did the scanner find any vulnerabilities?” That question is necessary but not sufficient. A vulnerability count sa00
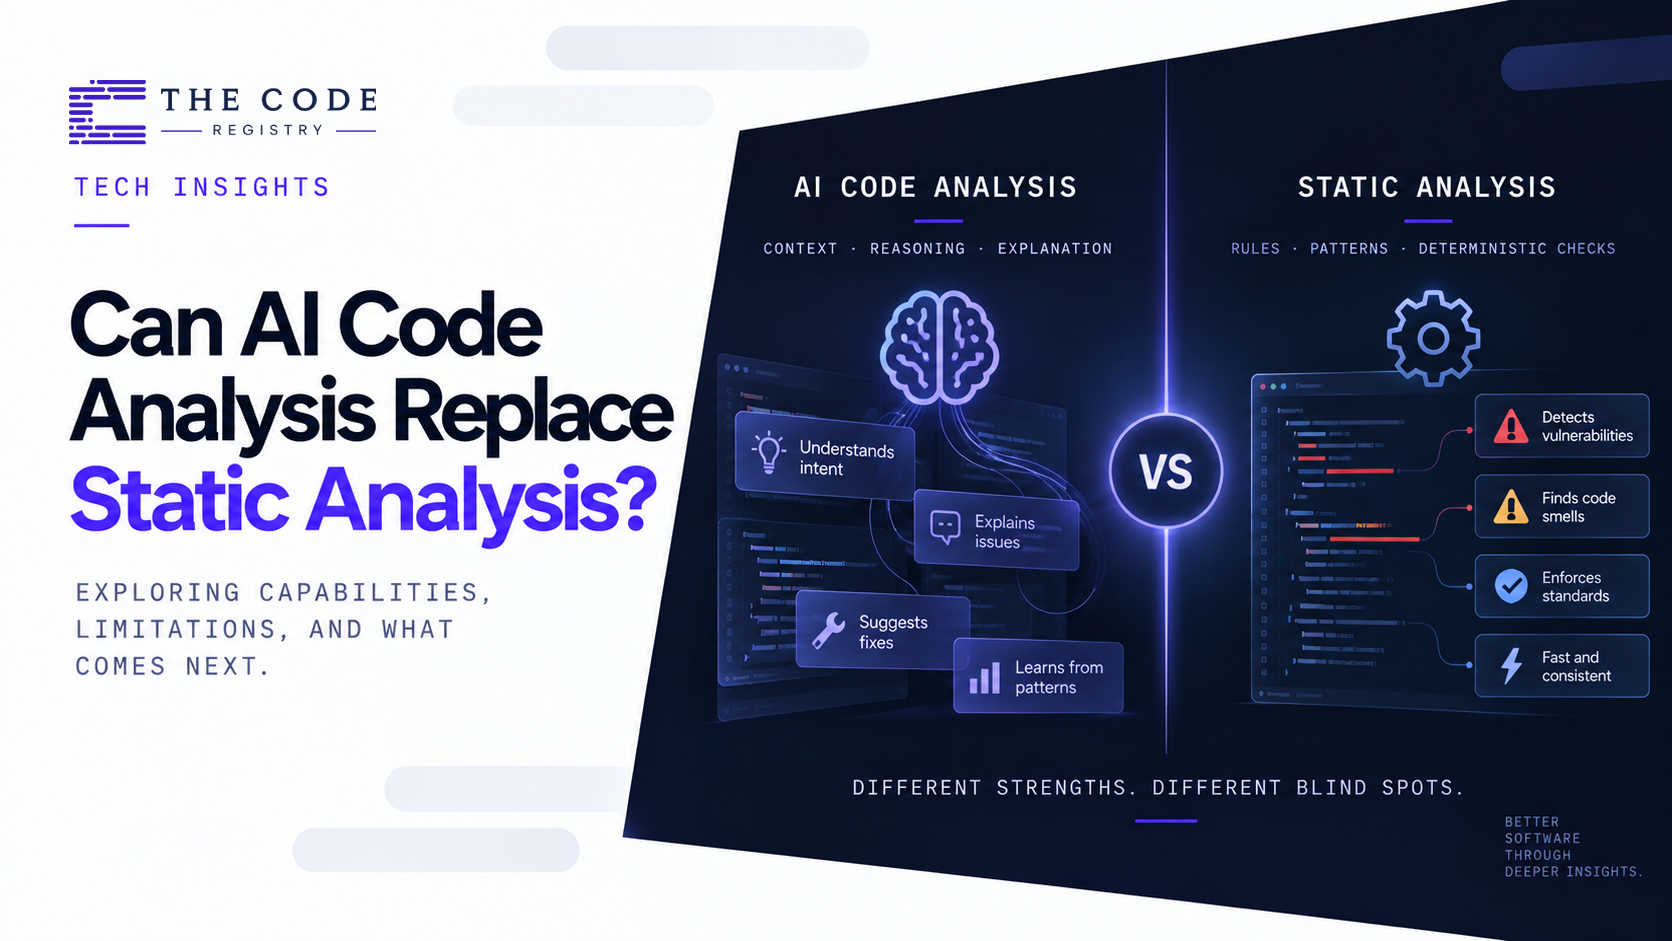
Ppraveeninthecoderegistry.hashnode.dev·Sep 15 · 33 min readCan AI Code Analysis Replace Static Analysis?Modern enterprise software assurance has reached an inflection point driven by generative models, autonomous coding agents, and algorithmic code synthesis. As machine learning models demonstrate the a00
Ppraveeninthecoderegistry.hashnode.dev·Sep 11 · 24 min readStatic Analysis vs Dynamic Analysis vs AI Code AnalysisSoftware analysis used to be relatively straightforward. Developers wrote code, static analysis scanned it, security teams tested the running application, and code reviewers evaluated important change11V
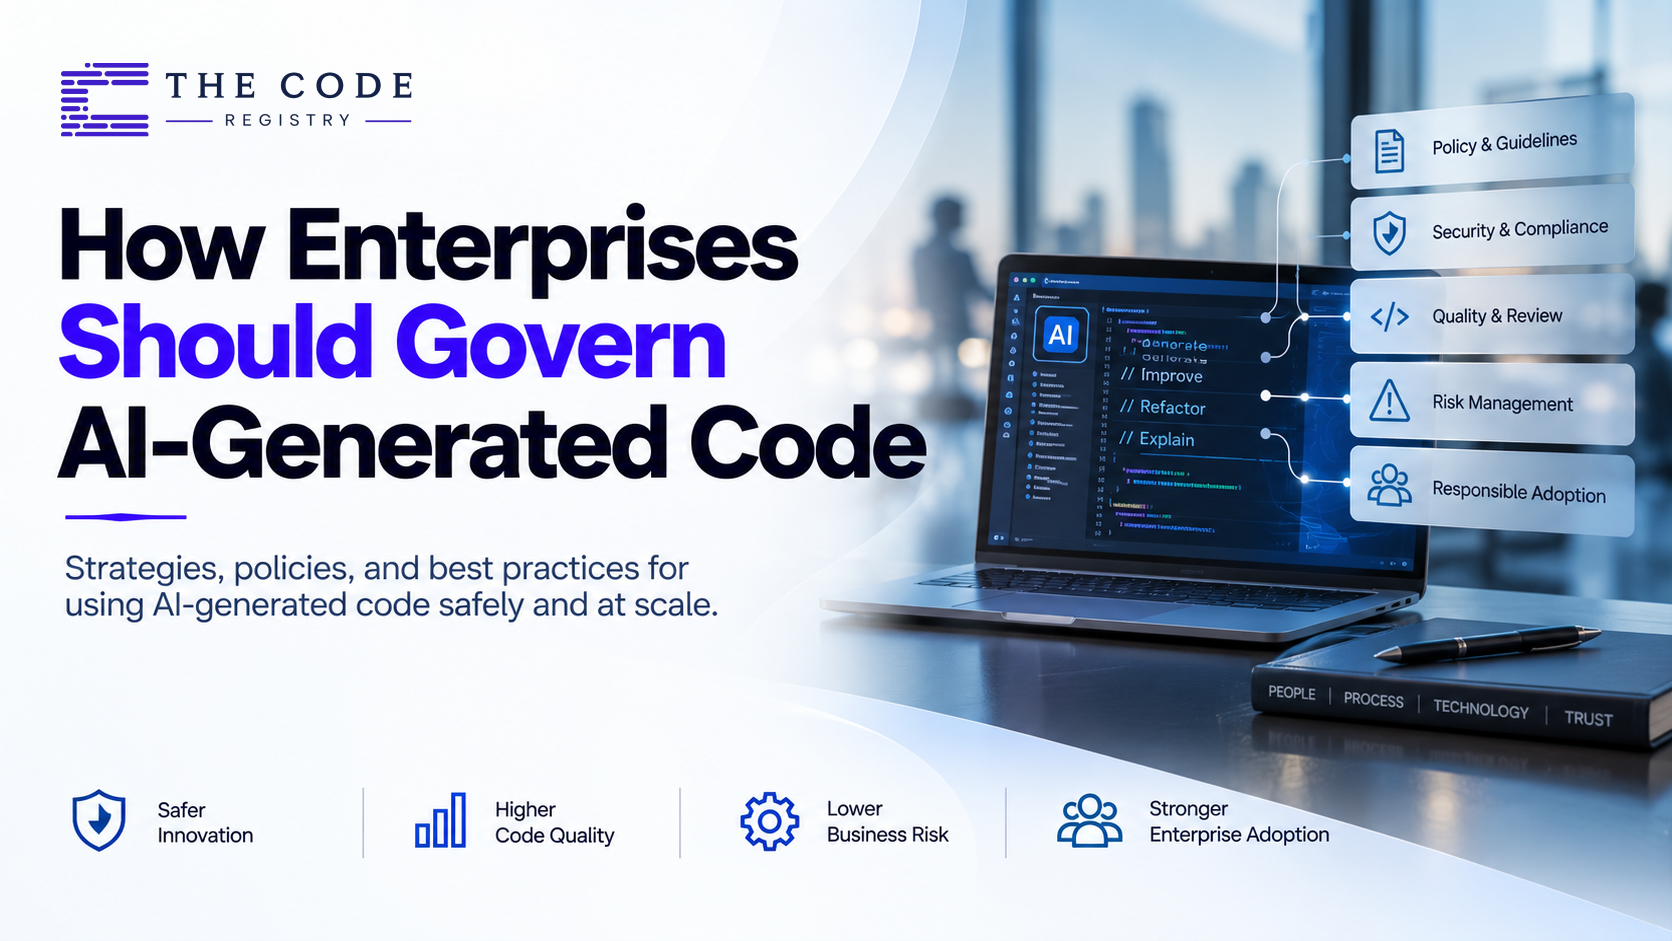
Ppraveeninthecoderegistry.hashnode.dev·Sep 9 · 31 min readHow Enterprises Should Govern AI-Generated CodeSoftware engineering is undergoing an irreversible structural transition. Where developers previously designed and hand-typed logic from scratch, engineering workflows now operate alongside large lang00