Delegated authorization is the right framing. Giving an agent the share link is equivalent to giving it the full credential. What makes this production-ready is scoping the delegation to exactly the intended action: a capability token authorizing 'share this file once to this recipient' rather than possession of the raw link. Same principle as session keys and per-call spending limits in programmable wallets.
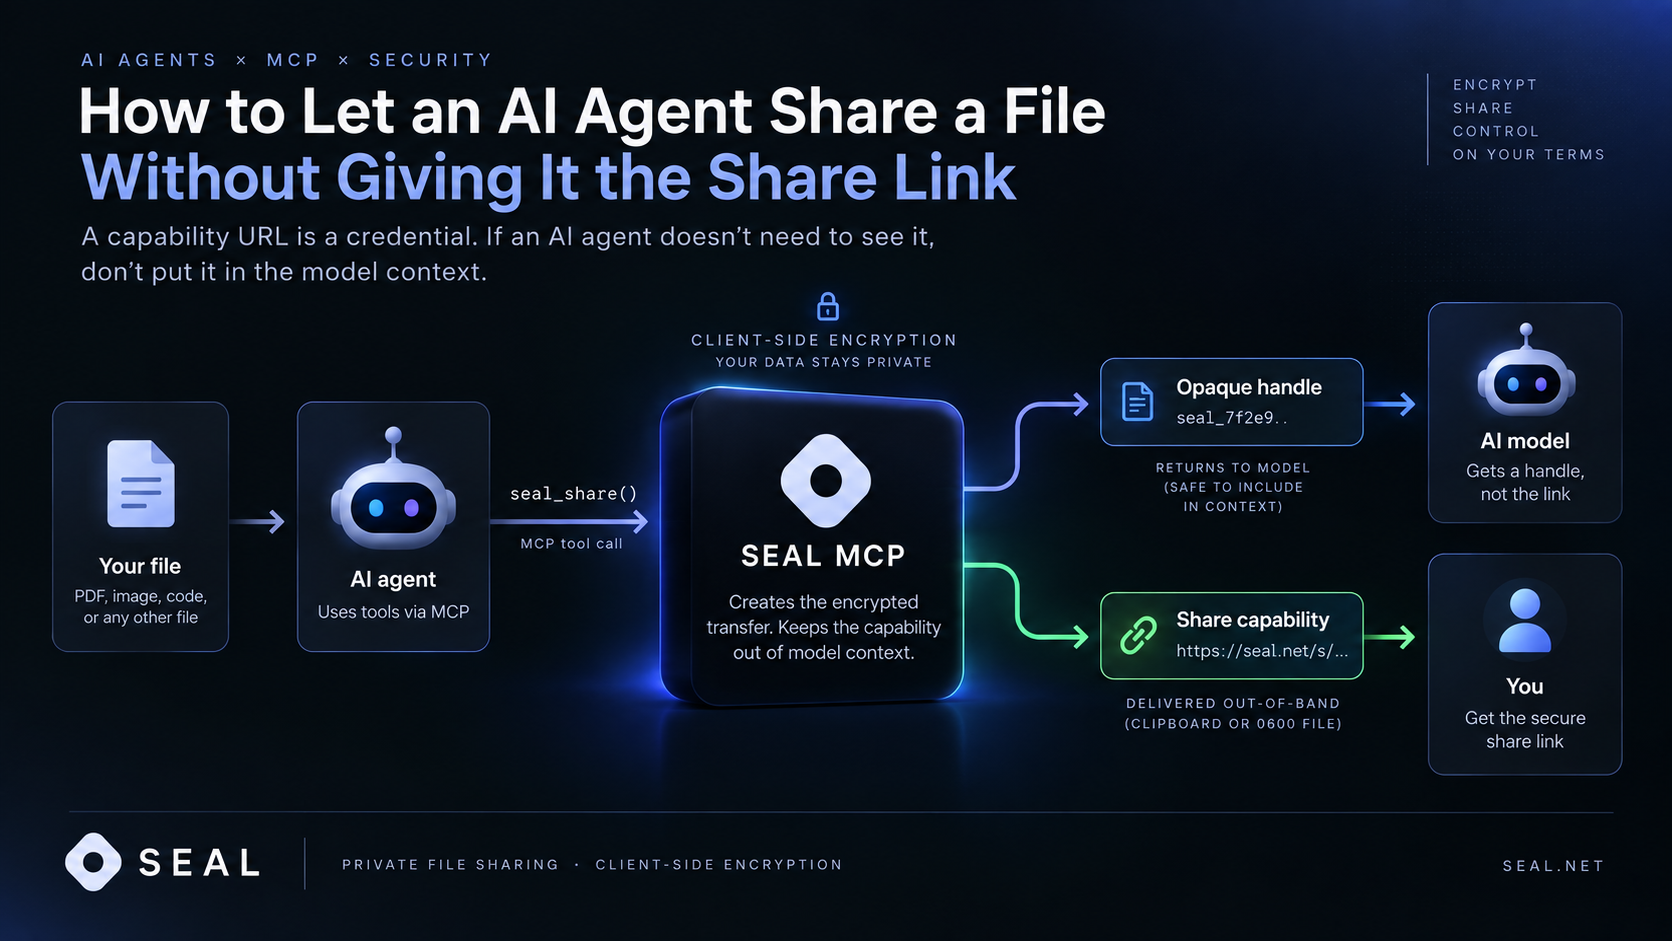
Exactly—the boundary between a reusable credential and a narrowly scoped authorization matters. Capability tokens scoped to one recipient and one action are a strong design pattern, but we’re not presenting that mechanism as production-ready in SEAL today. The narrower point of the article is that the model should not receive more credential material than the task requires. Thanks for sharpening that distinction.
Cai
A custodial email, a stablecoin wallet, a credential vault, and an agent-ready API — all at one @cai.com address.
Delegated authorization is the right framing. Giving an agent the share link is equivalent to giving it the full credential. What makes this production-ready is scoping the delegation to exactly the intended action: a capability token authorizing 'share this file once to this recipient' rather than possession of the raw link. Same principle as session keys and per-call spending limits in programmable wallets.