YPYuri Pocepaevinbadbat4560.hashnode.dev·5h ago · 8 min readPrevent Context Leakage in Multi-Tenant LLM SystemsTwo users can ask the same question and be entitled to completely different answers. “Summarize the renewal terms” might refer to a public template, a private contract, or a document shared with only 00
IIliyainblog.iliyadindar.site·3h ago · 8 min readIntigriti September 2026 Challenge, Critter GalleryVulnerability: Unauthenticated SQL injection (MySQL 8.0.46) in the base64-encoded pic parameter of /challenge.php, exploited with a single-column UNION SELECT to read the secret_vault table. TL;DR /c00
TOTapbit Officialintapbitofficial.hashnode.dev·18m ago · 9 min readHow Seed Phrases Rebuild HD Wallets: Entropy, Checksums, BIP-39, and Derivation PathsA seed phrase looks like a short list of ordinary words. Underneath, it is a portable representation of random data that wallet software can transform into a deterministic tree of cryptographic keys. 00
HHackitainfreecodecamp.org·27m ago · 10 min readHow ORMs Still Let SQL Injection Through (and How to Close the Gaps)A lot of developers assume that once they're on an ORM, SQL injection stops being their problem. But it doesn't disappear. It just relocates. ORMs like Sequelize, Prisma, TypeORM, and Knex parameteriz00
KAKayode Adeniyiinfreecodecamp.org·42m ago · 42 min readHow to Govern AI-Generated Infrastructure with Policy as Code and OPA [Full Handbook]Modern models generate syntactically correct code nearly 100% of the time. Veracode's 2026 report puts it plainly: "Syntax is effectively solved." That reads like a milestone, but it's the reason you 00
ABAuth By Exampleinauthbyexample.hashnode.dev·47m ago · 2 min readAuthorization needs fresh attributes, not yesterday's snapshotMost ABAC bugs I see are not bad rules. They are stale inputs. The policy says something like "finance can edit records tagged confidential, but only during business hours." That looks fine in a desig00
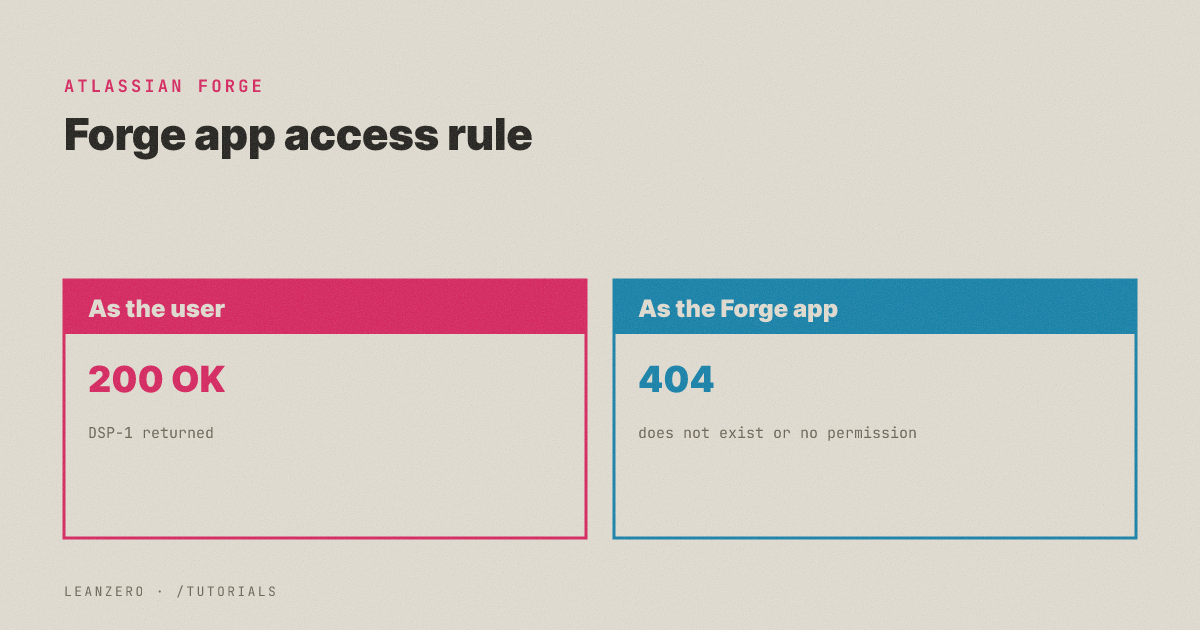
MMihai_LeanZeroinleanzero.hashnode.dev·2h ago · 23 min readForge App Access Rule: Handle Blocked ContentA Forge app access rule is the part of an Atlassian data security policy that blocks Marketplace and custom apps from content in chosen Jira projects or Confluence spaces. When an admin turns it on, y00
AAnandinanandms101.hashnode.dev·2h ago · 17 min readThe Model Is Untrusted Code: A Design Review of Meta's MuseYou ask a personal agent to prepare notes for tomorrow's meetings. It reads your calendar, pulls the related email threads, and opens your project notes. One thread came from outside your organization00
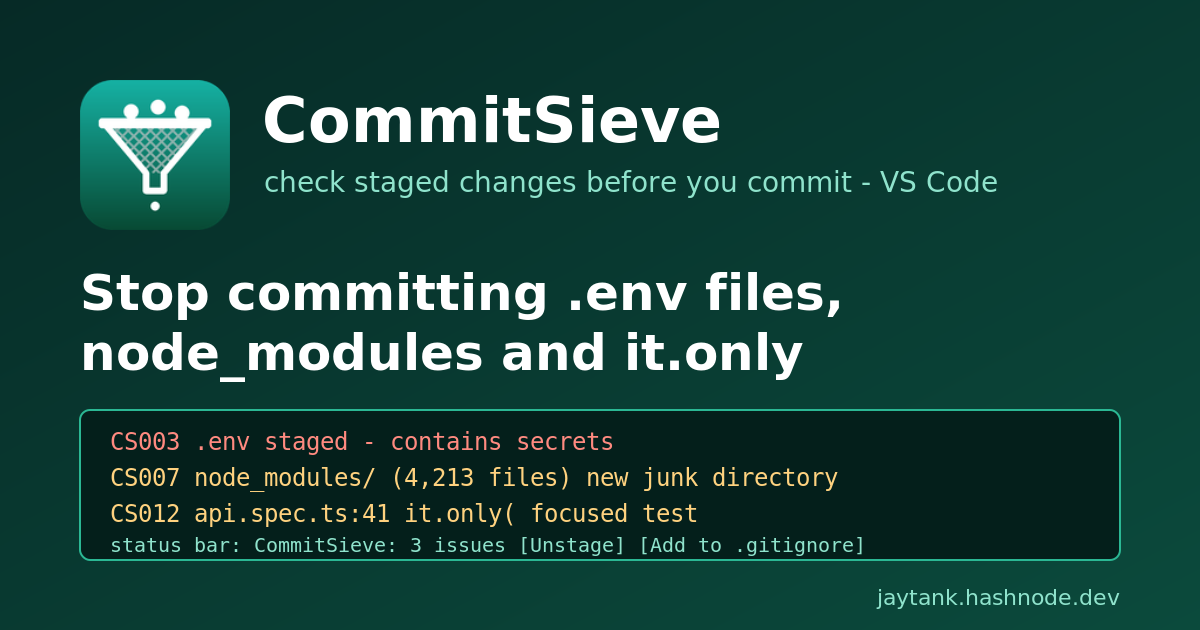
JTJAY TANKinjaytank.hashnode.dev·3h ago · 10 min readStop committing .env files, node_modules and it.only: check your staged changes before you press CommitIt is the end of the day, the fix finally works, and you click the + next to "Changes" to stage everything. You type "fix login redirect", press Commit, push, and close the laptop. The next morning yo00
SSSarmeet Singhinblueprintsofscale.hashnode.dev·3h ago · 58 min readAssume They're Already Knocking: Security and Abuse at Scale, Explained Like You're NewIn the URL shortener post, the interviewer asked the meanest question near the end. The design was done, sharded and cached and replicated across regions, and then: "Your Base62 keys are sequential. I00