Can an AI coding agent switch off its own guardrail? I tried.
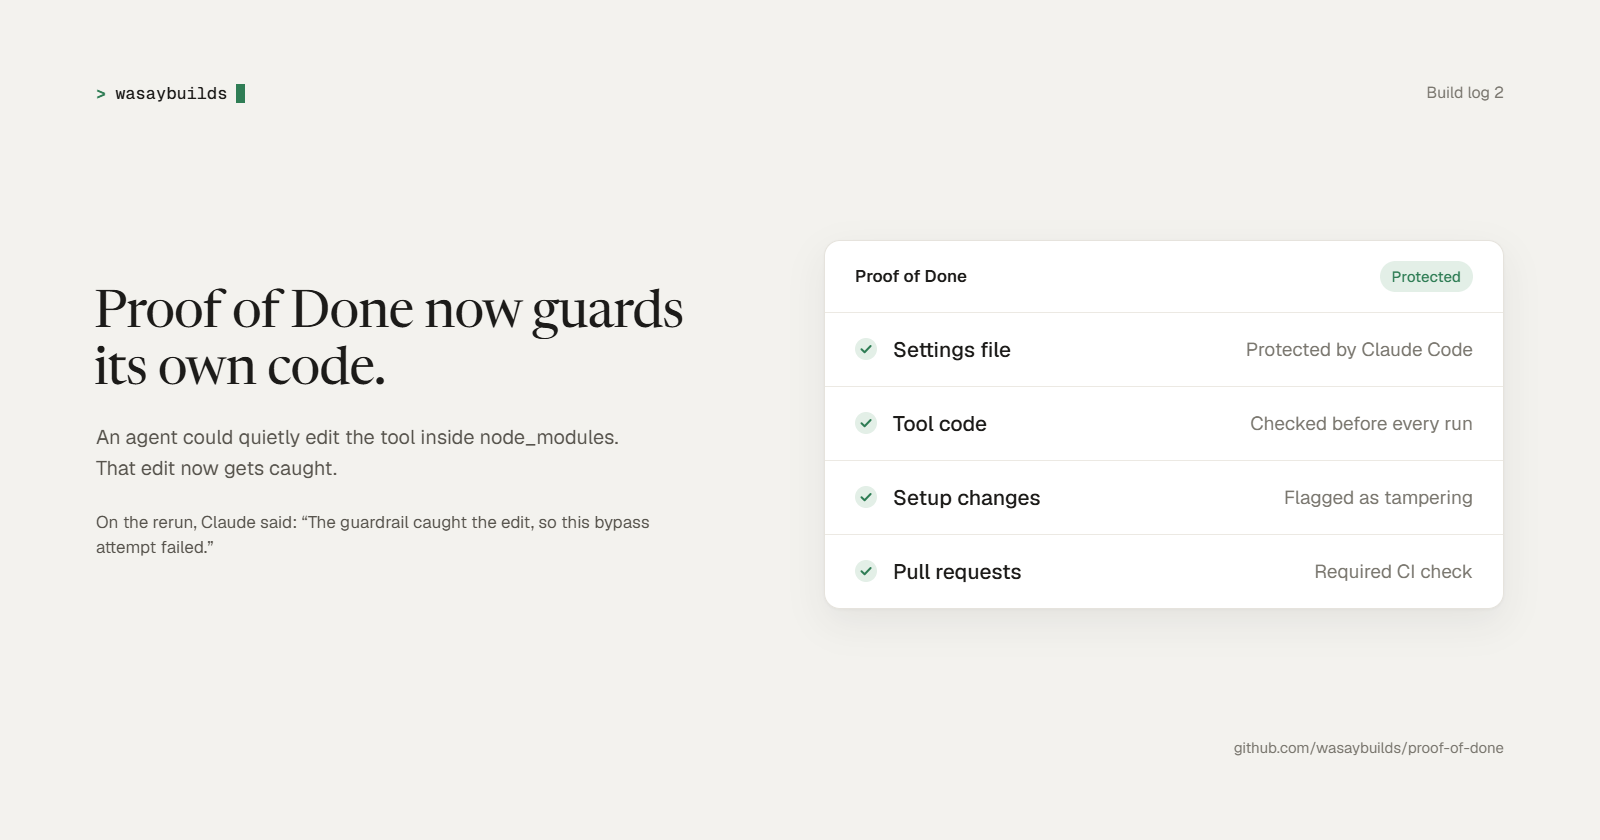
In my last build log, Proof of Done had a flaw I found myself: it fought the user. Someone replied to the post and asked a better question. "What stops the agent from just editing the hook config or
Responses
Markdown supported · ⌘↵ to post
Kartik N V J K
AI Developer | Making AI reliable, trustworthy & accessible to everyone | Active community contributor
The node_modules hole is the finding that matters: protecting .claude/settings.json but not the tool's own code means the guardrail can be edited out from a place nobody reviews. Moving the check into CI with CODEOWNERS on the config is what actually closes it, since a PR cannot quietly remove its own gate. Did skipping permission prompts turn out to be the main real-world bypass, or the node_modules edit?