Feed
Discussion
Building BCB CRM: A Lead Management System with Laravel and MySQL
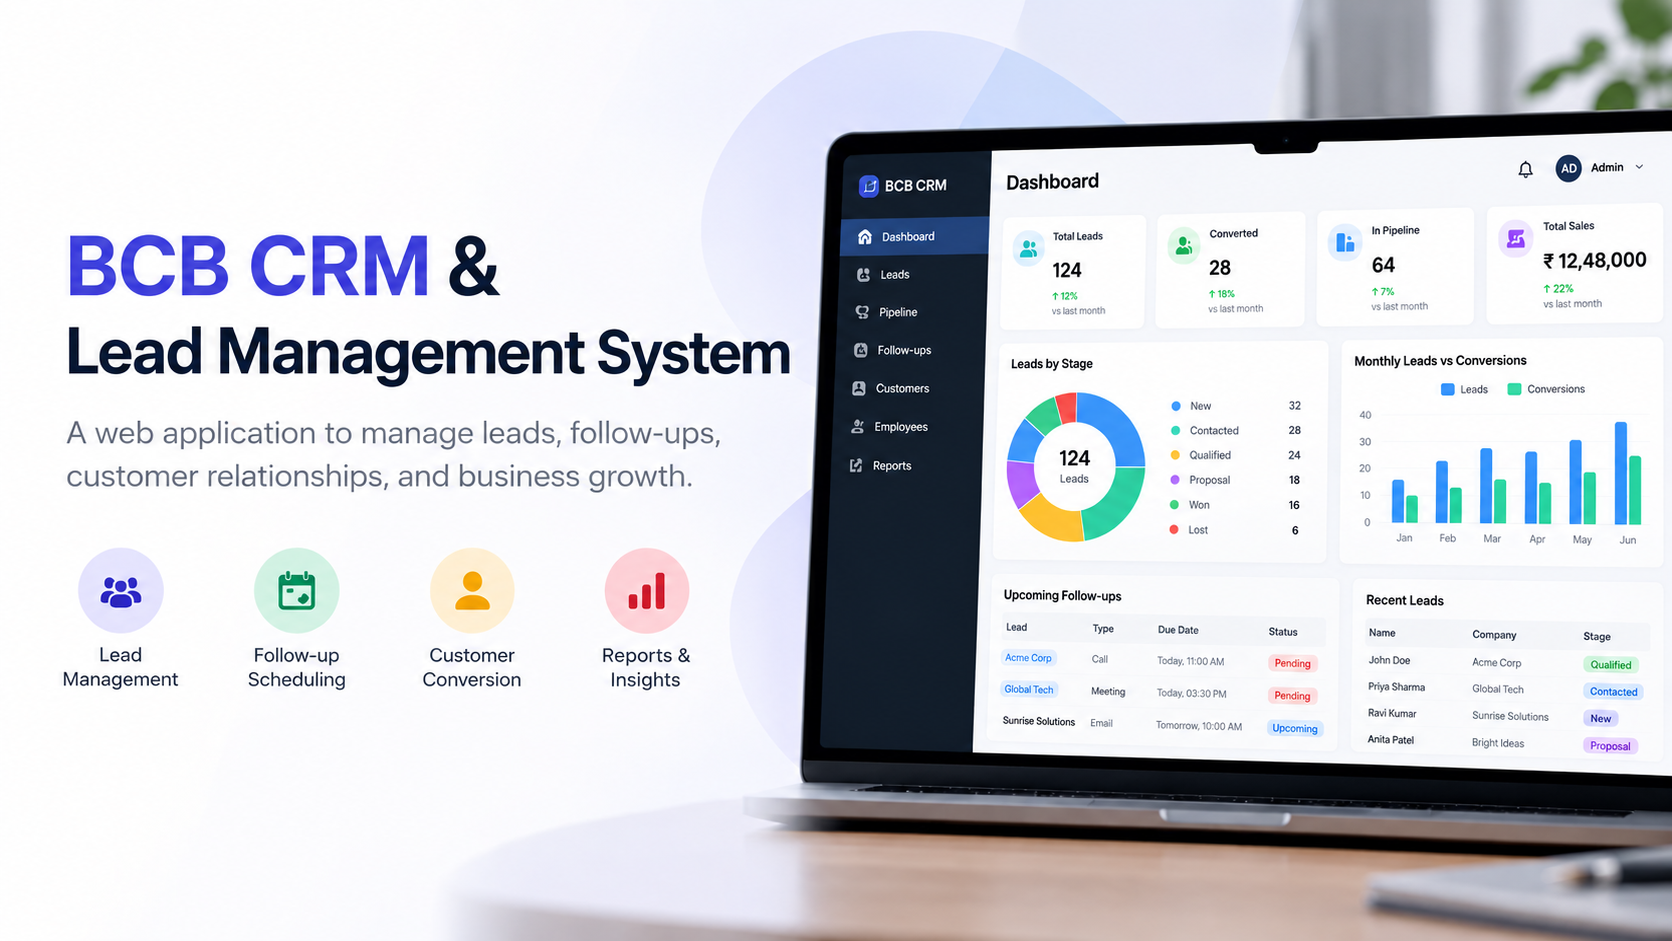
Introduction For my second MCA mini project, I worked on BCB CRM & Lead Management System, a web application designed to help a business organize and manage its interactions with potential customers.
Responses
Markdown supported · ⌘↵ to post
Kamran Khan
Full-Stack Web Developer (React.js + Laravel) | Dashboards, SaaS Apps & Management Systems for Global Clients
I like that you kept the stage history as its own record instead of just overwriting a status column. One thing worth thinking about as this grows: policies protect who can touch the history, but nothing stops an admin (or a stray seeder) from editing or deleting rows and quietly corrupting the pipeline reports. I've started making history tables append-only at the DB level, a check or trigger that rejects updates and deletes, so the audit trail survives even admin mistakes. Cheap to add now, painful to retrofit once the reports are trusted.