Coppersmith's Attack: When Knowing a Little Is Enough to Break RSA
The Problem RSA relies on a simple asymmetry: multiplying two large primes is easy, but factoring their product is hard. Given $$N = pq$$ recovering secret primes \(p\) and \(q\) from public modulus \
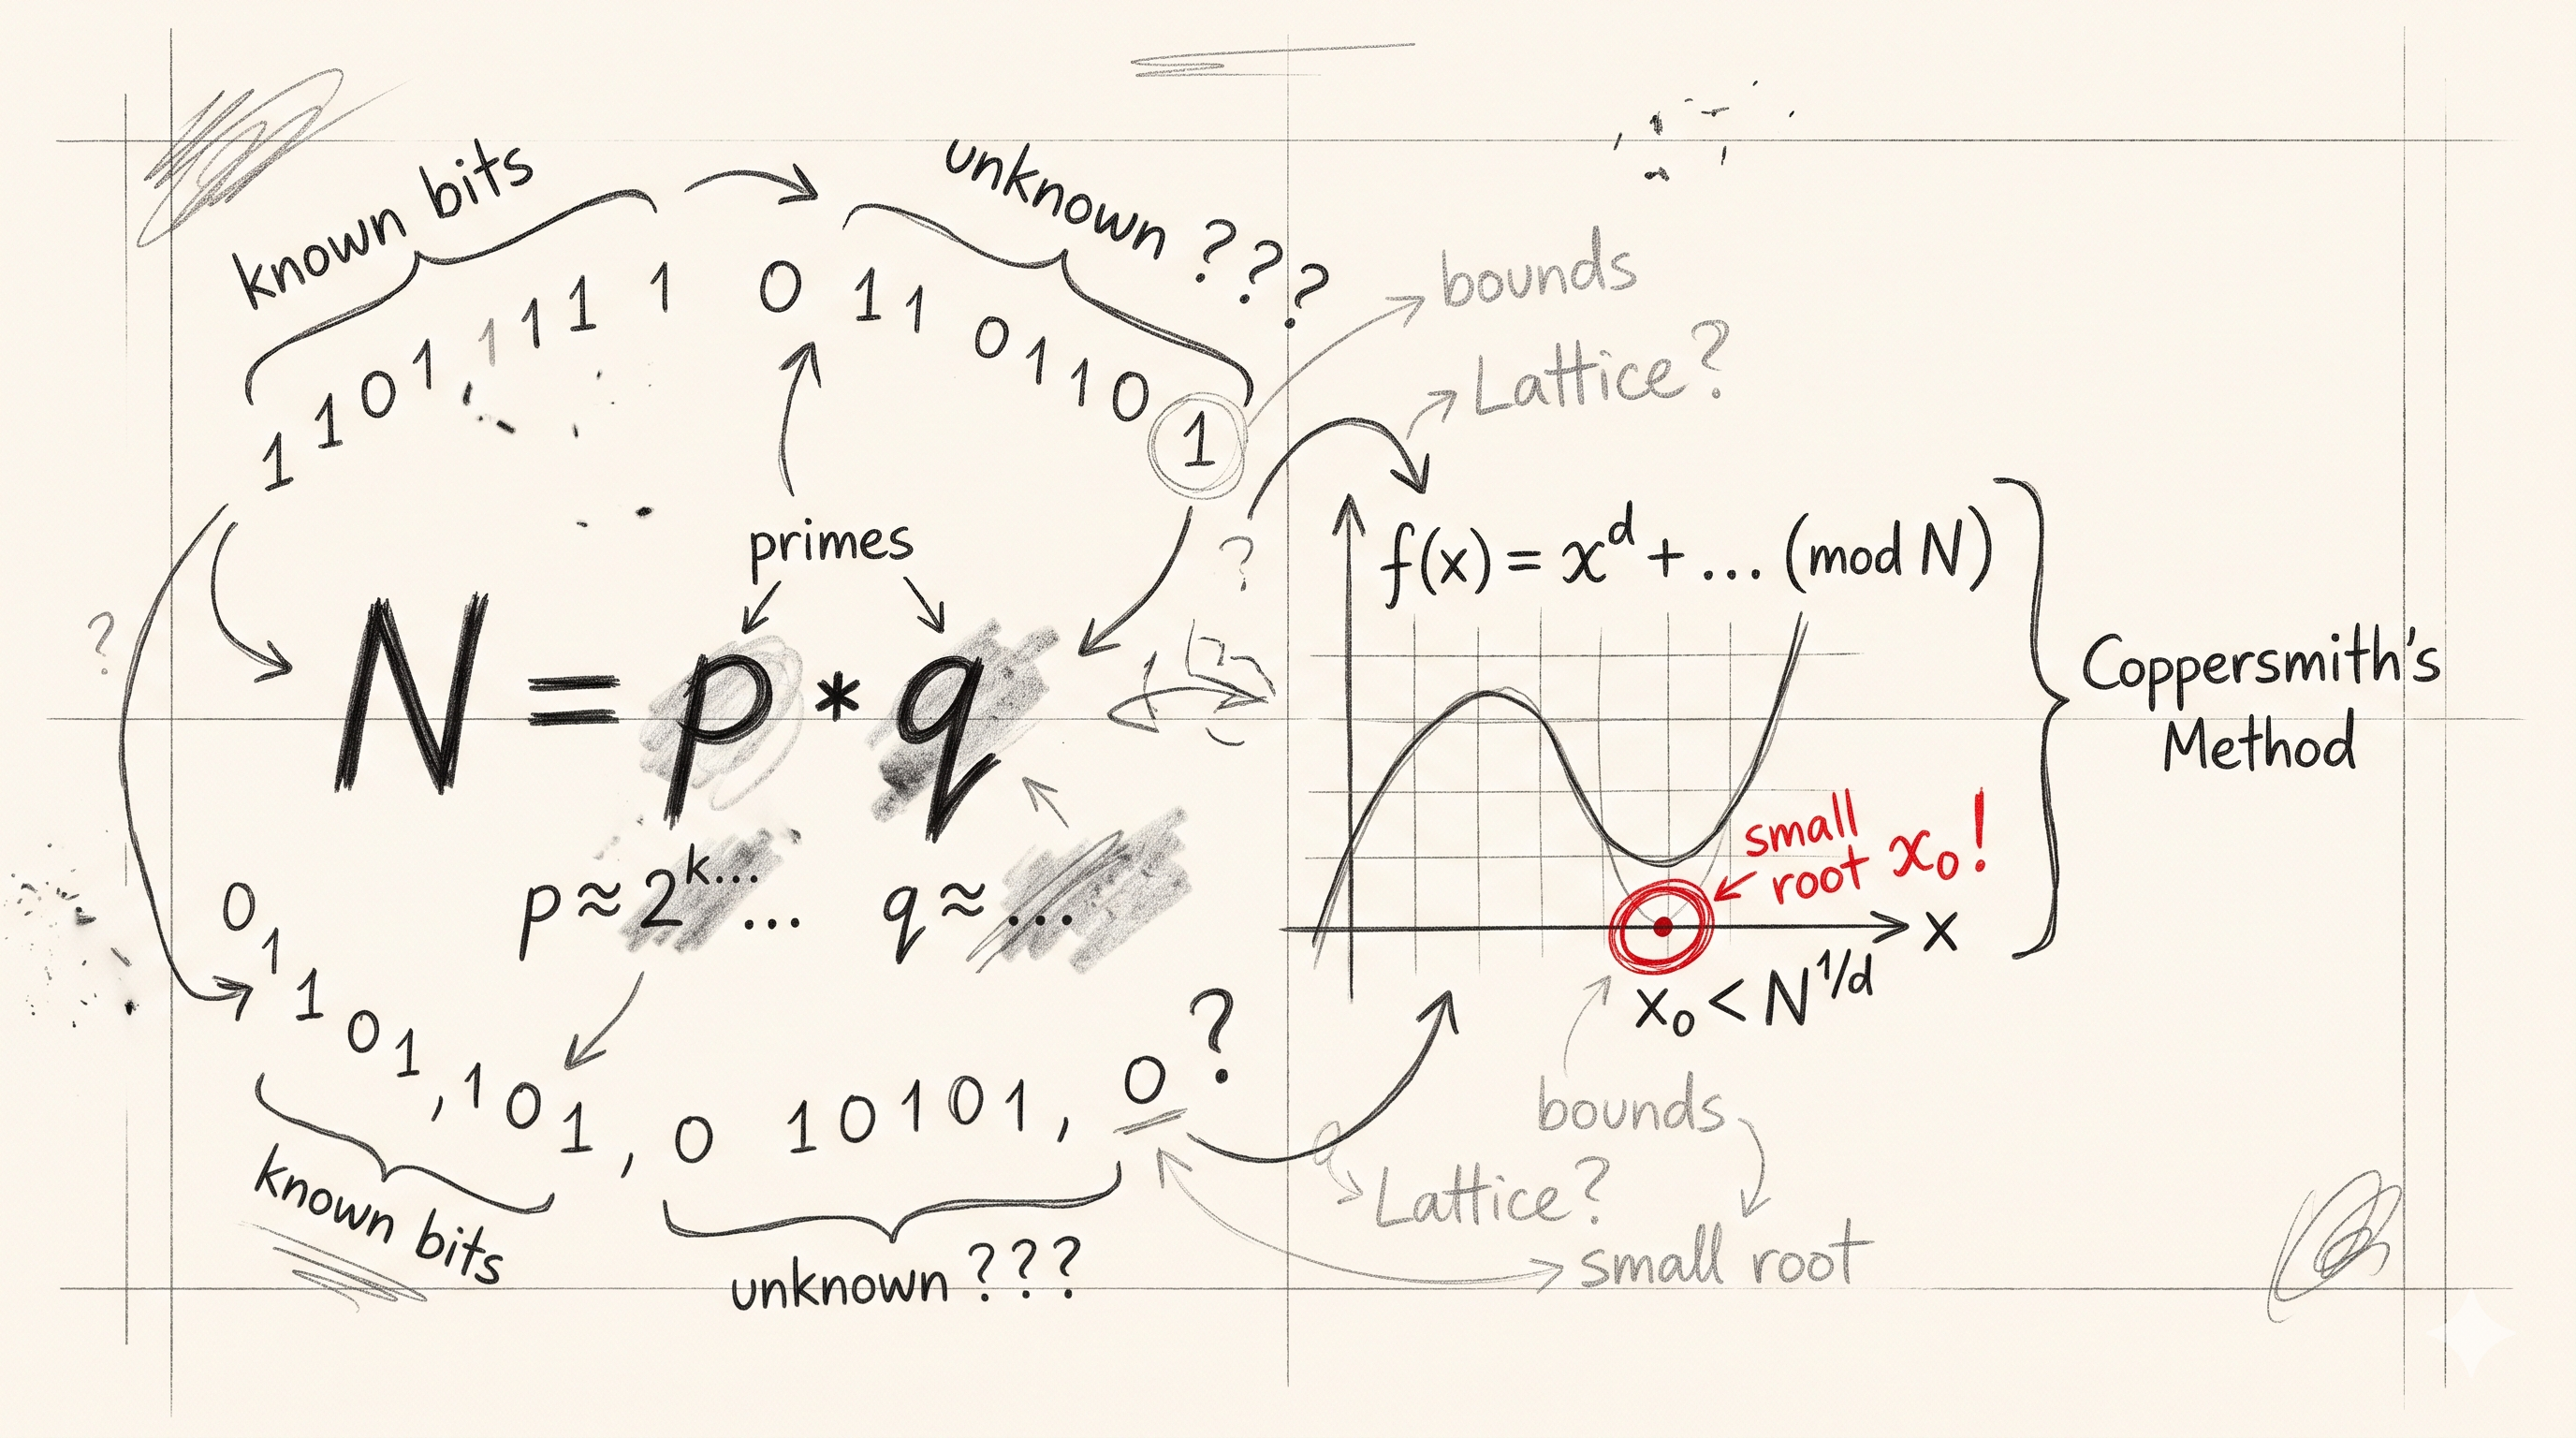
Responses
Markdown supported · ⌘↵ to post
No responses yet.