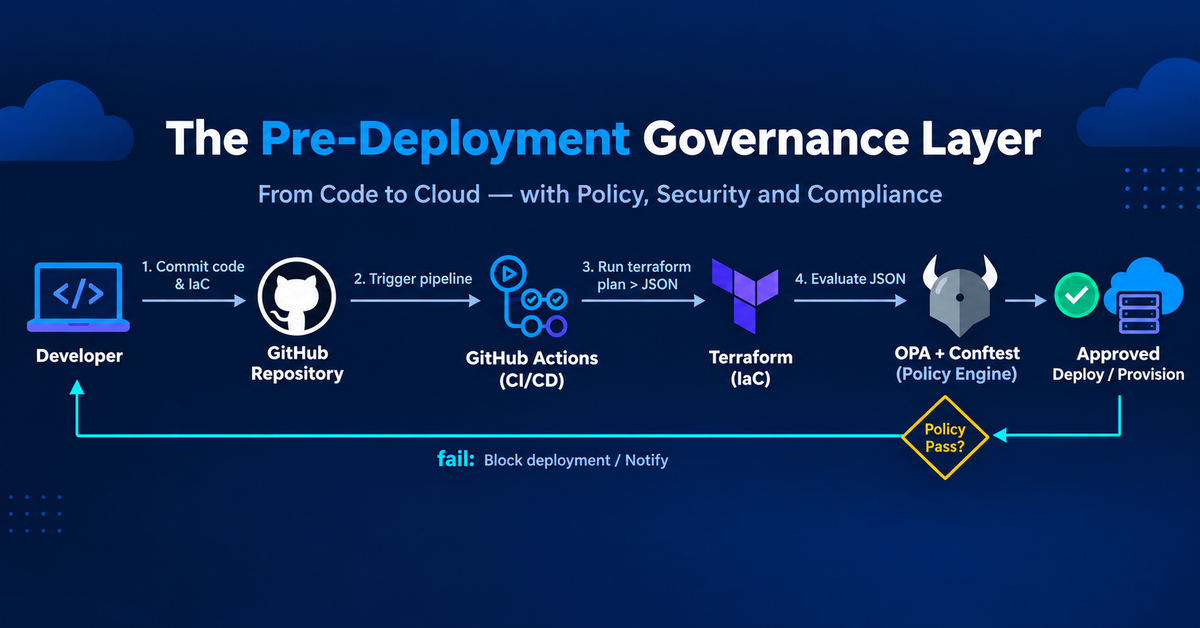
How to Block Over-Privileged IAM Roles in AWS Using Policy-as-Code
Chances are, your AWS account has an over-privileged IAM role right now, and you may not know which one. When you build infrastructure, you write Terraform that declares your resources and assigns IAM
Written by
Code that works isn't the same as code that's safe. I build the difference into the pipeline.
I build tools that catch AWS misconfigurations before they reach production: policy-as-code checks with Terraform, Open Policy Agent, and GitHub Actions, and ZeroLeak, an offline AWS auditor. I'm AWS Certified Solutions Architect – Associate and Cloud Practitioner, with a degree in cybersecurity. I write about the gap between code that works and code that's safe, including where my own tools fall short. Right now I'm building a series on Zero Trust governance for AWS serverless apps. The code is on GitHub. Based in Nigeria and open to Cloud Security and DevSecOps roles. Say hi on LinkedIn.
Responses
Markdown supported · ⌘↵ to post
No responses yet.