Feed
Discussion
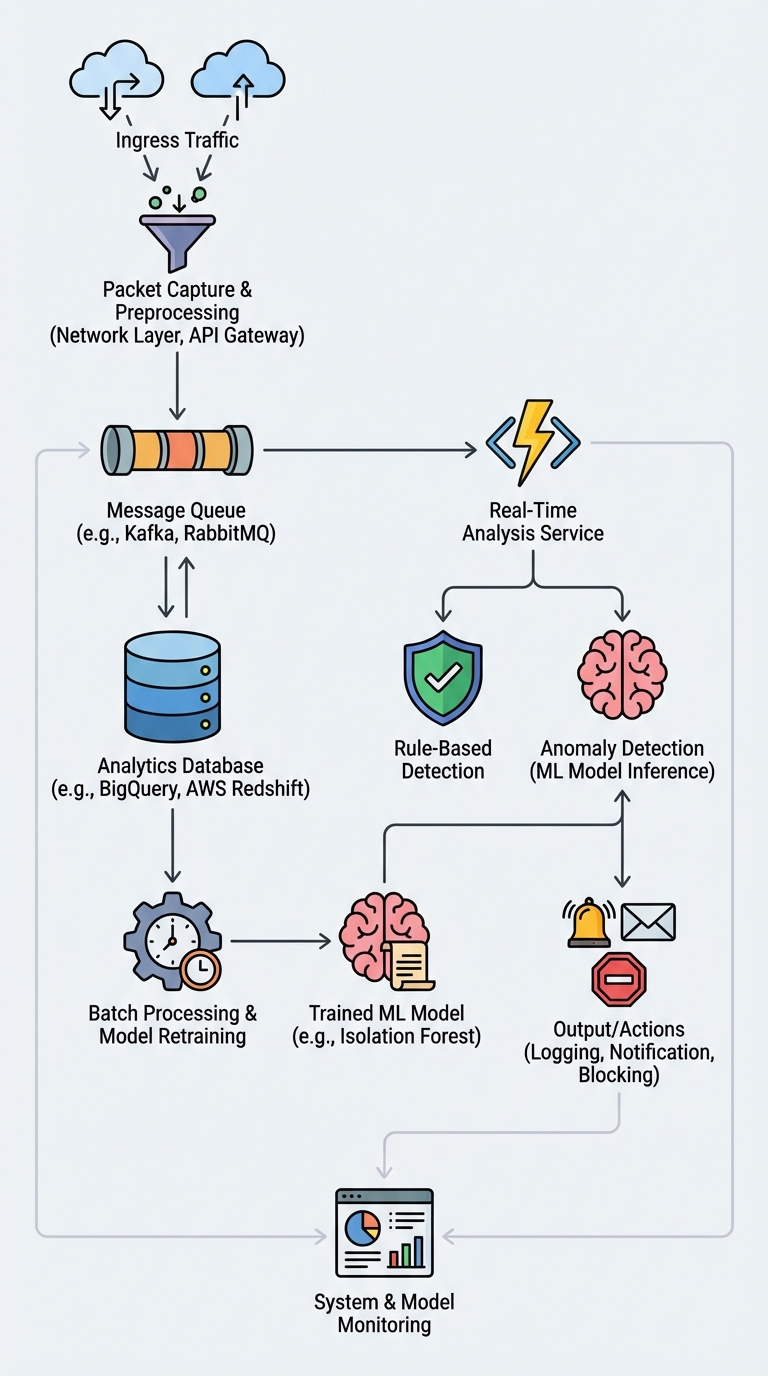
Hybrid Detection Wins Interviews: Rules for Speed, ML for the Unknown
In threat-detection design interviews, the simplest answer that scores high is: use a hybrid approach — fast rule-based gates for known bad behavior, and anomaly-based machine learning to catch the novel stuff rules miss. Below is a compact, intervie...
Responses
Markdown supported · ⌘↵ to post
No responses yet.