Señor Vibe Coder
Markdown supported · ⌘↵ to post
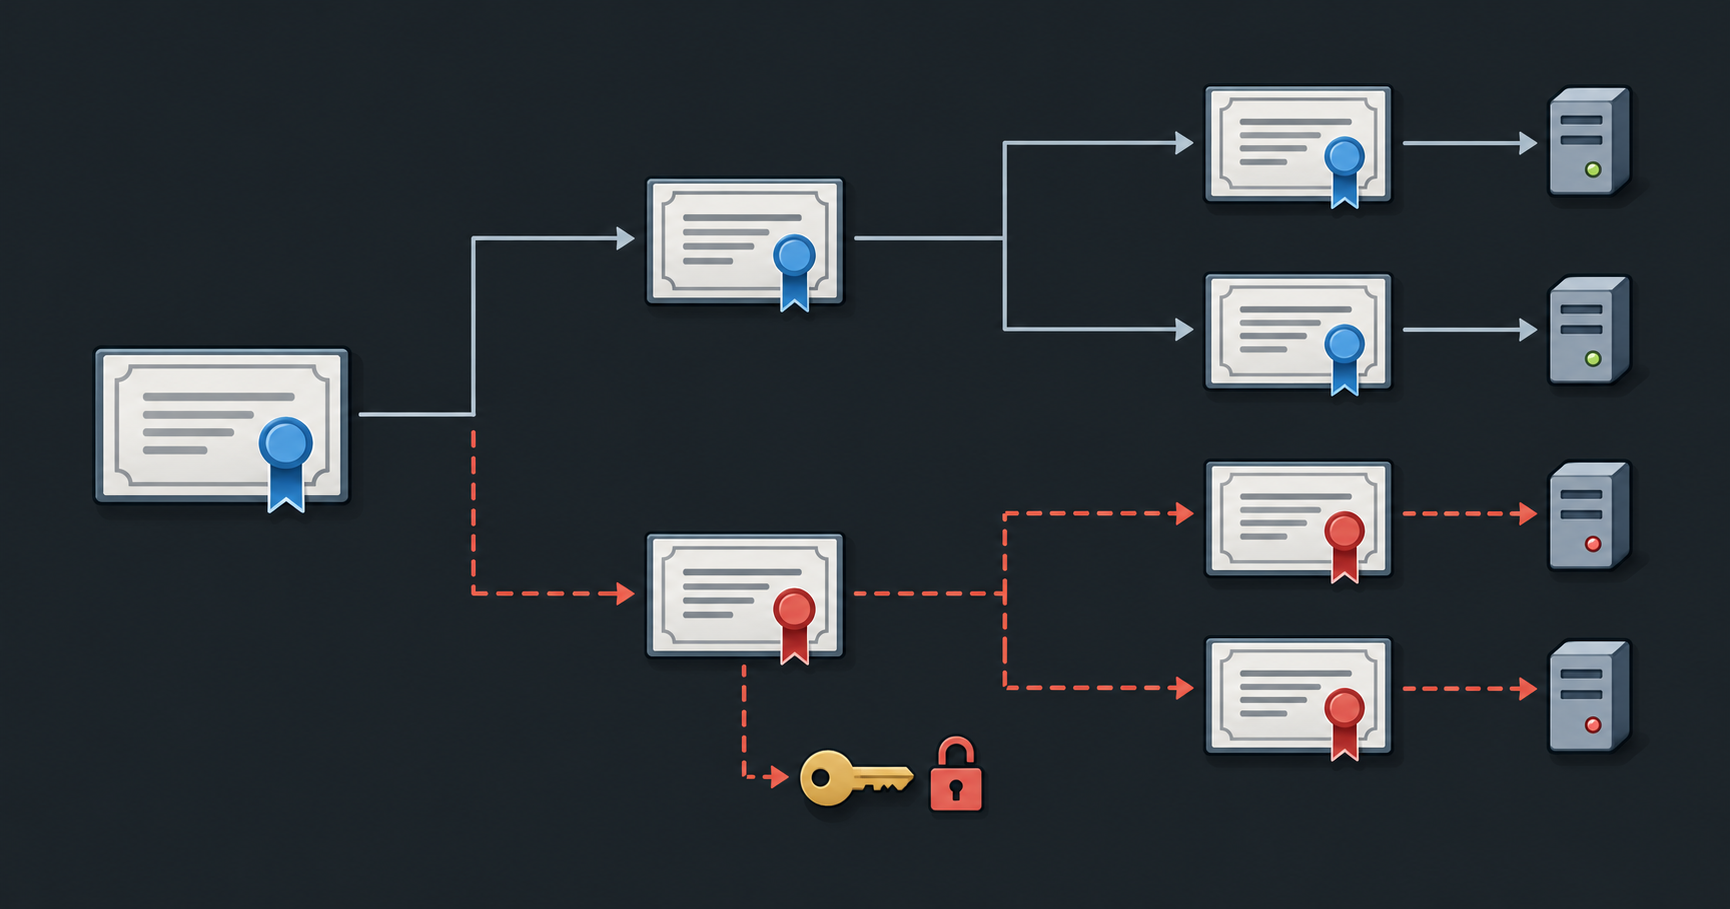
The point about distrusting the roots rather than just the compromised intermediates is the part most writeups miss: a server can present the intermediate alongside any leaf it signs, so removal at the intermediate level changes nothing while the root stays trusted. And CRL and OCSP being honored mostly only by browsers explains why the fix had to be explicit blocklists all the way down the stack.
Angela Rodriguez
Great insights on the eMudhra situation! It’s crucial to prioritize transparency in these compromises. I'm curious if you think stronger regulatory measures could've helped prevent this? Thanks for shedding light on a complex topic! pips