uptimepage
Software engineer with 20+ years building and running production systems: microservice architecture on Kubernetes, cloud infrastructure on AWS and Terraform, and security-critical SaaS in the fintech domain.
Markdown supported · ⌘↵ to post
CDN Edge Ops
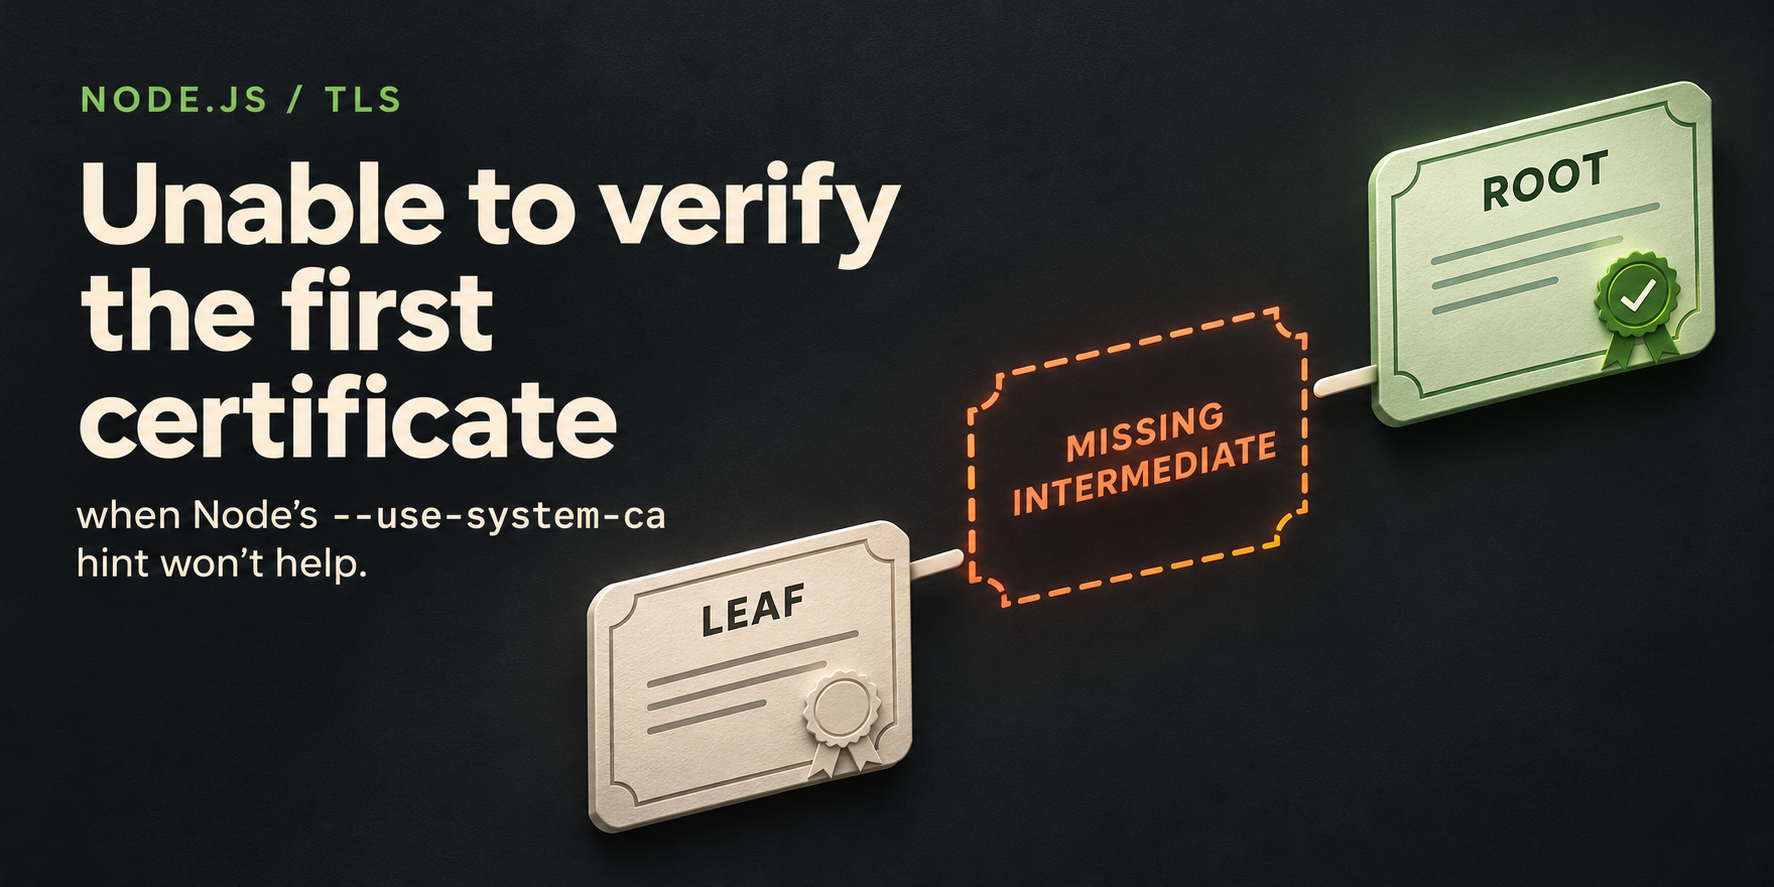
This error is almost always a chain problem, not a Node flag problem. The leaf is fine but the client never sees a trusted intermediate — common behind a reverse proxy that presents leaf-only, or a corporate MITM CA that never landed in the trust store the process actually uses.
Checks that save time: openssl s_client -showcerts to the same host:port the app dials, compare the chain length to what browsers get, and confirm the runtime trust store (distro ca-certificates vs a container's empty /etc/ssl). --use-system-ca only helps when the missing CA is already on the host; if the proxy should be stitching the chain, fix the server cert bundle first instead of disabling verification in the client.