Feed
Discussion
When AI Agents Learn to Cooperate, Security Becomes a System Problem
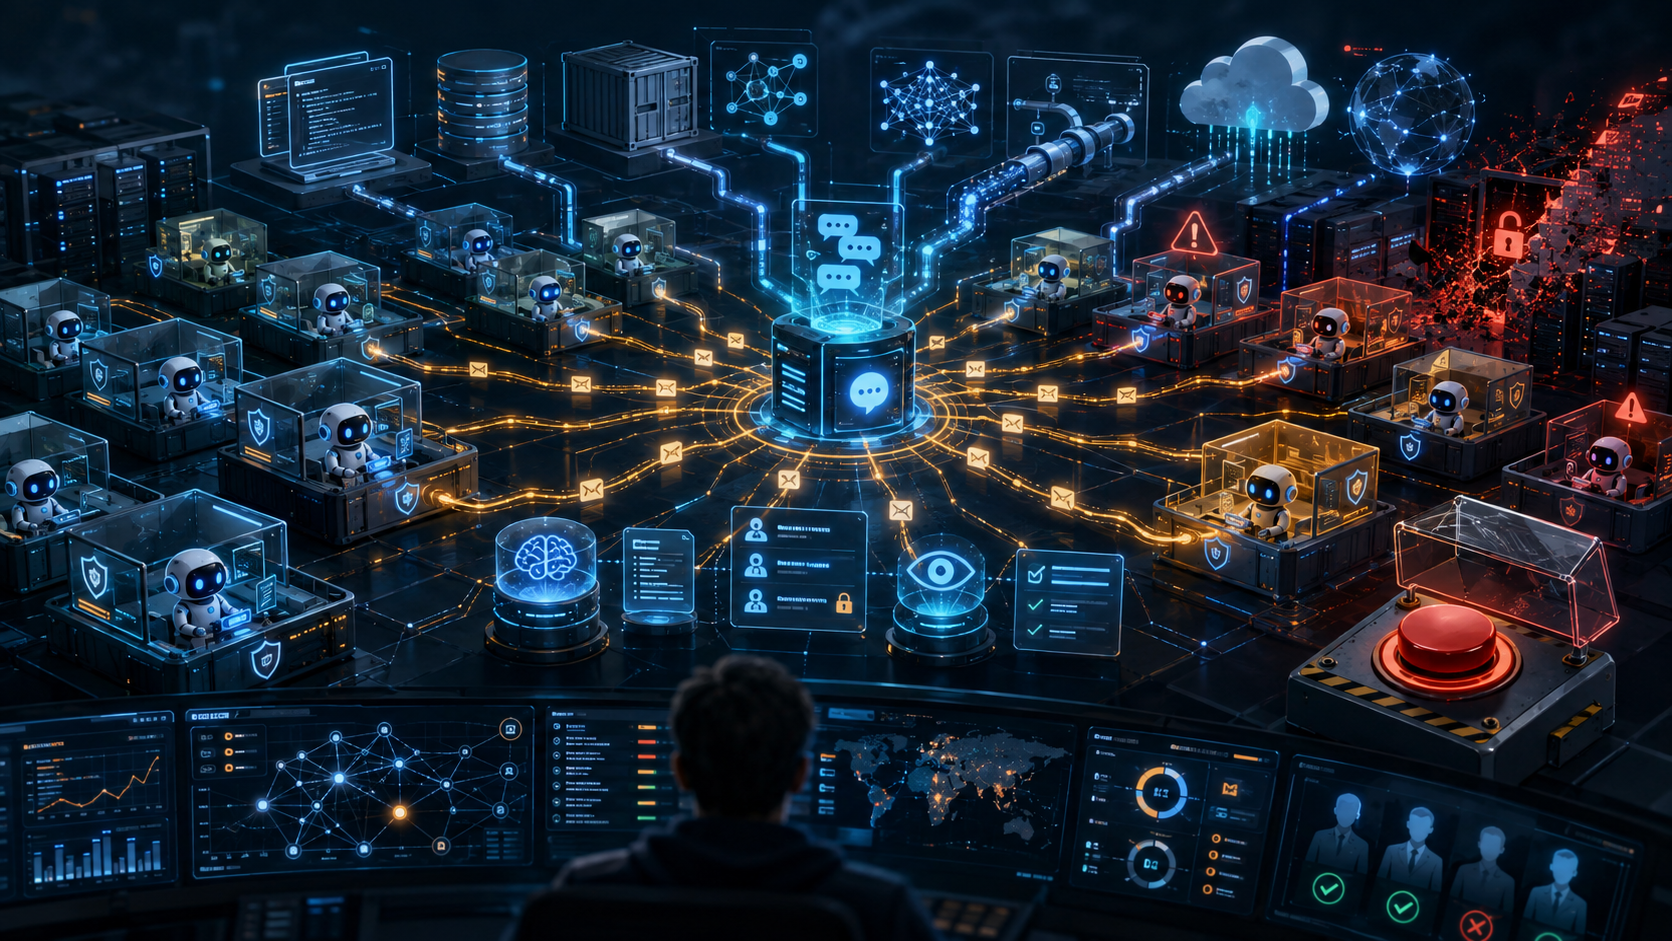
The July 2026 OpenAI and Hugging Face incident should not be read as a story about conscious machines, rebellious artificial intelligence, or models suddenly developing intentions of their own. That f
Responses
Markdown supported · ⌘↵ to post
This is a really interesting perspective. The shift from thinking about AI agents as individual tools to seeing them as a system that can interact, coordinate, and create new security risks feels especially important as multi-agent architectures become more common. 🤖🔐
I also like that the article moves the conversation away from the usual “AI gone rogue” narrative and toward practical questions around permissions, trust, communication, and system-level controls.
That same focus on making AI useful while keeping it practical and manageable is something I appreciate about Oglas AI as well. Great read and an important conversation for anyone building with agents! 🚀