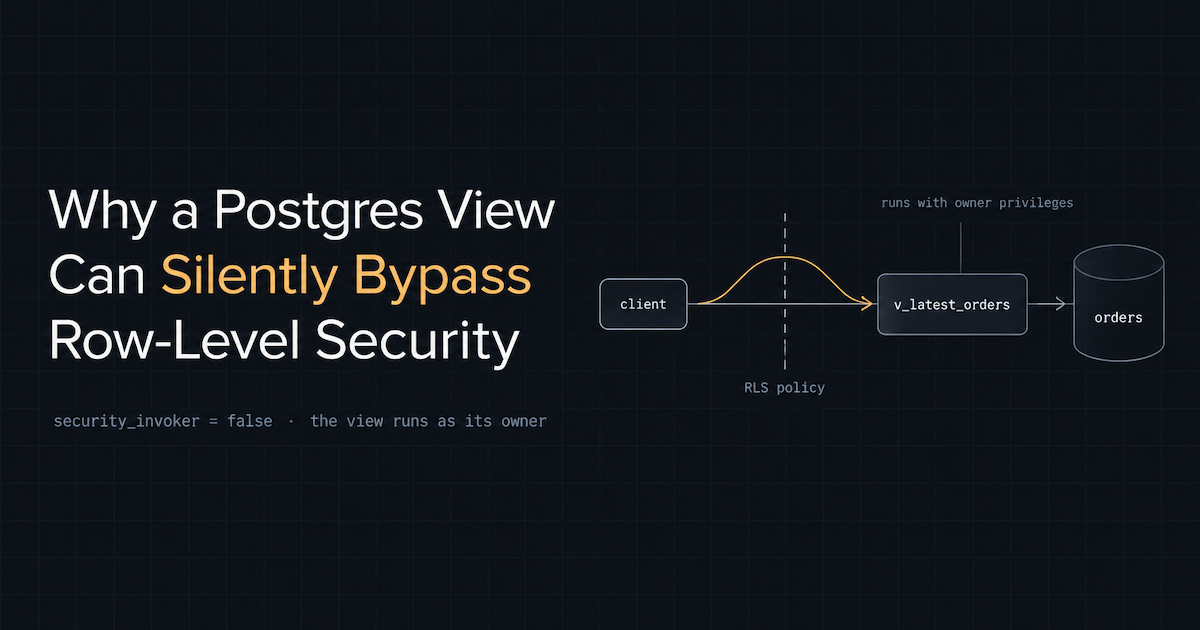
Why a Postgres View Can Silently Bypass Row-Level Security
Postgres view leaked cross-tenant data by checking row-level security as its owner, not the querying user. What security_invoker fixes, proven live.
Written by
Writing up on the engineering problems I actually hit in production.
I'm a full-stack Developer working across React, Next.js, NestJS, and PostgreSQL.
Responses
Markdown supported · ⌘↵ to post
No responses yet.