Indie Android studio building privacy-focused and useful apps.
TSI Dev Studio builds privacy-focused and useful Android apps, with a focus on local-first design, simplicity, and user control.
Markdown supported · ⌘↵ to post
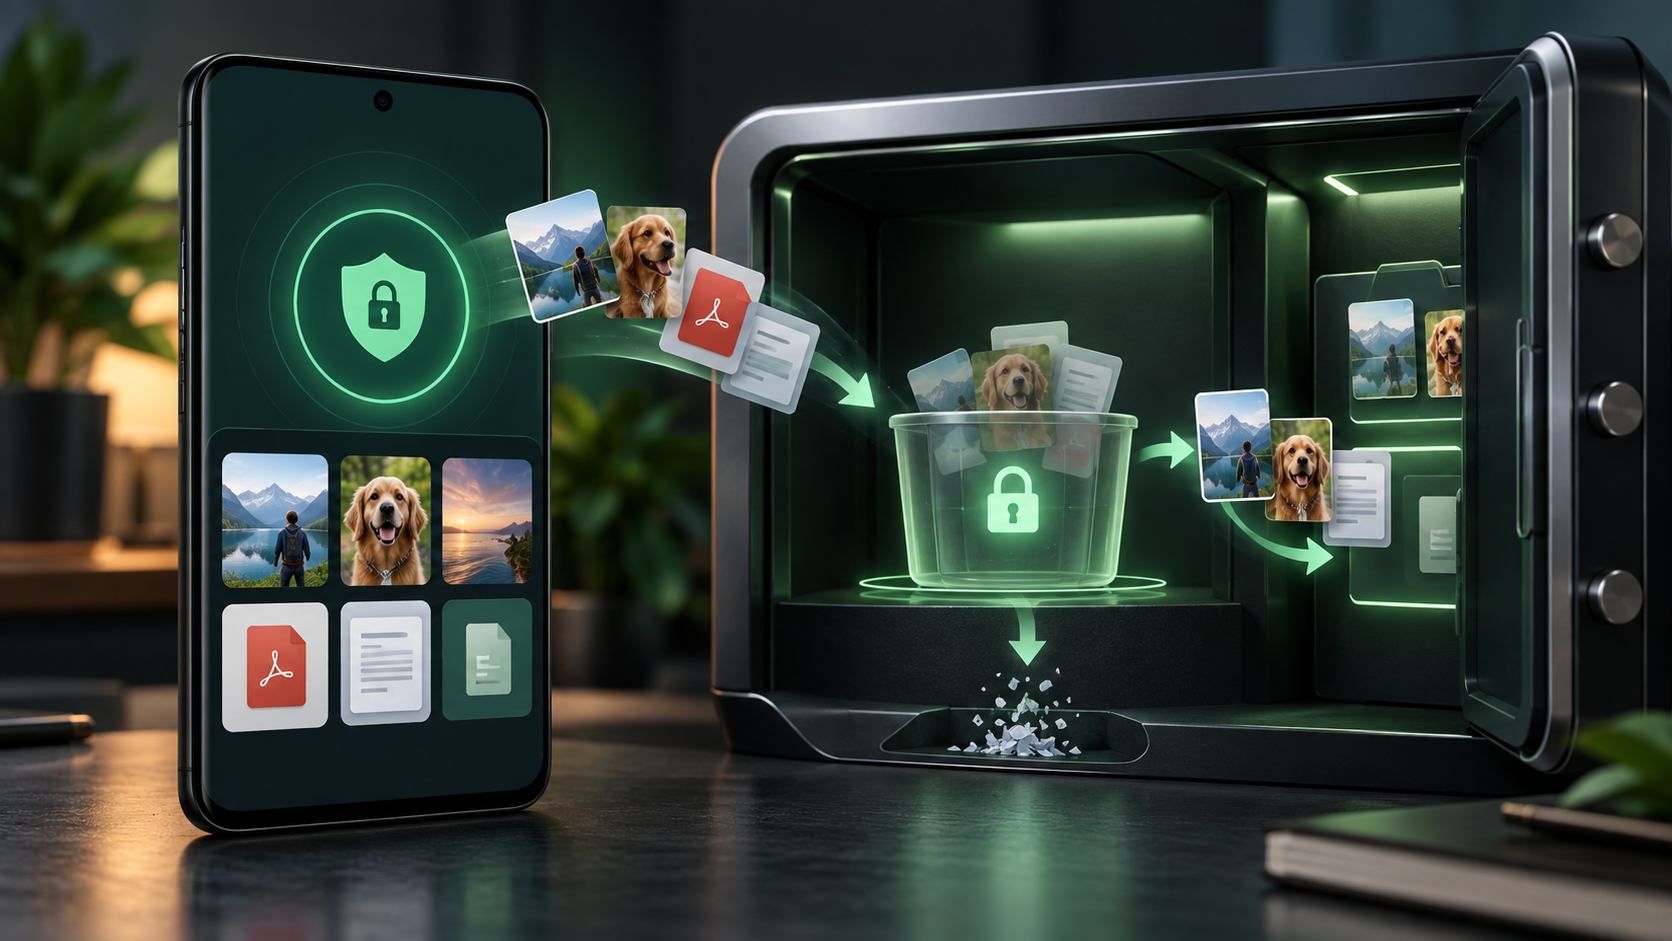
That’s a fair concern. The Trash in Xsilent is intentionally kept inside the same protected encryption boundary as the private vault rather than being treated as a plain recovery folder or cloud-backed holding area. I deliberately avoid publishing the exact key-management layout or where individual key material is anchored, because those implementation details are part of the app’s security design rather than something users need to rely on. The important property from the user’s perspective is that items in Trash remain encrypted throughout the recovery window and are not intentionally exposed as plaintext outside the vault. So yes, key handling is treated as part of the threat model — but I prefer to describe the security guarantees publicly rather than disclose the internal key topology
indiainfranotes
An encrypted trash is a nice touch because the recovery window is exactly where most privacy apps leak, deleted files often sit in plain storage or cloud backups for days. The tricky part is key handling: if the trash key lives next to the files, encryption mostly protects against casual browsing, not a device dump. Where does the key for the trash live, Android Keystore or something derived from the user unlock?
iin1006h03