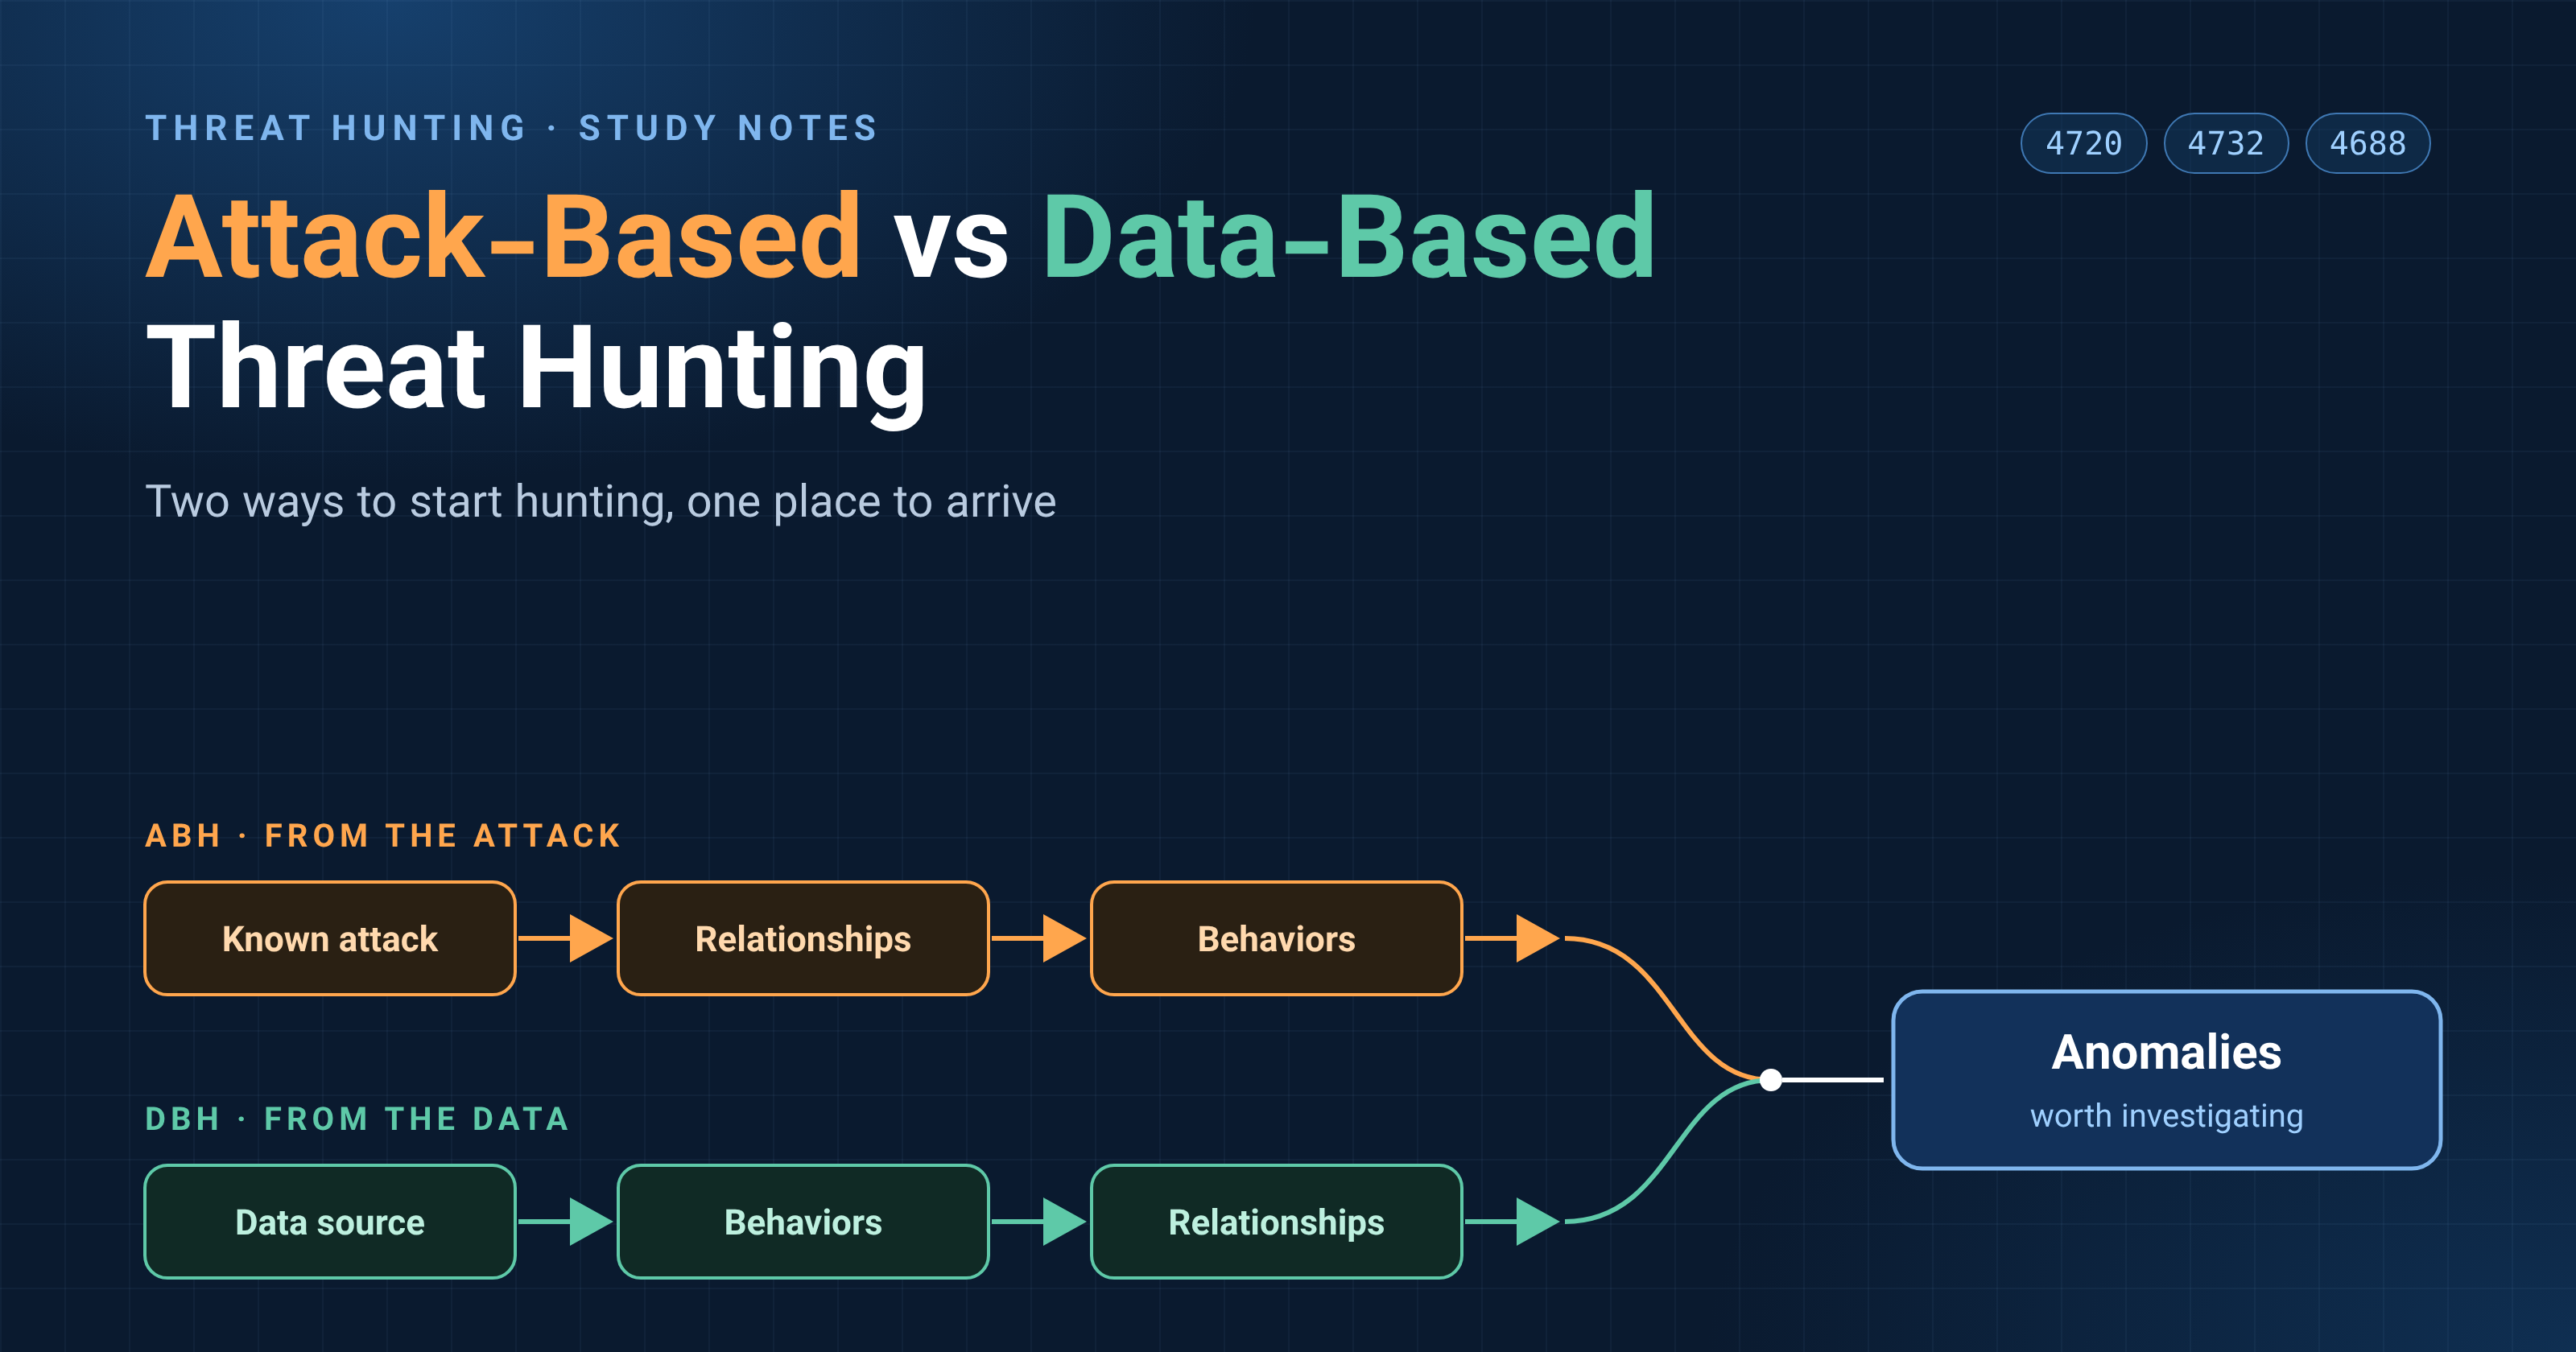
Attack-Based vs Data-Based Threat Hunting: Two Ways to Start
Study notes on two threat hunting approaches: starting from an attack (ABH) or from a data source (DBH), with Windows Event ID examples.
Written by
Computer Engineering student sharing my journey through Linux, Networking, and Systems Administration.
Responses
Markdown supported · ⌘↵ to post
No responses yet.