Your API's biggest hole isn't injection - it's the ID in the URL
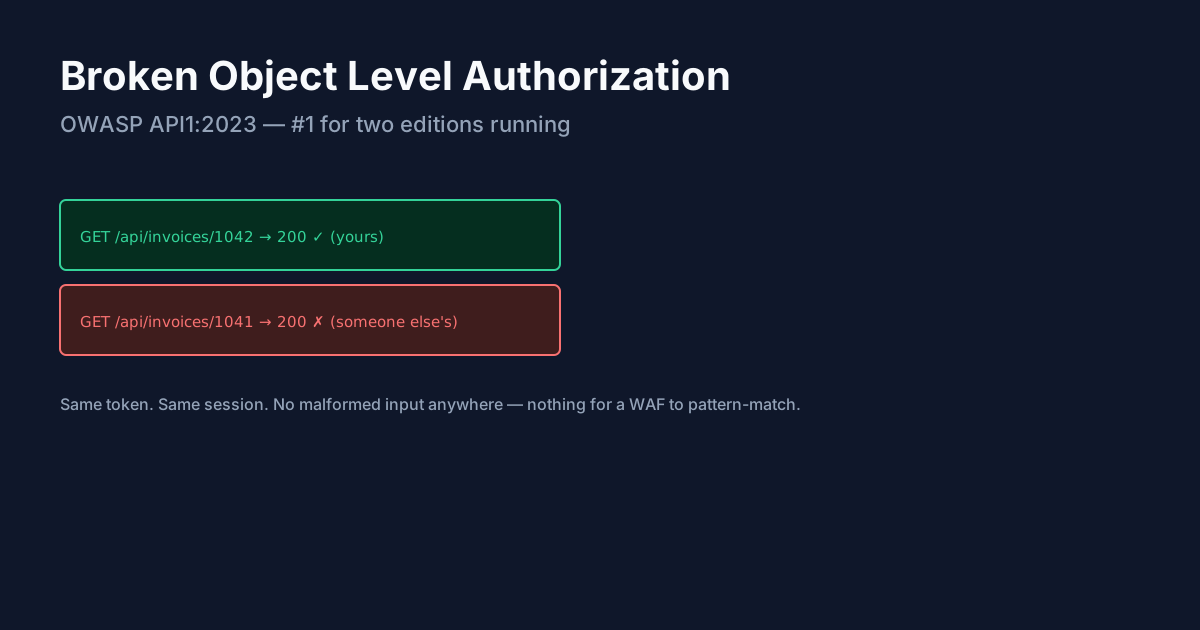
GET /api/invoices/1042 returns your invoice. You're logged in, the token is valid, the response is a clean 200. Change one character - GET /api/invoices/1041 - and it returns someone else's invoice. S
jaytank.hashnode.dev10 min read