Independent security researcher and systems engineer based in Berlin. Author of UNK_DeadDrop and unk-scanner. I write about static AST analysis, software supply-chain security, and low-level runtime internals. Currently open to full-time roles in security research, static analysis tooling, or systems engineering.
Markdown supported · ⌘↵ to post
Damiano Bianda
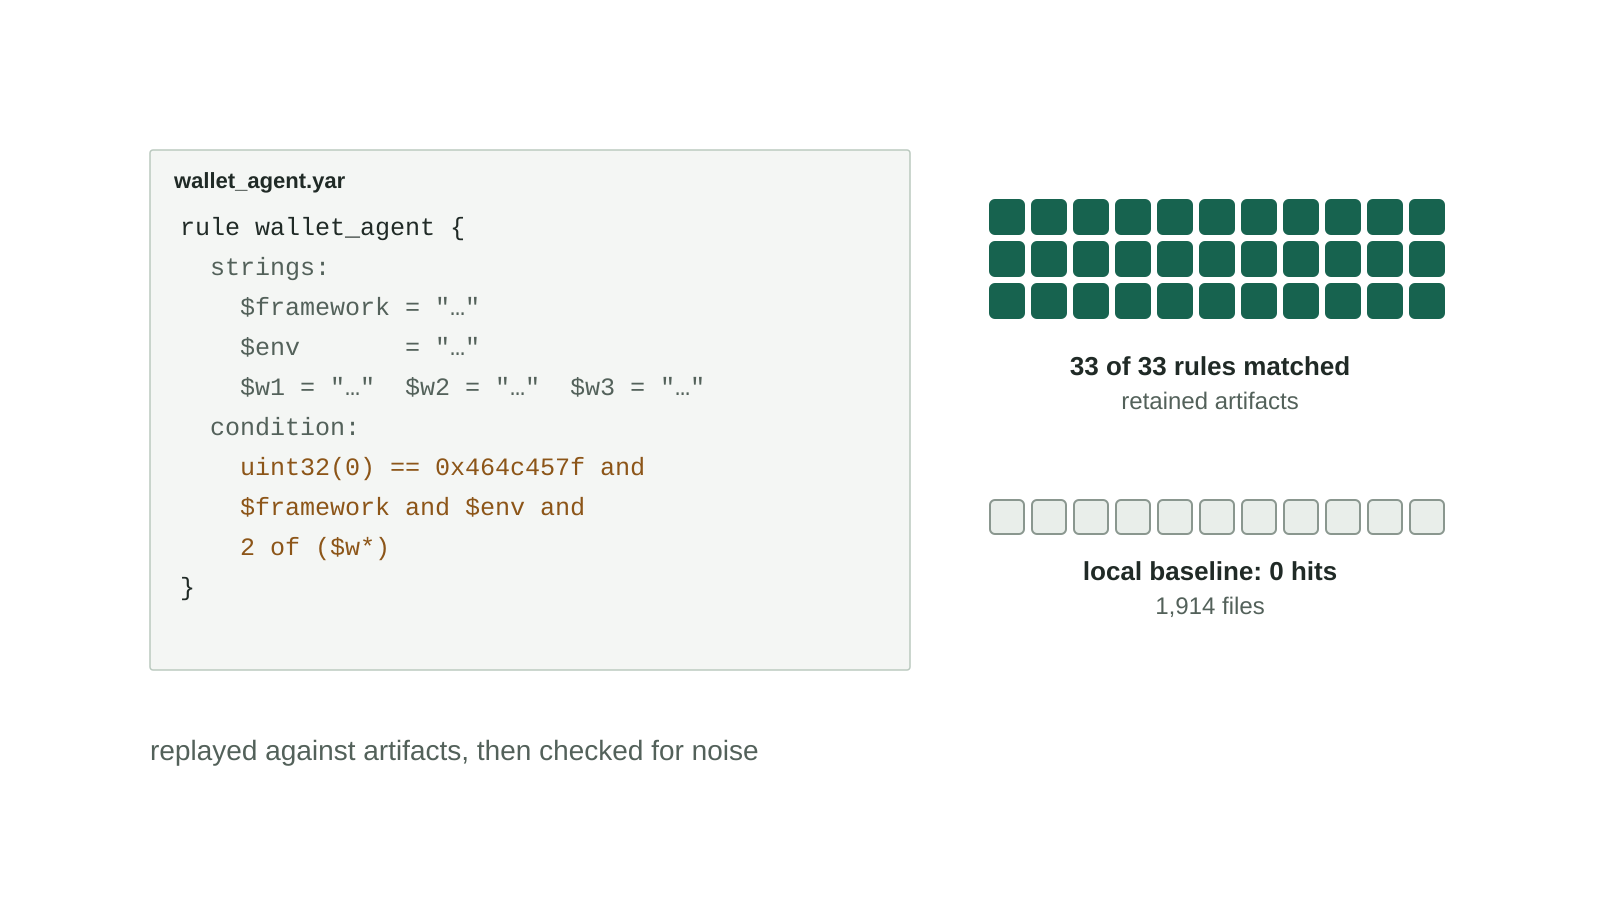
The ELF magic fix deserves a mention of its own: requiring the header at offset zero is the standard way to stop a byte-pattern rule from firing on research prose, and in YARA it stays self-contained as uint32(0) == 0x464C457F in the condition, no separate module needed. What I find most useful here is the decision to drop the event and workspace-configuration rules instead of replaying them against synthetic telemetry. A detection validated on invented records measures the fixture, not the malware, and publishing it would have made the snapshot look broader than the evidence supports.