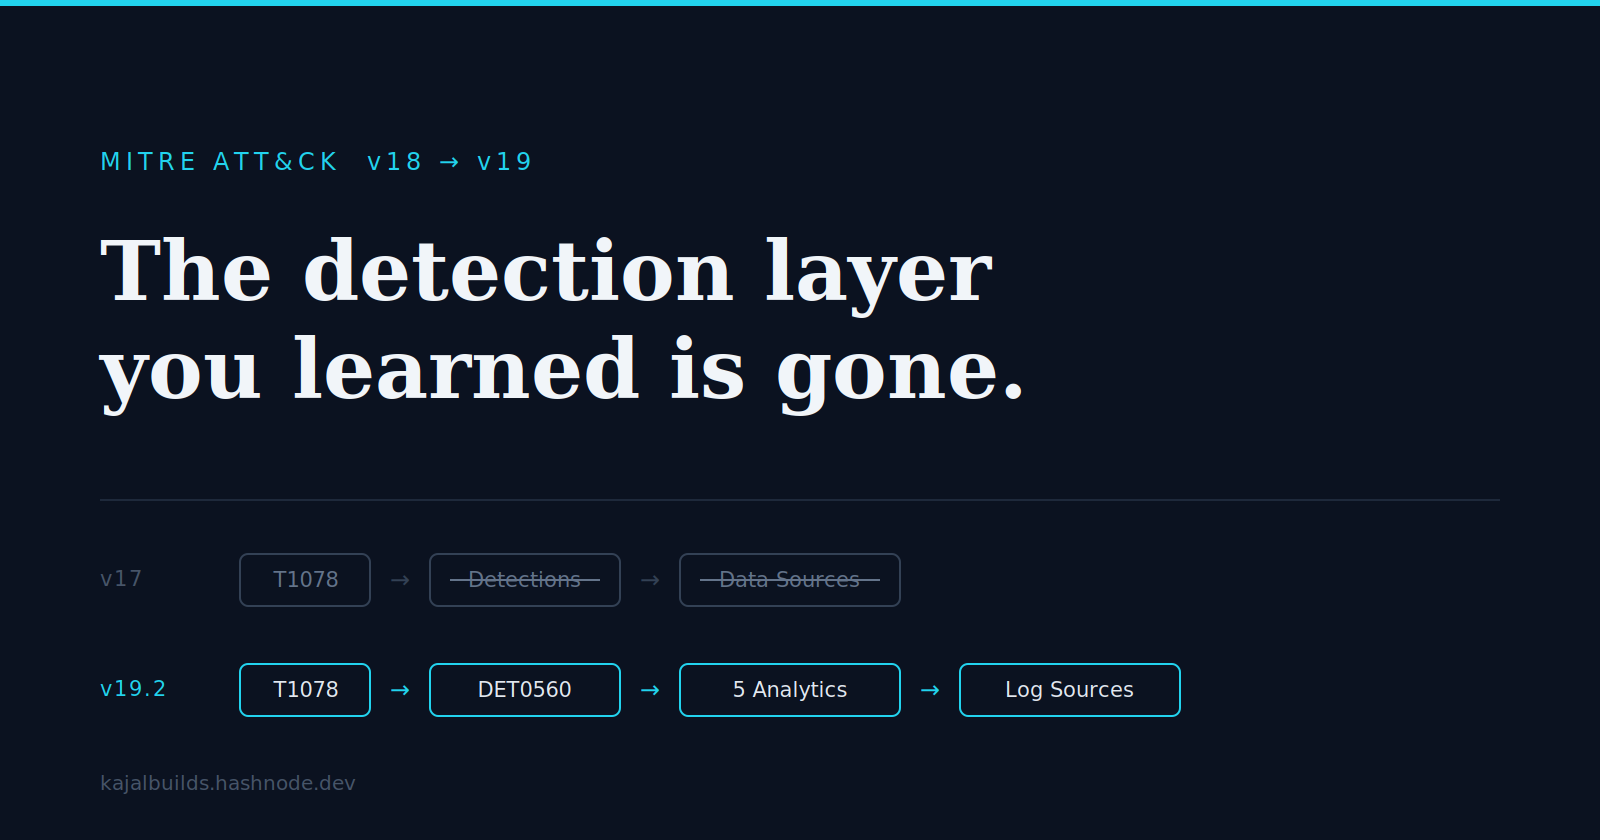
The MITRE ATT&CK most people are learning was retired in October 2025.
MITRE retired the Detections field and Data Sources in v18, and split Defense Evasion in v19. What replaced them, and how to read ATT&CK now.
Written by
I write about detection and identity for security vendors and MSPs. ICT Support Technician@ JB Hifi and a Cybersecurity Master's student, AISA Cyber Security Awards 2026 finalist.
I write about detection and identity. Specifically, the gap between what a security control is assumed to prove and what it actually proves, and what that gap looks like in the logs. Recent posts cover the blind spots built into nine common log sources, the anatomy of an identity compromise through Entra and M365 telemetry, and the MITRE ATT&CK detection layer that was retired in 2025. Two rules hold across everything here. Every factual claim is sourced to primary documentation, meaning vendor technical docs, standards bodies or government advisories, never vendor marketing. Lab work is labelled as lab work. I am a cybersecurity Master's student in Melbourne and a finalist in the AISA Cyber Security Awards 2026, Student of the Year category. I build and publish ATT&CK mapped detections in a public Microsoft Sentinel lab. I take paid writing commissions from security vendors and MSPs.
Responses
Markdown supported · ⌘↵ to post
No responses yet.