Your backup server is the crown jewel: why ransomware crews go after backups first
Between 10 and 19 September 2026, an attacker worked its way through a UK school estate. It did not start with the school's data. It started with the backup servers.
According to Bitdefender's report,
·10 min read·sentinelleai.hashnode.devRead the article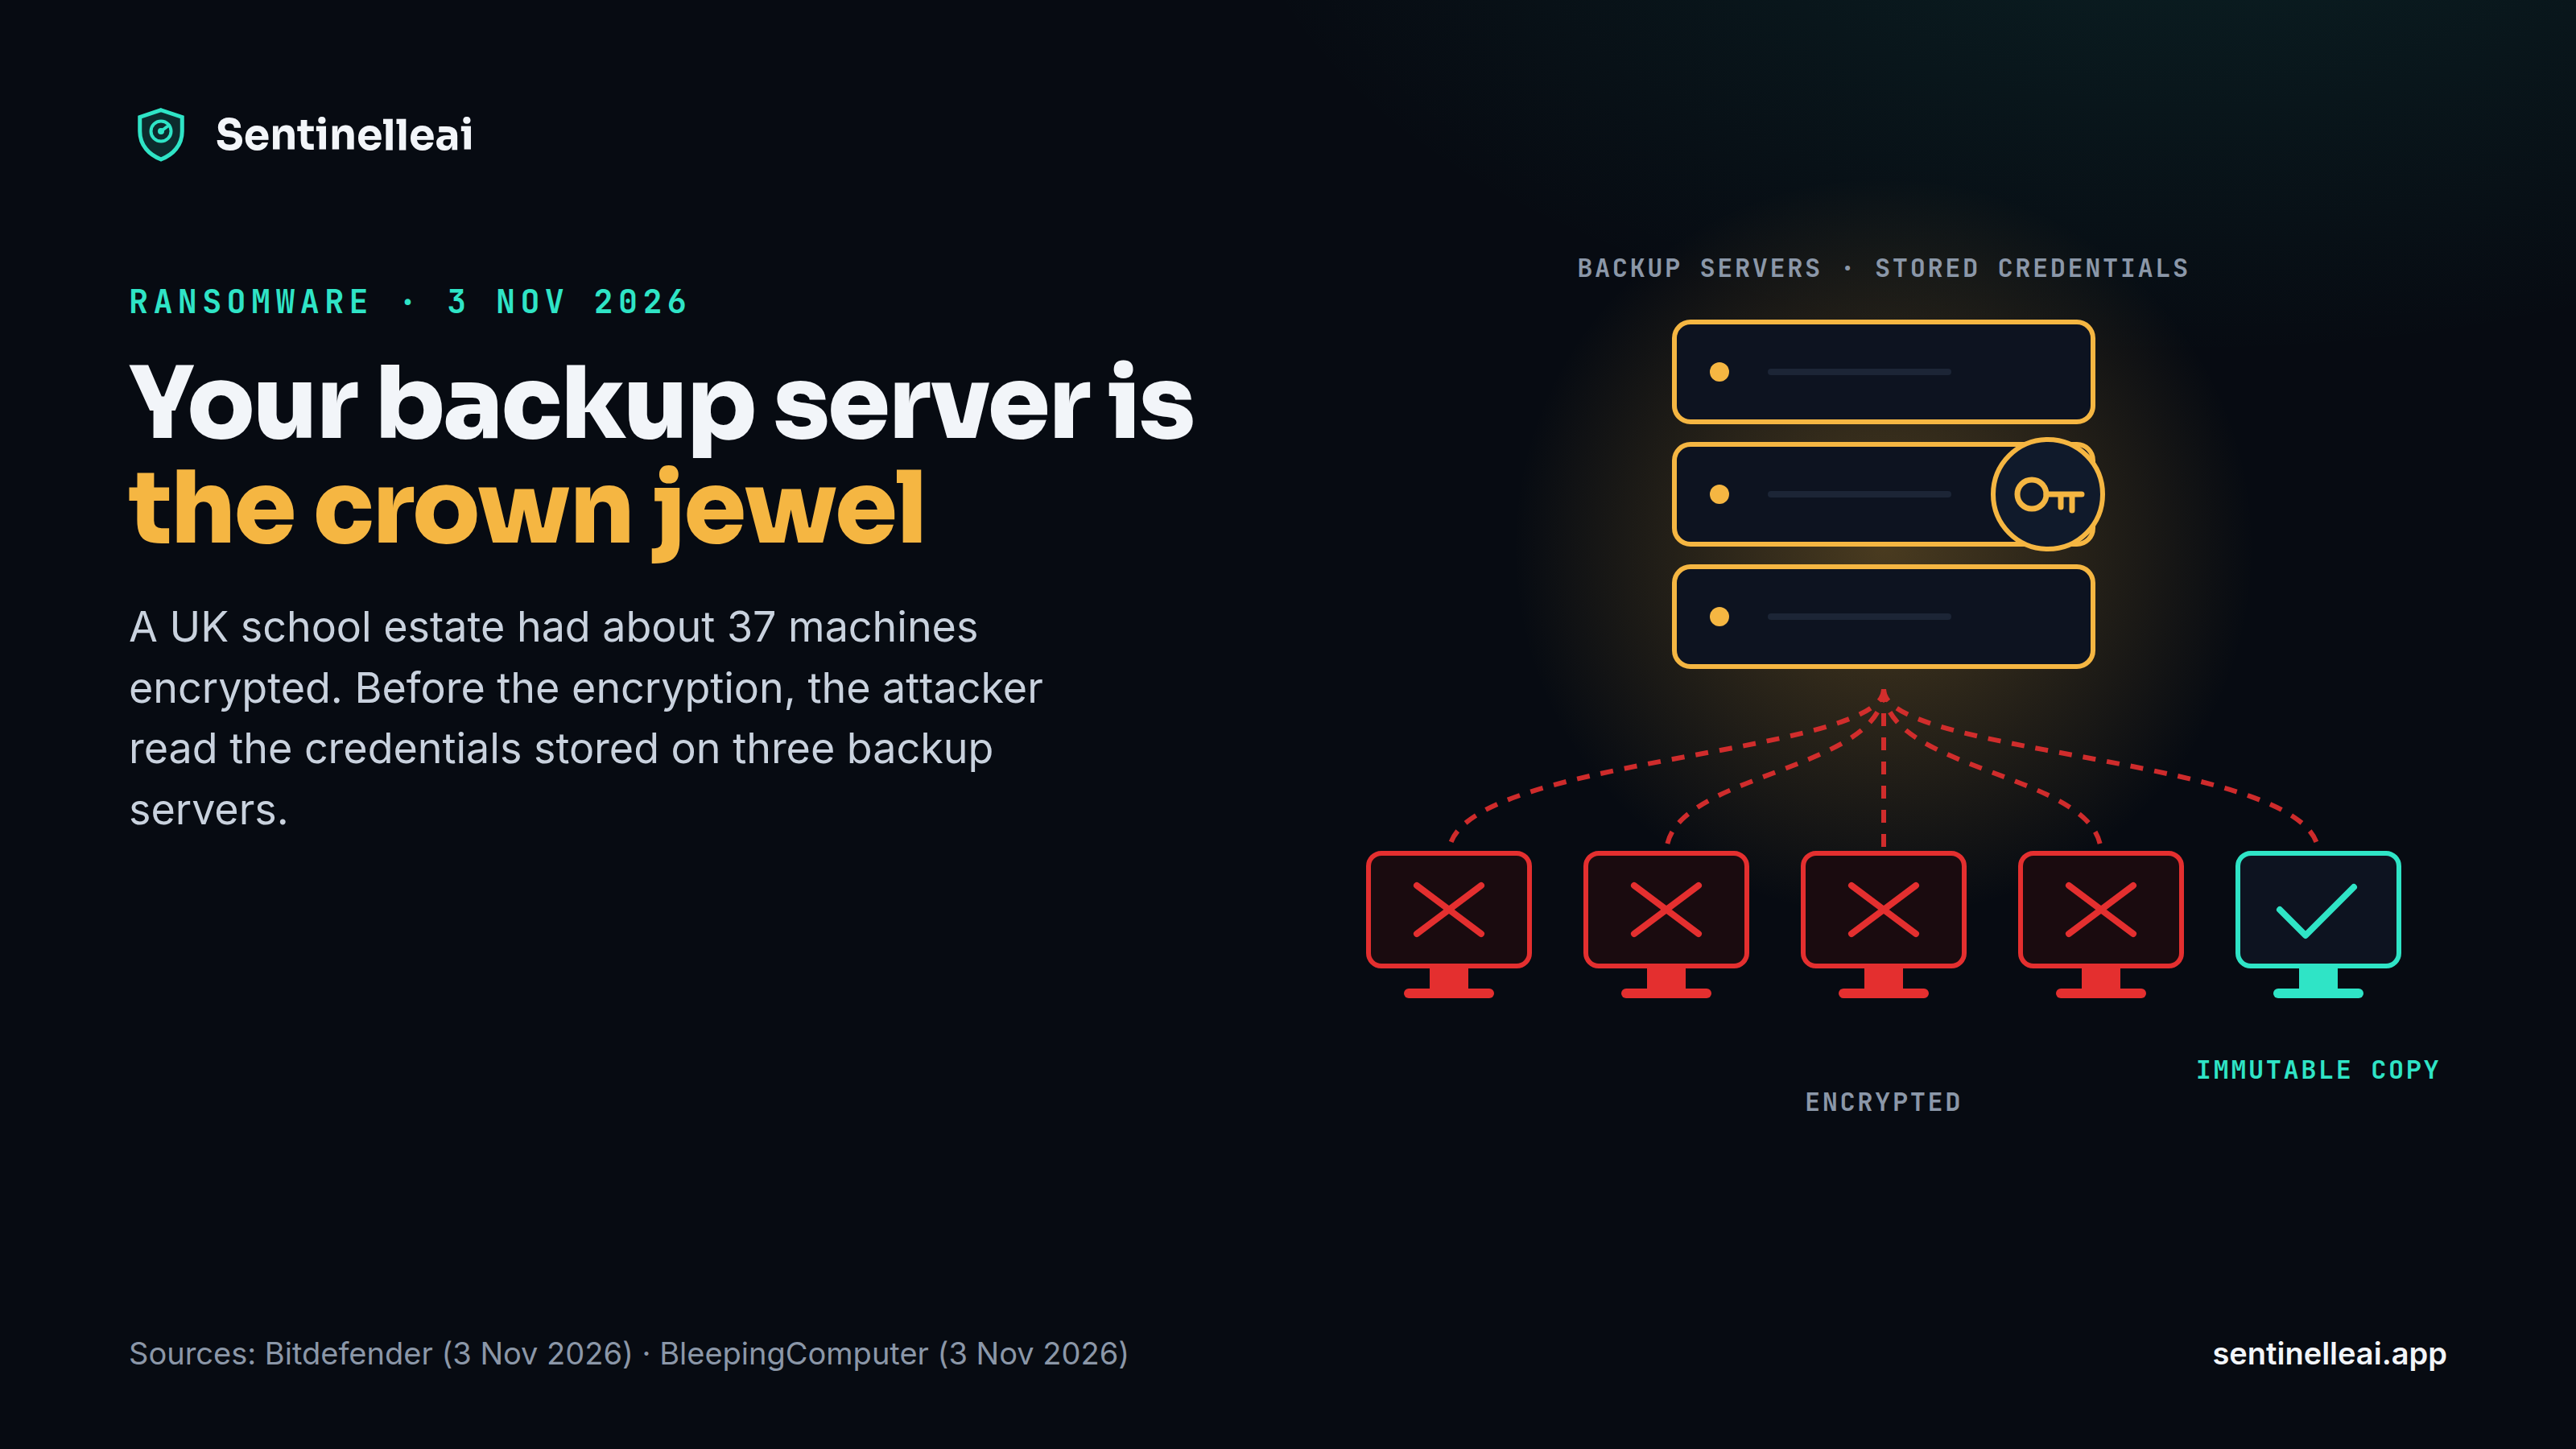
Mario Fang
这篇把顺序讲得很清楚:9月10到11日先从三台 Veeam 备份服务器里读出凭据,9月19日加密前才删系统状态备份,备份是先被拿下的,不是最后才遭殃的。这一点我自己深有体会:以前我把备份服务器也放在生产域里,用的还是域管理员账号,总觉得备份只是个工具,没把它当成高价值目标。后来有一次做恢复演练才发现,域里任何一个管理员其实都能动到备份,那之后我才把一份不可变副本放到域账号删不掉的地方,并且每月真的恢复一台机器计时。文中提到要对 4720 新建账号和 4706 新建信任告警,我回去也要补上,我现在的告警只盯登录失败,这一块确实是盲区。