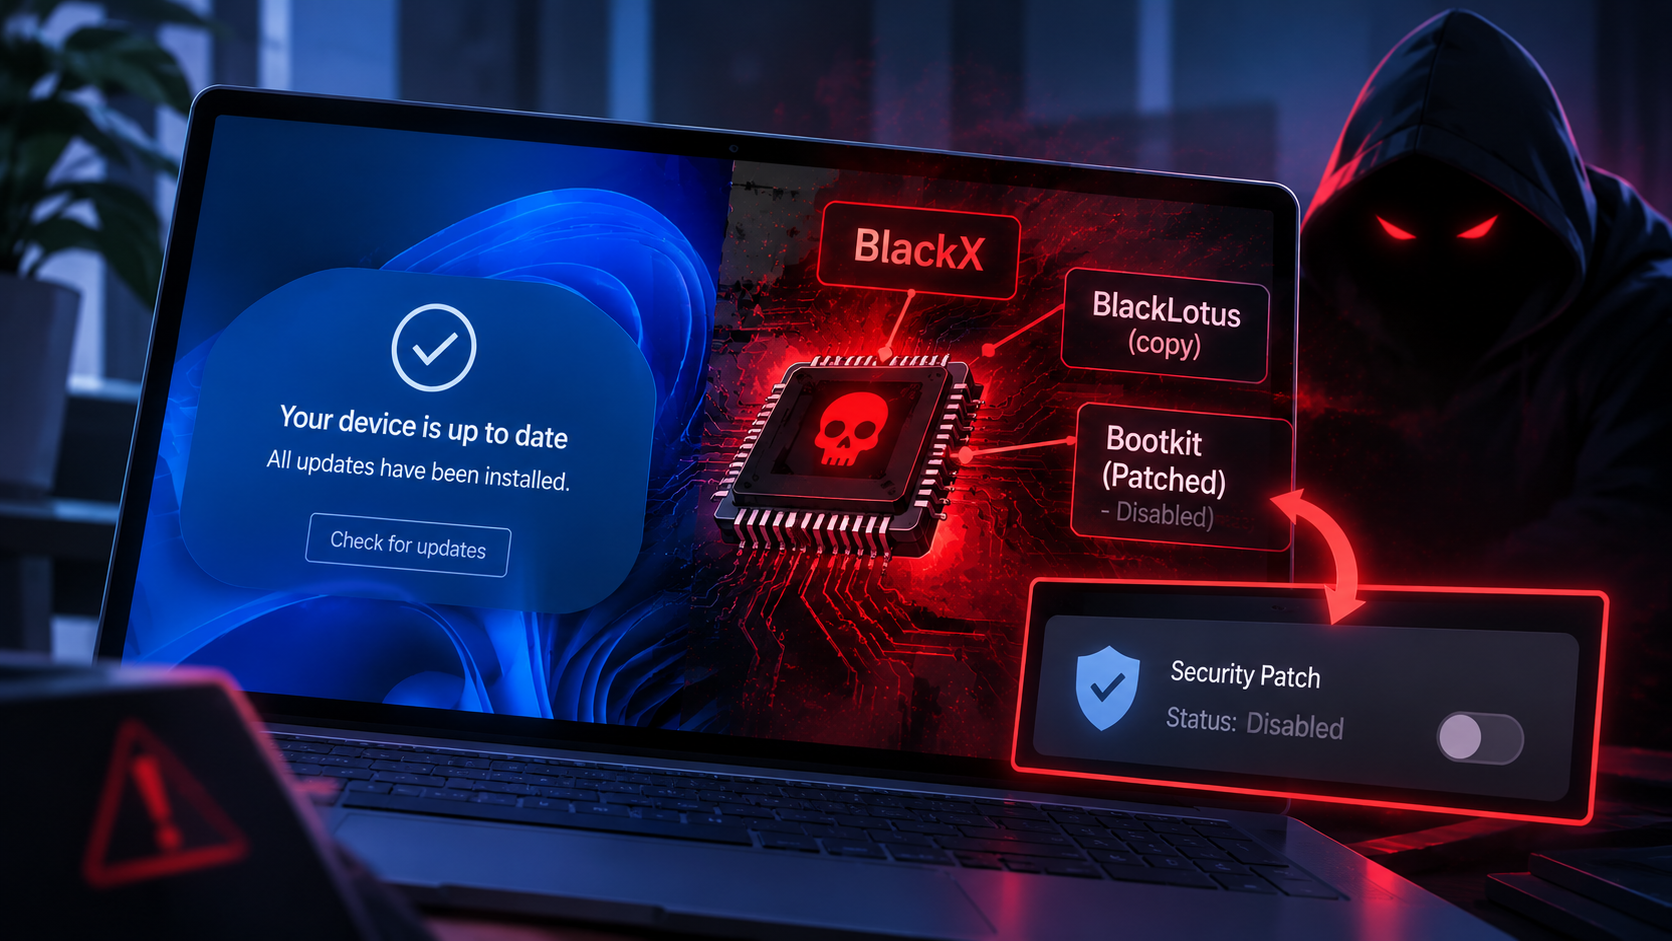
Fully patched machines still got a bootkit: BlackX, the BlackLotus copycat, and the patch nobody switched on
Summary
In early 2026, Kaspersky GReAT identified an APT campaign against diplomatic agencies in Tajikistan, Uzbekistan and Turkmenistan that involved a UEFI bootkit they named BlackX. On examination,