YYogeshwar Peela·Aug 23TryHackMe : Compiled WriteupTryHackMe room walkthrough covering ELF reverse engineering, Ghidra, objdump, strcmp checks, decoy strings, PIE analysis, and scanf parsing tricks.7 min read·exploitnotes.hashnode.dev
SSagun·Aug 5Malware Reverse EngineeringUnderstanding the Code Behind Malware7 min read·sagunwrites.hashnode.dev
SSagun·Aug 5Understanding PE FilesThe Structure Behind Windows Programs7 min read·sagunwrites.hashnode.dev
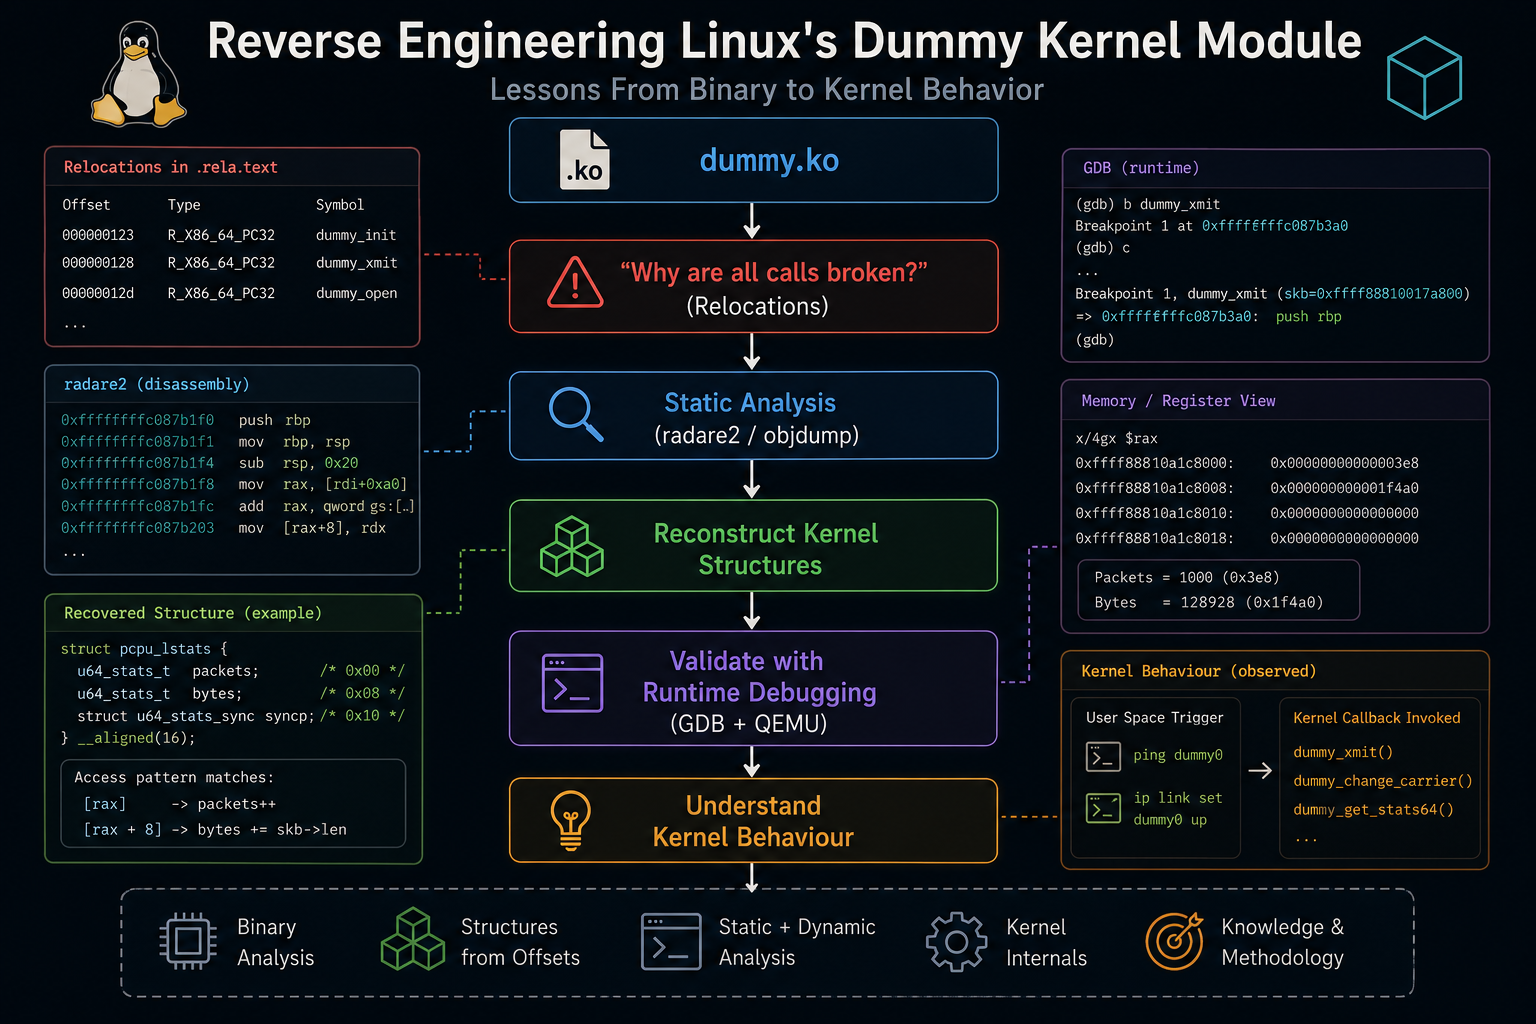
RRavidu Priyankara·Jul 28Reverse Engineering Linux's Dummy Kernel Module: Lessons from Binary to Kernel BehaviourLessons from reversing Linux's dummy kernel module using radare2, GDB and QEMU, covering relocations, callbacks, runtime analysis and more.7 min read·ravindu-priyankara.hashnode.dev
YYogeshwar Peela·Jul 12BronoCTF : No Laughing MatterSolve No Laughing Matter by converting A/H binary patterns into ASCII bytes, decoding the hidden message, and recovering the BroncoCTF flag.2 min read·exploitnotes.hashnode.dev11J
FFundacja Dobre Państwo·May 5Ghidra Book: Binary Analysis as Modern Data ScienceThis article provides an in-depth review of the second edition of "The Ghidra Book," charting the transformation of reverse engineering from a craft to a mature data science. Authors Kara Nance and Chris Eagle present the Ghidra framework as a compre...1 min read·fundacjadobrepasntwo.hashnode.dev
JJohn Ebinyi Odey·Feb 24, 2025Chimera: Code Injection in Linux ELF FilesChimera is a Linux code injection tool built for educational purposes for Cybersecurity experts and enthusiasts.1 min read·hotwrist.hashnode.dev