Feed
Discussion
Free-text actions like publish_content are where we added a check, since in our setup approval and sending are separate steps. When a reply needs approval, our reply sender checks a ledger and stops if the text differs from what was approved, so a reworded reply can't ship under an earlier yes.
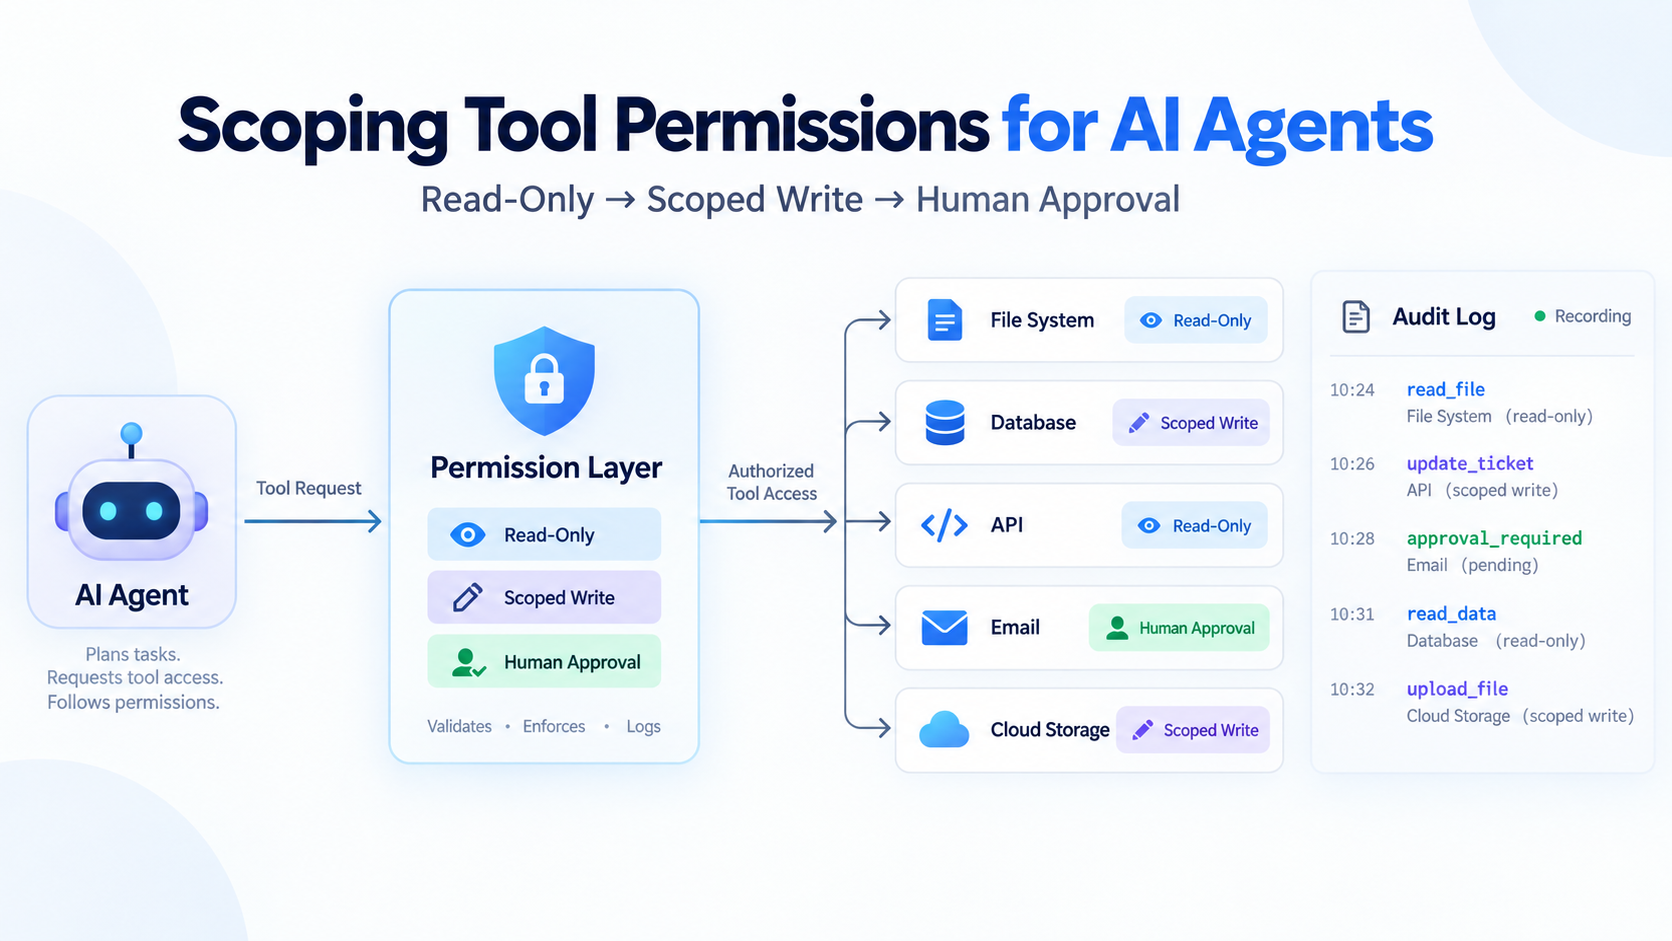
Permission scopes for agents should be boring and narrow. I start with read only on one repo path and open write only after the plan passes review. Wide access is how quiet mistakes get loud.
Vlad Zoff
I like the idea of scoping permissions explicitly because it moves the security boundary away from the model's judgment. One thing I'd add is that the permission model itself should be versioned and inspectable. Once an agent can call tools repeatedly across a workflow, debugging “why was this allowed?” becomes just as important as deciding whether the capability should exist.