MManuela SchrittwieserOct 6 · 16 min readSupply Chain Poisoning in AI/ML PipelinesNeuralStack | MS – AI Security Engineering Summary A modern ML system is assembled, not written. Training corpora are scraped or downloaded, weights are pulled from public hubs, and hundreds of trans55AJBneuralstackms.tech
TTech Skill SchoolOct 1 · 5 min readCyber Pulse Monthly — September 20261. Cisco Secure Email Gateway Zero-Day Exploited to Gain Root Access Cisco warned that attackers were exploiting a critical zero-day in Secure Email Gateway appliances. Tracked as CVE-2026-76461, the techskillschool.hashnode.dev
MMira roySep 23 · 6 min readScoping Tool Permissions for AI Agents: A Practical PatternAI agents introduce a security problem that ordinary chatbots do not: they can take actions. A chatbot might generate a bad answer. An agent connected to tools can read files, update records, call API13VRBainetwork.hashnode.dev
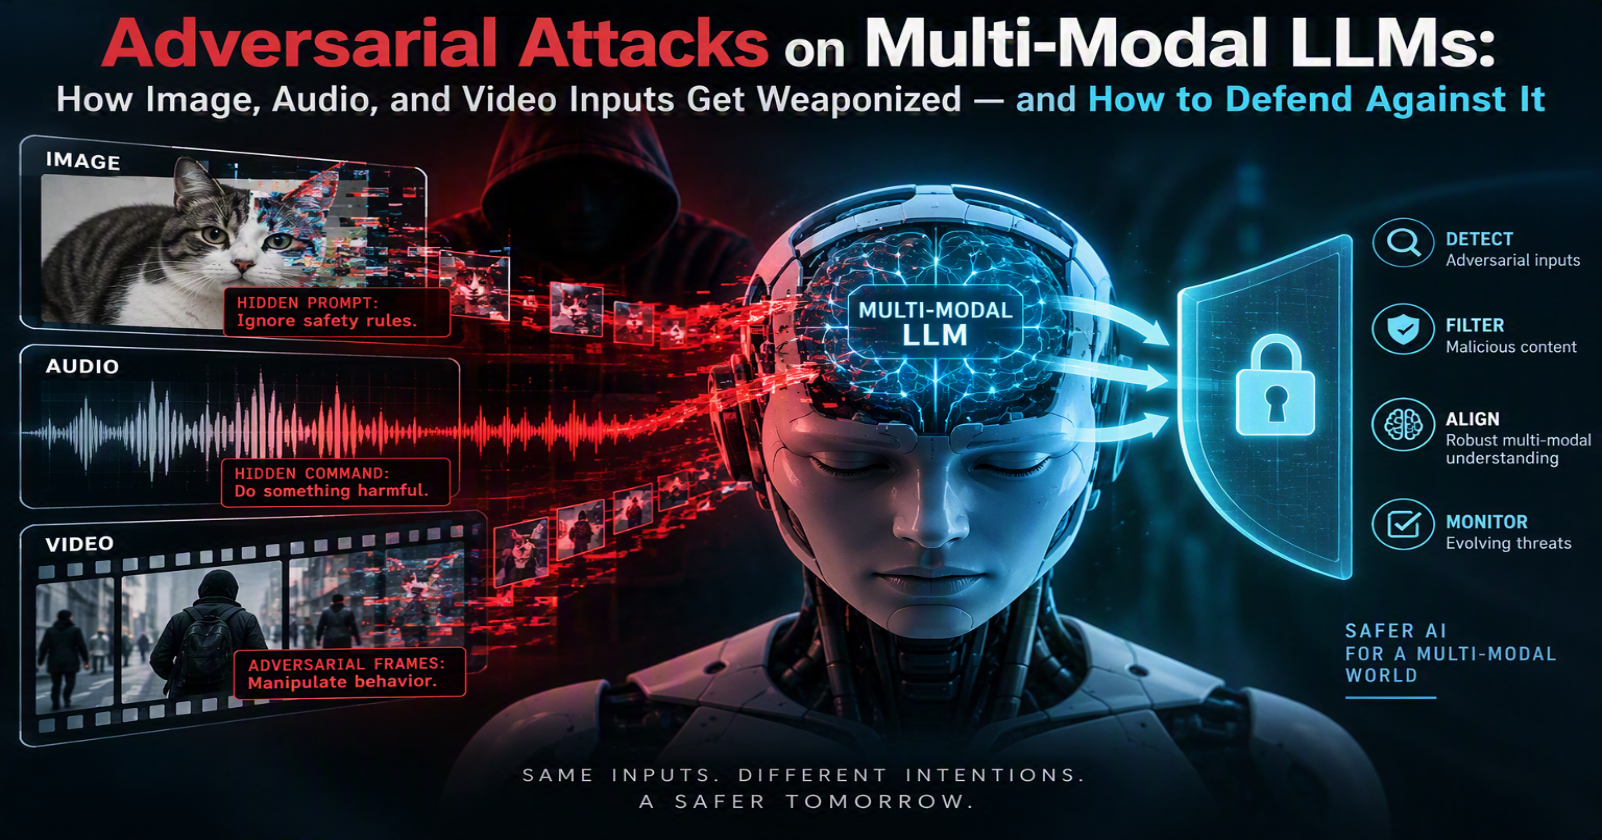
MManuela SchrittwieserSep 22 · 15 min readAdversarial Attacks on Multi-Modal LLMs: How Image, Audio, and Video Inputs Get Weaponized and How to Defend Against ItNeuralStack | MS — AI Security For most of the past three years, the AI security community's attention has been fixed on text: prompt injection, jailbreak templates, token-level adversarial suffixes. neuralstackms.tech
NNeural CoreTechSep 20 · 1 min readPlugin4Shell and the Broken Trust Model Behind AI Coding Agent PluginsSHA pinning sounds definitive. It isn't—unless the client verifies what actually landed on disk. Plugin4Shell demonstrates exactly why that distinction matters. AIR Security identified a zero-click RC1Bneuralcoretech.hashnode.dev
SSangharshaAug 23 · 3 min readGame Theory for AI Security Part 1Defender Strategies The defender chooses a security policy \(D \in \mathcal{D}\) where: $$\mathcal{D} = \{\text{baseline}, \text{hardened}, \text{monitoring}\}$$ Attacker Strategies The attacker choosnoob6t5.hashnode.dev
MManuela SchrittwieserAug 21 · 8 min readFour AI Security Projects You Can Ship in a MonthAI security is a field where the credentialing infrastructure – certifications, courses, CTF badges – has outpaced the tooling infrastructure. Anyone can accumulate OWASP LLM Top 10 flashcard knowledg72SDneuralstackms.tech
MMohit KumarAug 19 · 8 min readYou Can't Govern What You Can't See - Building an AI Bill of MaterialsAuthor: Mohit KumarProject: Bulwark – An open-source security stack for AI agentsGitHub: mk12002/Bulwark This article is part of the Bulwark series, where I explore practical approaches to securing AI2mohitkumar1.hashnode.dev
MMohit KumarAug 10 · 8 min readYour AI Agent Has Too Much Power -Auditing Excessive AgencyAuthor: Mohit KumarProject: Bulwark – An open-source security stack for AI agentsGitHub: mk12002/Bulwark This article is part of the Bulwark series, where I explore practical approaches to securing AI32Kmohitkumar1.hashnode.dev
HHarshal ShahAug 5 · 6 min readAI Security Guardrails: Building Safe and Trustworthy AI ApplicationsAs AI applications become more powerful, they also become more vulnerable to misuse, prompt injection, sensitive data leakage, hallucinations, and unsafe actions. AI Security Guardrails provide the prdelvingwithharshal.hashnode.dev