YYogeshwar Peela·Oct 17HackTheBox: Odori WriteupExplore the HTB Odori machine walkthrough: crack BitLocker, extract Windows credentials, bypass restricted SFTP, and escalate to root.27 min read·exploitnotes.hashnode.dev
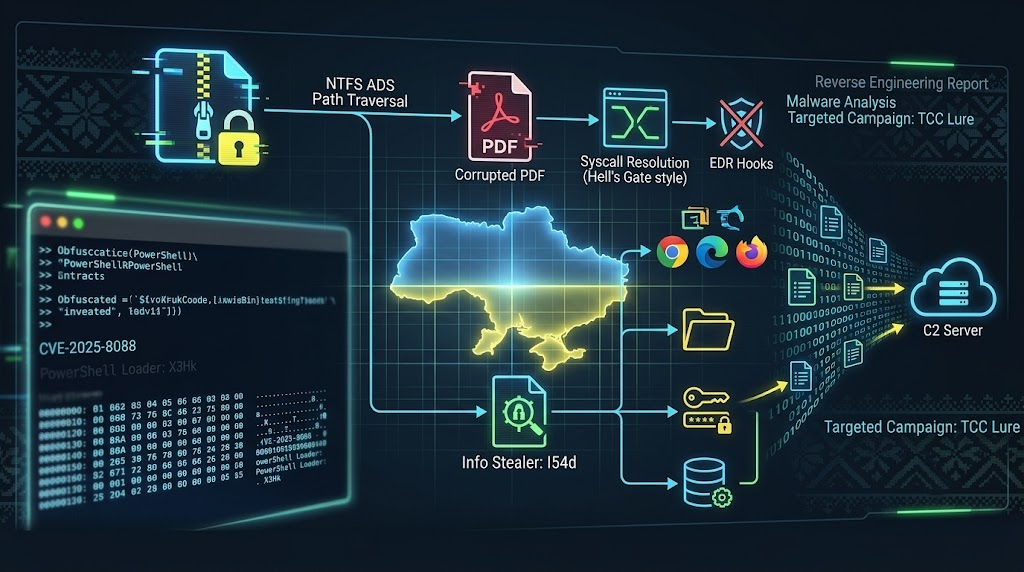
NNguyễn Đăng Hưng·Jul 22Beyond the Archive: CVE-2025-8088 Stealer Targeting Ukraine0. Overview This report details a targeted cyber-espionage campaign conducted by the Russia-aligned threat actor group APT SHADOW-EARTH-066 (also tracked by CERT-UA as UAC-0226), delivering an updated36 min read·bluecyber.hashnode.dev
RRCE.0ps·Feb 27Credential Dumping with NetExec (nxc)Learn how attackers use NetExec (nxc) to dump credentials in Active Directory environments.12 min read·rceops.hashnode.dev