AAdminPackStudioOct 15 · 18 min readAADSTS50105 User Not Assigned to a Role for the Application: A Read-First Enterprise App Assignment TriageHelpdesk: "Finance can't open the new expense app. Red page says AADSTS50105, the signed in user is not assigned to a role for the application. IT already tried from a Global Admin account and it work1adminpackstudio.hashnode.dev
AAdminPackStudioOct 14 · 10 min readAADSTS53003 Blocked by Conditional Access: A Read-First Sign-In Log TriageA user forwards a screenshot: "You cannot access this right now" and, under More details, AADSTS53003: Access has been blocked by Conditional Access policies. The access policy does not allow token isadminpackstudio.hashnode.dev
AAdminPackStudioOct 14 · 12 min readEntra ID Break-Glass Accounts: Best Practices After Mandatory MFAA lot of tenants still have the same break-glass setup: one cloud-only Global Admin, a long password in a safe, and "excluded from MFA" written on the envelope. Microsoft's mandatory MFA enforcement madminpackstudio.hashnode.dev
KkbentisOct 4 · 7 min readHow much of your Intune tenant is deploying to nobody?Intune can tell you whether an app or a policy is assigned. That part's easy. What it won't tell you is whether the assignment makes any sense. A compliance policy whose only assignment is an exclusio1kbentis.cloud
MMihai_LeanZeroOct 2 · 19 min readMicrosoft Graph to Jira Assets User IngestionMicrosoft Graph to Jira Assets User Ingestion The ingestion system consists of three main components: Microsoft Graph API Client - Handles OAuth 2.0 authentication and fetches user data including manleanzero.hashnode.dev
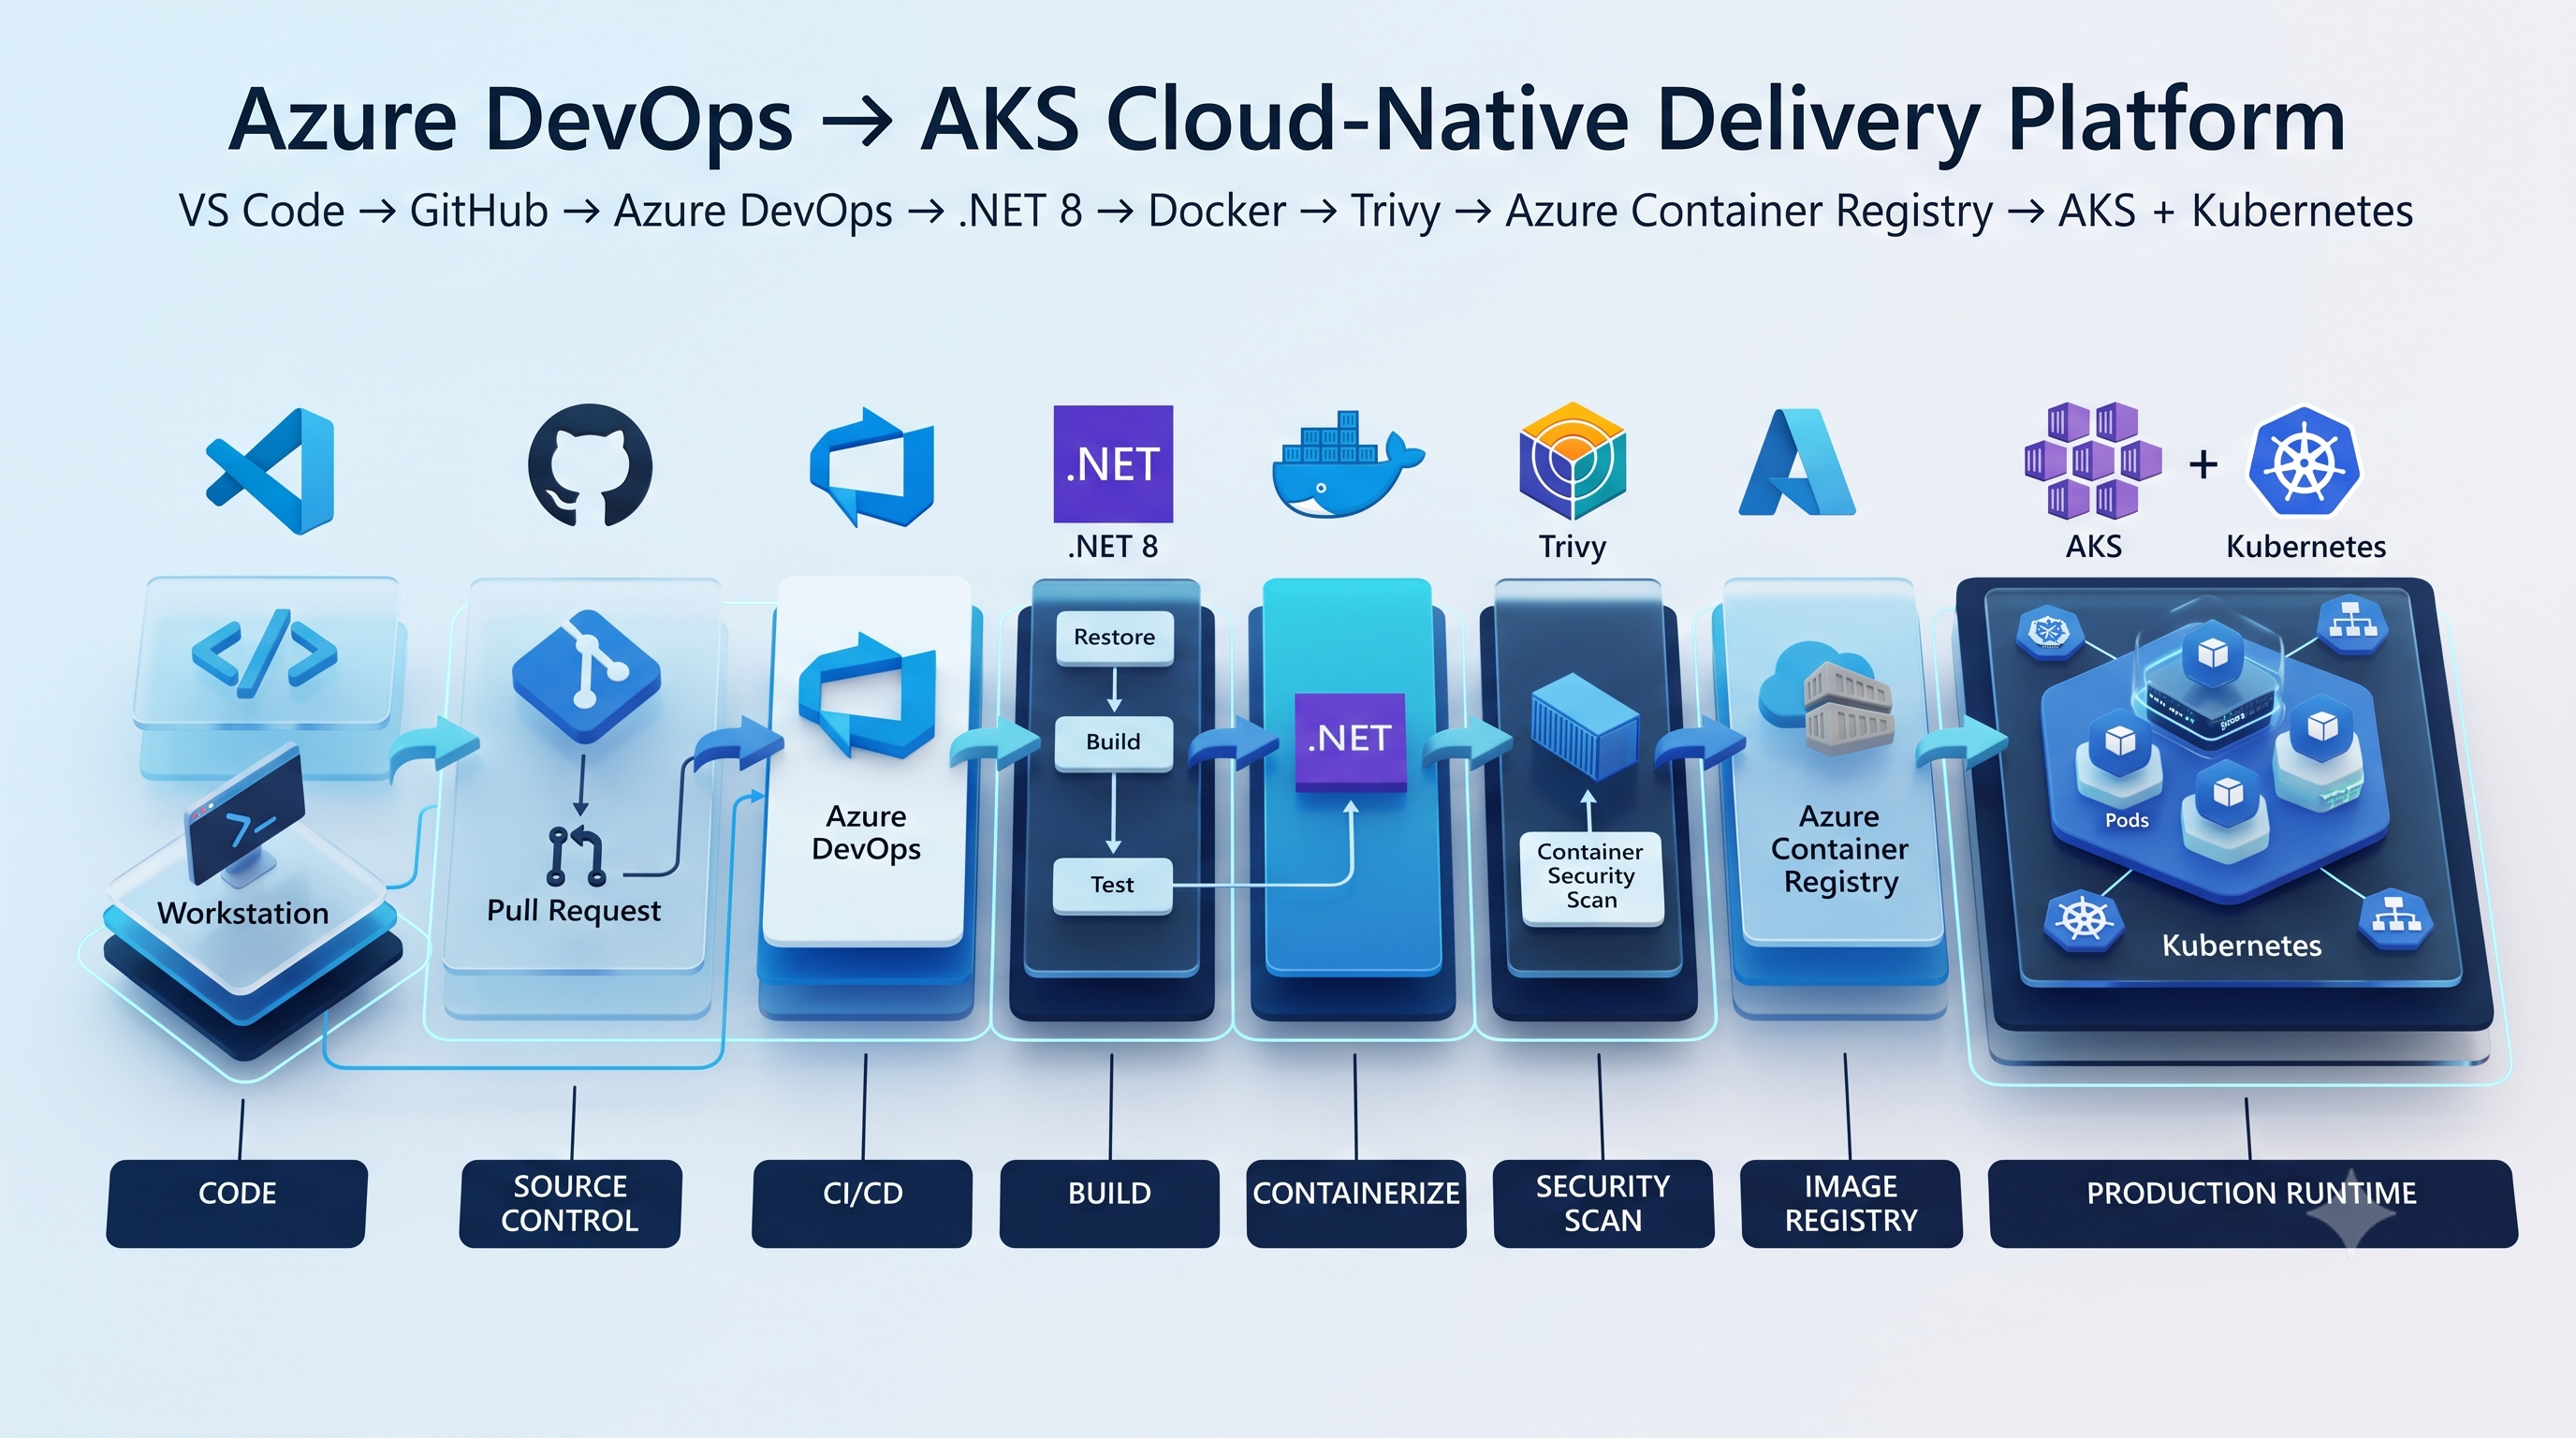
HHardik AroraSep 13 · 7 min readMy Breaking and LearningJourney with Azure DevopsI've been working on a small DevSecOps project to get more hands-on with Azure DevOps and cloud Checkout Github Overview here I wanted to understand what happens between: Developer ↓ Azure Devopshardik0811arora.hashnode.dev
DDaniel WeberAug 19 · 5 min readWhy Microsoft 365 Group-Based Licensing Fails Quietly Group-based licensing solves an important operational problem. Instead of assigning Microsoft 365 licenses manually, administrators connect entitlement to group membership and let the platform processengineering-field-notes.hashnode.dev
KKajal DhanjalAug 18 · 12 min readAnatomy of an identity compromiseWhy nothing fired When a detection misses, the first instinct is to blame the rule. Wrong threshold, wrong table, wrong logic. Sometimes that is exactly right. But there is a class of intrusion where kajalbuilds.hashnode.dev
SSachin NandanwarAug 5 · 14 min readSecure AI Functions in Microsoft Agent Framework with Microsoft Entra OAuth Role-Based Access Control Lets take a scenario where you have an MAF (Microsoft Agent Framework) AIAgent that has tool calls to multiple AIFunctions. You definitely wouldn't want an AIAgent to blindly invoke every available to1azureguru.net
SSachin NandanwarAug 3 · 11 min readBuild AI Agents with Microsoft Agent Framework to Access Azure Services Using Entra OAuthImagine a scenario where you have an AI agent that needs to access Azure services, such as Azure Storage. Simply granting the agent open and unrestricted access to Azure resources is not an option. Do1azureguru.net