BBrandon Sooknanan2d ago · 5 min readHow to test a vulnerability reporting tool in 14 daysMost free trials end the same way. You sign up, click around with the sample data, get pulled into other work, and the trial expires before you have tested anything that matters. A vulnerability reporblog.varaxontech.com
BBrandon Sooknanan2d ago · 5 min readFixed, accepted or ticketed: close the loop on every vulnerability findingMost vulnerability reports end the same way. The scan runs, the PDF goes out, and three months later the same findings are back in the next PDF. Nobody decided to ignore them. Nobody decided anything blog.varaxontech.com
BBrandon Sooknanan2d ago · 4 min readTurning vulnerability scan results into billable remediation workA vulnerability scan is one of the best sources of project work an MSP has. It is also one of the easiest to give away for free. The pattern is familiar. The scan finds 200 issues. Some are patches yoblog.varaxontech.com
BBrandon Sooknanan4d ago · 4 min readEnd-of-Life Software in Vulnerability Reports: What to Do When There's No Patch ComingMost findings in a vulnerability report have a fix: install the update, change the setting, restart the service. End-of-life software is different. When a vendor stops supporting a product, new vulnerblog.varaxontech.com
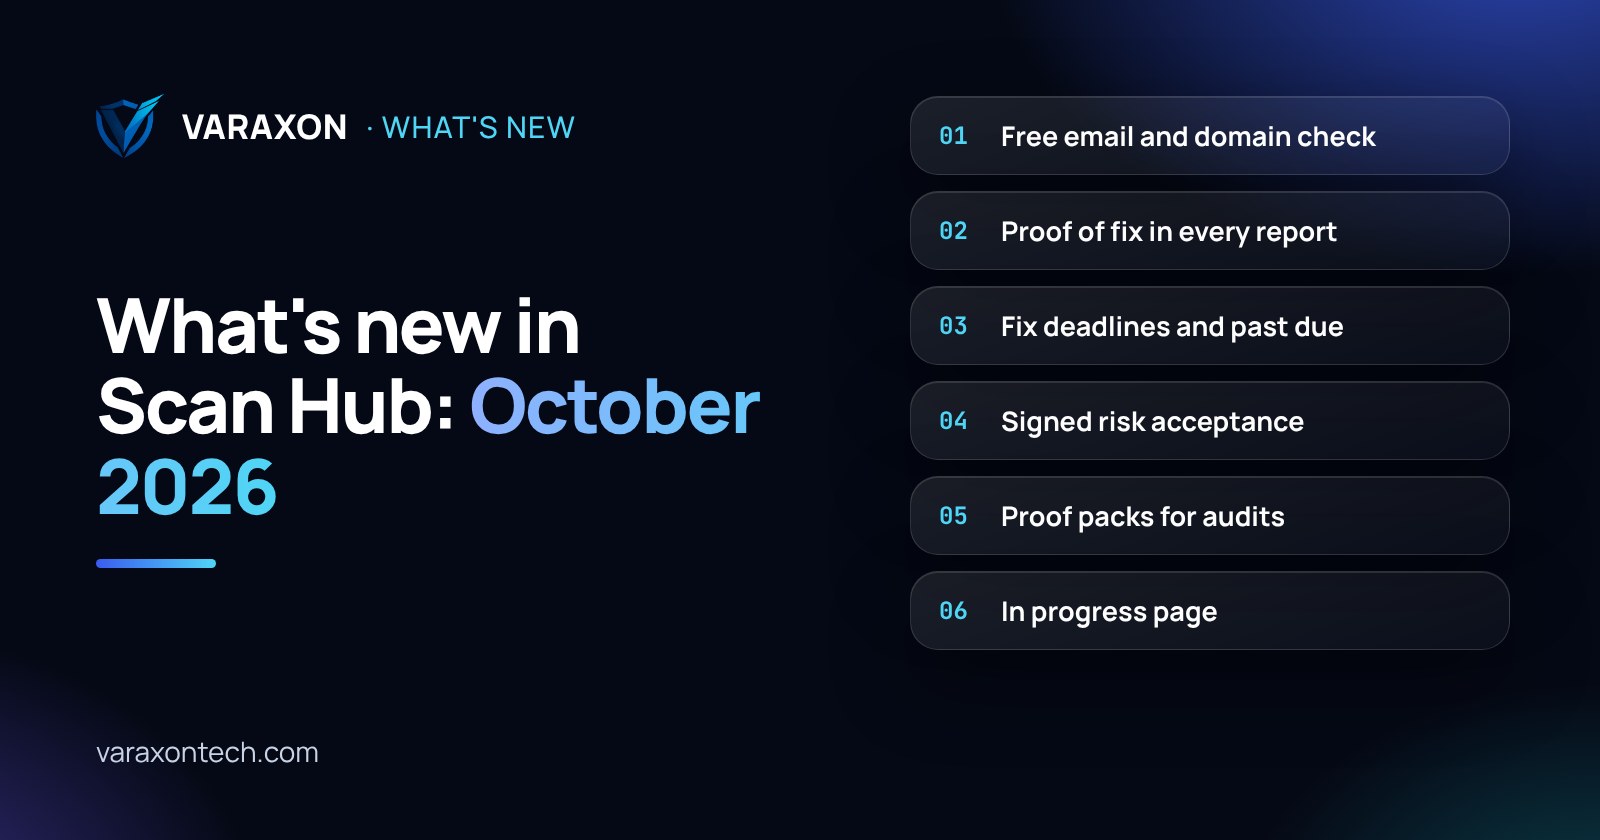
BBrandon Sooknanan4d ago · 5 min readWhat's new in Varaxon Scan Hub: October 2026Key takeaways New: a free email and domain check, graded A to F, for your own domain, your clients and their suppliers. Reports now prove what was fixed since the last scan, with deadlines and a pastblog.varaxontech.com
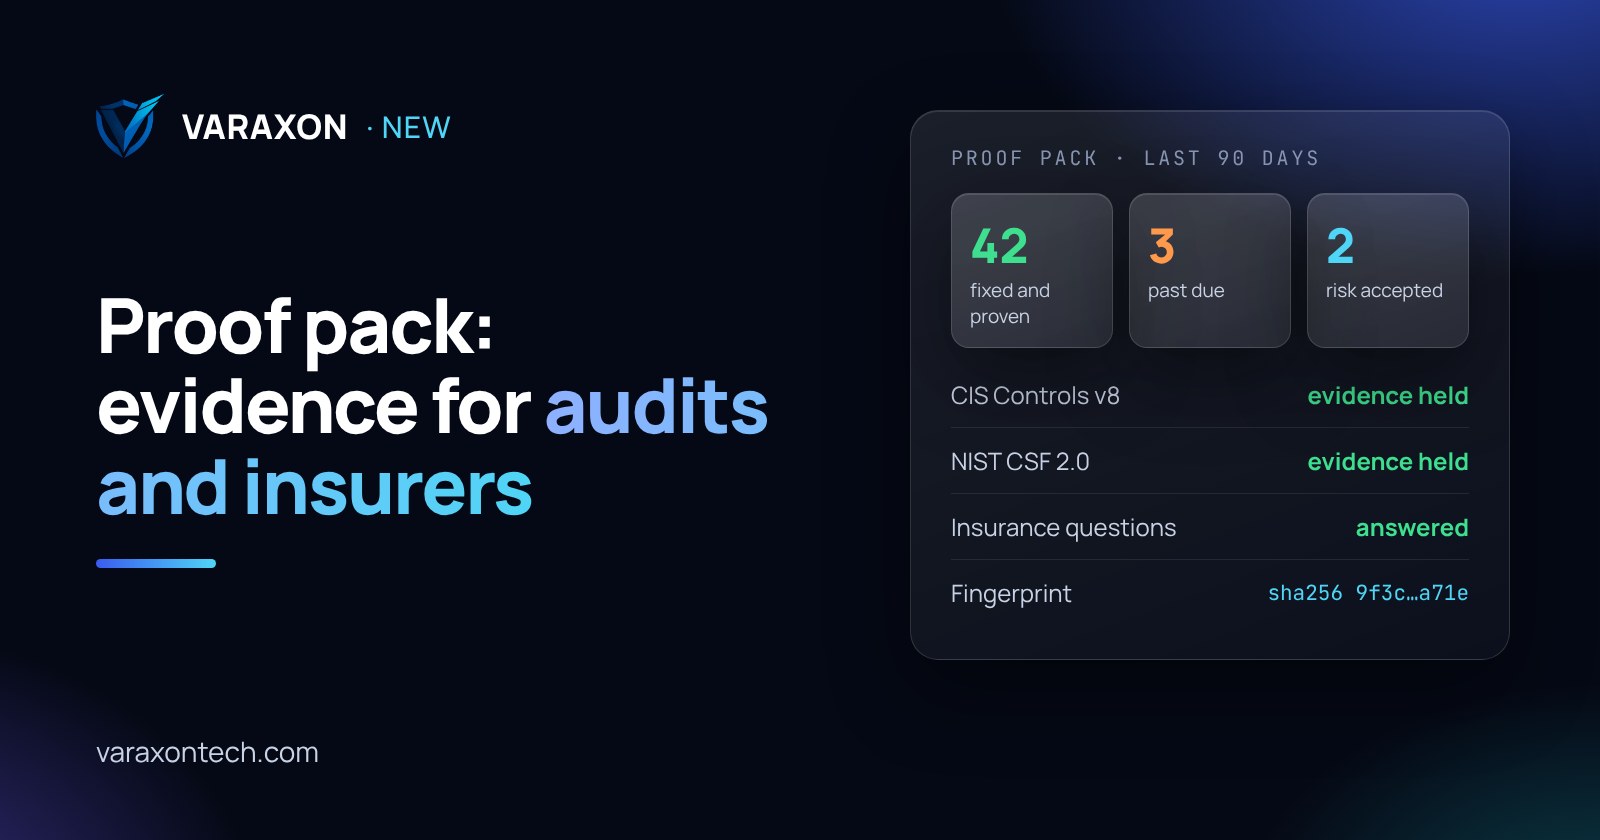
BBrandon Sooknanan4d ago · 6 min readProof pack: evidence of your vulnerability work for audits, insurers and renewalsKey takeaways Every tracked finding now has a fix deadline, and a past due list shows what is late and by how many days. When a client won't fix something, they can accept the risk by signing online,blog.varaxontech.com
BBrandon Sooknanan4d ago · 4 min readProof of fix: show clients what you fixed since the last scanEvery month you patch, rescan and send the client a report. And every month the report shows a long list of what is still wrong, while the work your team did is invisible. Proof of fix changes that. Vblog.varaxontech.com
BBrandon Sooknanan4d ago · 4 min readA Critical CVE Just Dropped. What MSPs Should Do in the First 48 HoursIt happens a few times a year. A vulnerability in a VPN appliance, a firewall, a file-transfer tool or a widely used library gets announced, it's rated critical, and within hours there are reports of blog.varaxontech.com
BBrandon SooknananOct 22 · 4 min readRisk Acceptance: How to Document a Vulnerability Your Client Won't FixSooner or later a client says no. The finance system only runs on an old version of Windows. The vendor won't support the patch. The fix means a weekend of downtime they can't afford this quarter. Thablog.varaxontech.com
BBrandon SooknananOct 22 · 4 min readFalse Positives in Vulnerability Scans: How to Verify Them Without Hiding Real RiskEvery scan has a few findings that make you squint. The web server is flagged for an Apache flaw, but the box runs nginx. A Windows patch shows as missing on a machine you updated yesterday. A client blog.varaxontech.com