KK4M1_n0_73in0xk4m1.hashnode.dev·3d ago · 15 min readDC-1: Drupalgeddon2, SUID binary to root shellSo I am going to be starting with this vuln machine. I'd say I'm starting to carve out a methodology with machines like this. First of all, I'll start with a netdiscover to figure out the IP address o00
SASuresh Attanayakeinsureshatt.com·5d ago · 7 min readA Practical Guide to AI-Assisted Pentesting for AppSec TeamsPentesting is a core part of any application security program. Specifically, some organisations use pentesting as the final security gate before production. However, for the AppSec team, pentesting is20
00x8r41nr07inbraindump.0x8r41nr07.xyz·Sep 29 · 5 min readI Wrote "Being Non-Guided" Twice in One Day.Part 15 of an ongoing series. [Start from Part 1.] Wednesday night I was filling in my daily wrap-up, the same template I've used for months — what sparked new ideas, what frustrated me, two separate 00
FFalkenkralleinttpsandtricks.hashnode.dev·Sep 27 · 9 min readHow To Hack (almost) Every KeypadDisclaimer I do not have official authorized field experience since I am a student and research is limited for this topic. So most of the techniques shown are brainstormed with a mind shaped by listen00
Aarosioninarosion-labs.hashnode.dev·Sep 23 · 11 min readBabyTwoBabyTwo is a medium-difficulty Windows machine set in an Active Directory environment. The initial foothold is gained through password guessing and the abuse of Windows logon scripts. Privilege escala00
Iinfoincodebridgeagency.hashnode.dev·Sep 21 · 3 min readThe Laravel Vulnerability We Find in 60% of SaaS Apps (And the 2-Line Fix)We audited 40 SaaS applications last quarter. 60% had some version of the same vulnerability in production. Not in staging. Not in an old branch. In production, serving real users, right now. It's cal00
AJAmartya Jhainsecurity-research.hashnode.dev·Sep 17 · 6 min readYour Perimeter Will Fail. The Real Question Is How Far an Attacker Gets After.TL;DR: External tests and scanners check your perimeter. Neither answers the question that decides how bad a breach gets: once someone is inside, how far can they go? That is what internal penetration00
AJAmartya Jhainsecurity-research.hashnode.dev·Sep 17 · 8 min readYour Pentest Report Says "SQL Injection on /api/search." It Won't Say Which Line.Your Pentest Report Says "SQL Injection on /api/search." It Won't Say Which Line. TL;DR: External penetration testing still matters, but the classic once-a-year model has six structural gaps that hurt00
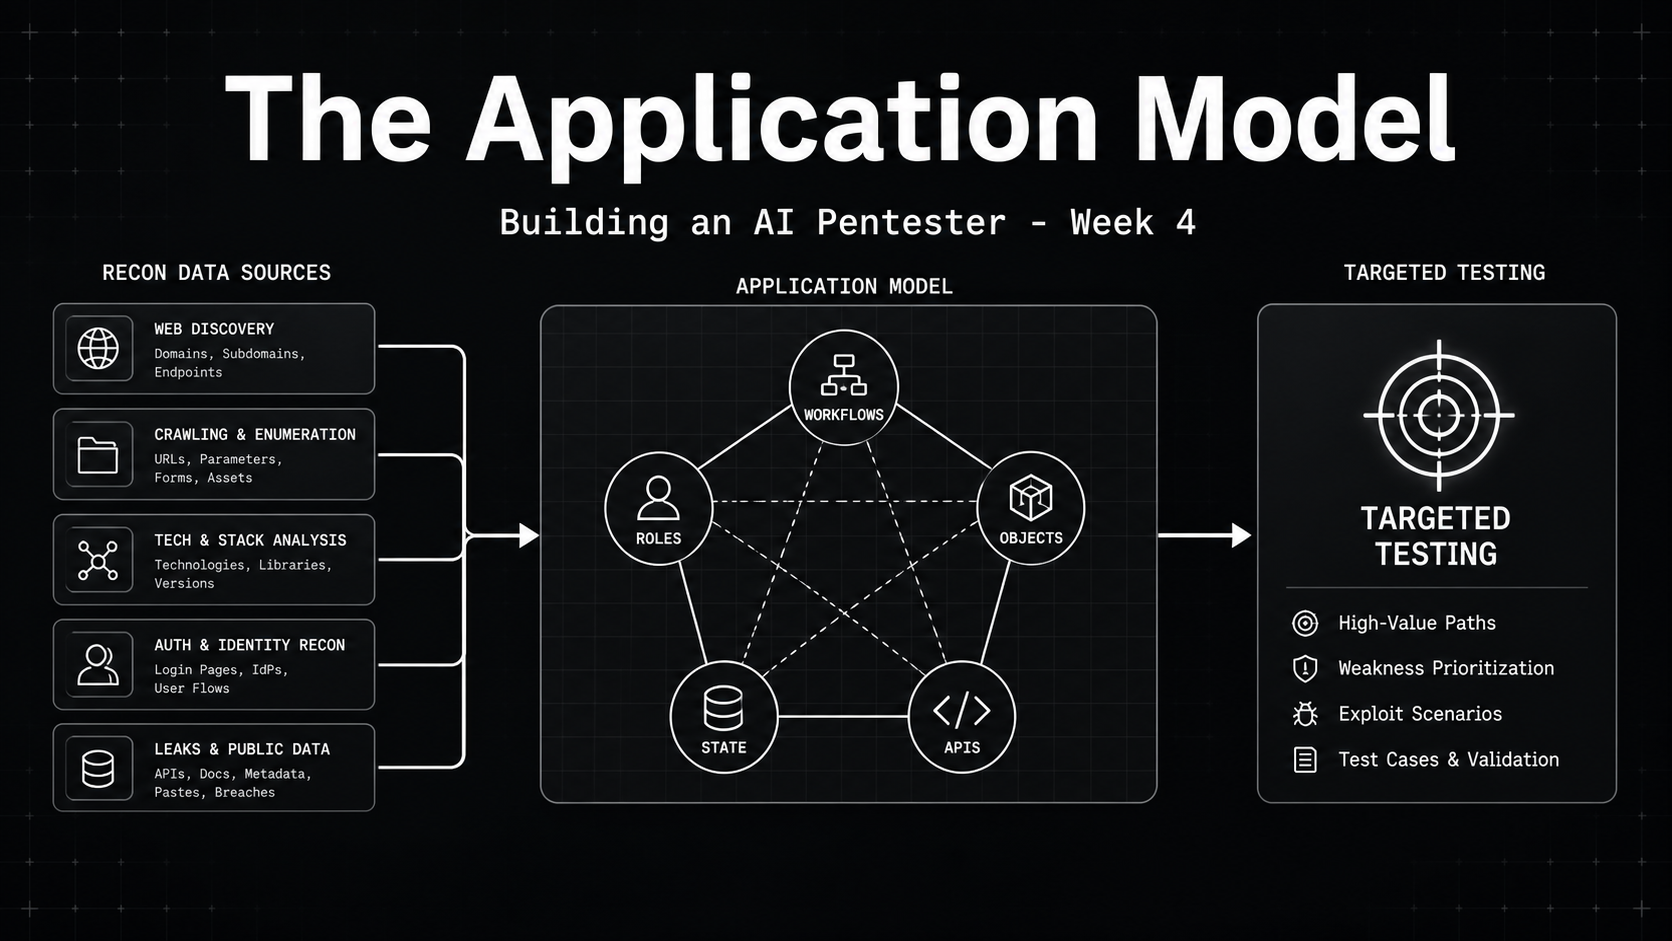
KPKrishn Patelinai-pentester.hashnode.dev·Sep 14 · 7 min readBuilding AI Pentester Week 4:From Endpoints to Security Questions , Building AI Pentester's Application ModelLast week, I changed Recon from a tool launcher into a staged pipeline. It now ends with a correlated surface instead of asking Hunt to interpret unrelated files from every tool. That handoff still ha00
JJebitokinsharonjebitok.com·Sep 11 · 10 min readNoScope: Finding RCE (TryHackMe)Link to the challenge on TryHackMe: NoScope: Finding RCE Introduction Alf.io(opens in new tab) is an open-source, Java/Spring Boot event management platform used by conference organizers, sports clubs00