AAngusKit3d ago · 7 min readReplace Semgrep, Trivy, and Gitleaks scripts with one scan gateThe merge request is green, then release is blocked by a secret or dependency CVE—usually because Semgrep, Trivy, and Gitleaks each own a job: three logs, three exit codes, no shared Finding, no shareanguskit.hashnode.dev
GGeorge EzejioforSep 13 · 26 min readHarden & Lockdown RKE2 Cluster with a 4-Layer DevSecOps StackIntroduction Before you move furniture into a new house, you install the locks, the cameras, and the gates. Kubernetes is no different, yet engineers constantly build clusters inside-out, treating secgeorgeezejiofor.com
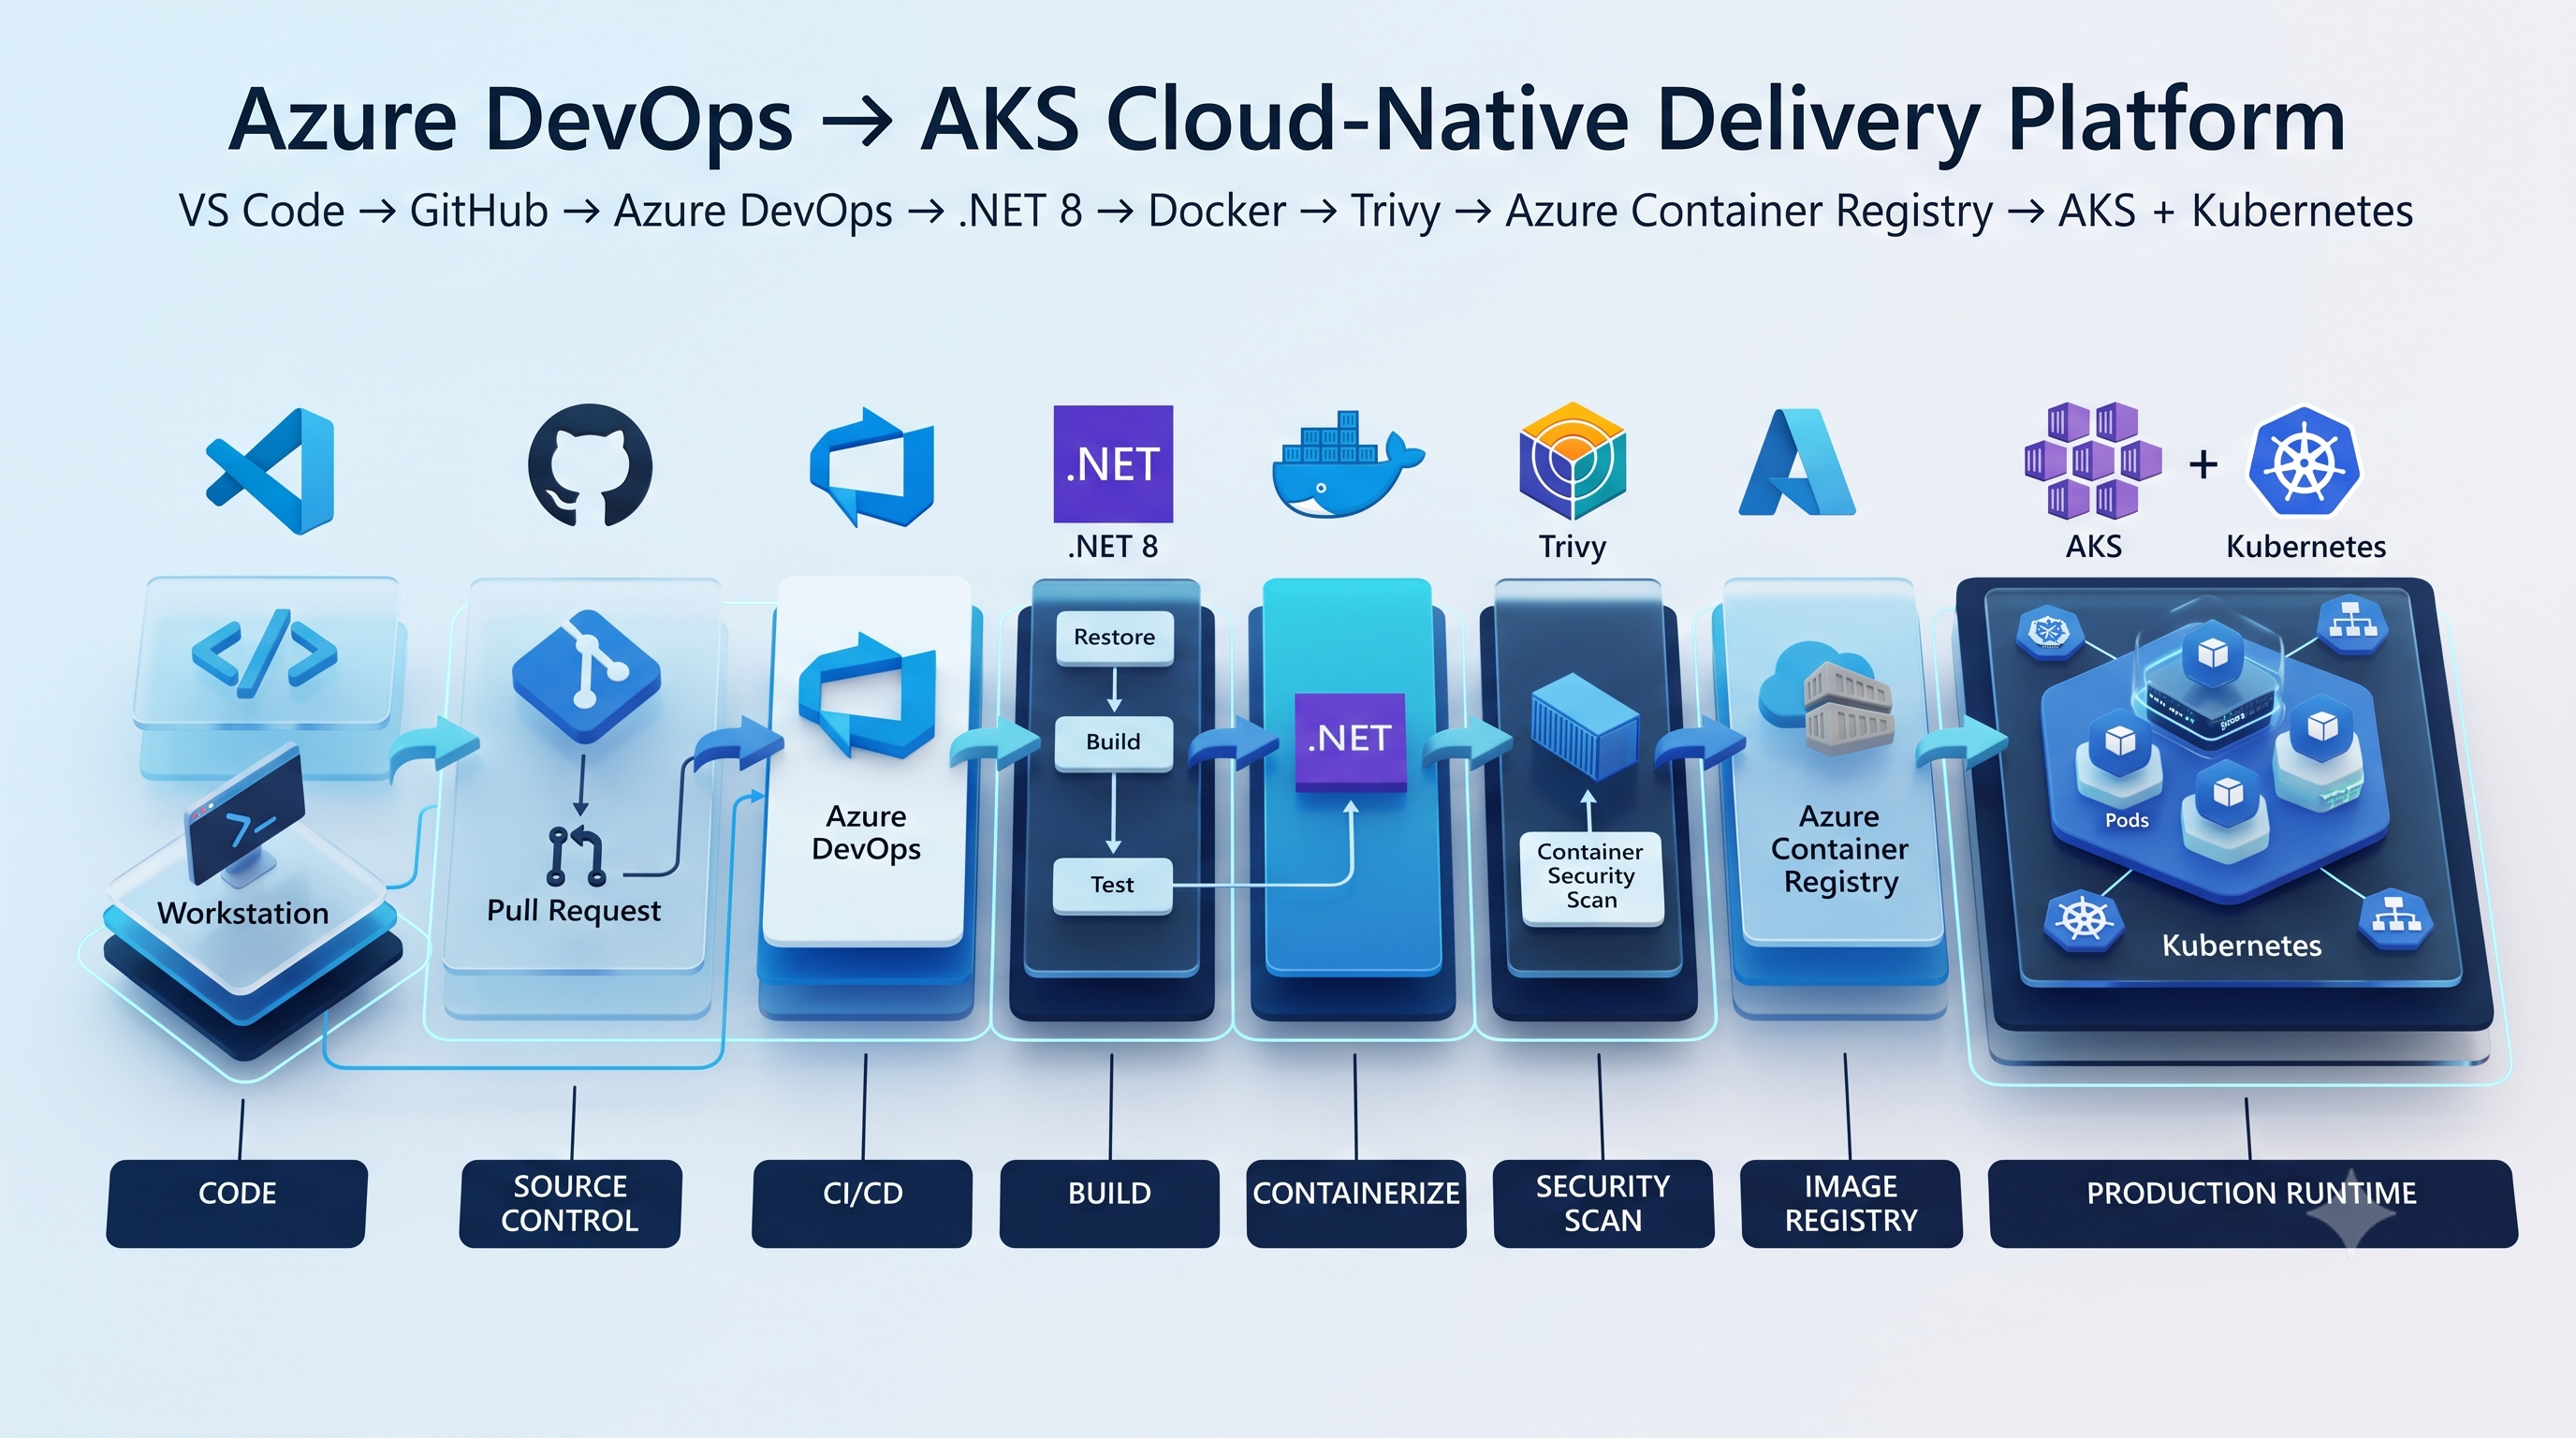
HHardik AroraSep 13 · 7 min readMy Breaking and LearningJourney with Azure DevopsI've been working on a small DevSecOps project to get more hands-on with Azure DevOps and cloud Checkout Github Overview here I wanted to understand what happens between: Developer ↓ Azure Devopshardik0811arora.hashnode.dev
HHarshit SahuSep 7 · 12 min readSecure Docker Images & Container ScanningContainers transformed software delivery by making applications portable, lightweight, and consistent across environments. But every Docker image carries more than application code—it also carries an harshitsahu2311.hashnode.dev
MMatt BrownJun 4 · 15 min readTrivy Operator: The Scanner That Leaves ReceiptsI’ve been working through a bigger Kubernetes security stack, and I wanted to come back to one of the simpler pieces: scanning. Not runtime blocking. Not admission control. Just scanning. Trivy Operatcloudsecburrito.com
MMatt BrownJun 4 · 10 min readDeploying OSS Kubernetes Security ConsoleThe first post laid out the idea: Kubernetes security tools already produce a lot of useful data, but most of it lands in separate places. Trivy Operator writes vulnerability and configuration finding4cloudsecburrito.com
HHardik AroraJun 1 · 7 min readBuilding a Zero-Egress, AI-Driven DevSecOps Pipeline: My Journey with SupplyChain-Guardian-AI As platform engineering evolves, we are constantly battling alert fatigue. We run our vulnerability scanners, generate endless Software Bill of Materials (SBOMs), and drop massive PDF reports onto devhardik0811arora.hashnode.dev
MMatt BrownMay 28 · 12 min readBuilding an OSS Kubernetes Security Console with MCPA single Kubernetes security finding is rarely the whole story. That is true whether the signal comes from runtime detection, vulnerability scanning, posture assessment, or admission control. “Shell cloudsecburrito.com
KKrishna BagalMay 27 · 8 min readI Built an Open-Source Vulnerability Scanner with a Real-Time Dashboard — Because Nothing Else Did It AllThe Problem That Started It All If you run servers, write code, or manage containers, you already know the uncomfortable truth: vulnerabilities, exposed secrets, and misconfigurations are everywhere. 93KVSblog.krishnabagal.com
AAkaeze KosisochukwuMay 25 · 9 min readBeyond Shift Left: Runtime Security with Falco on AWS EKSThe whole concept of "Shift Left" revolves around proactive scrutiny, catching issues before they ever reach the environment where real users are. This spans everything from performance and reliabilit2audrey01.hashnode.dev