FeedDiscussion
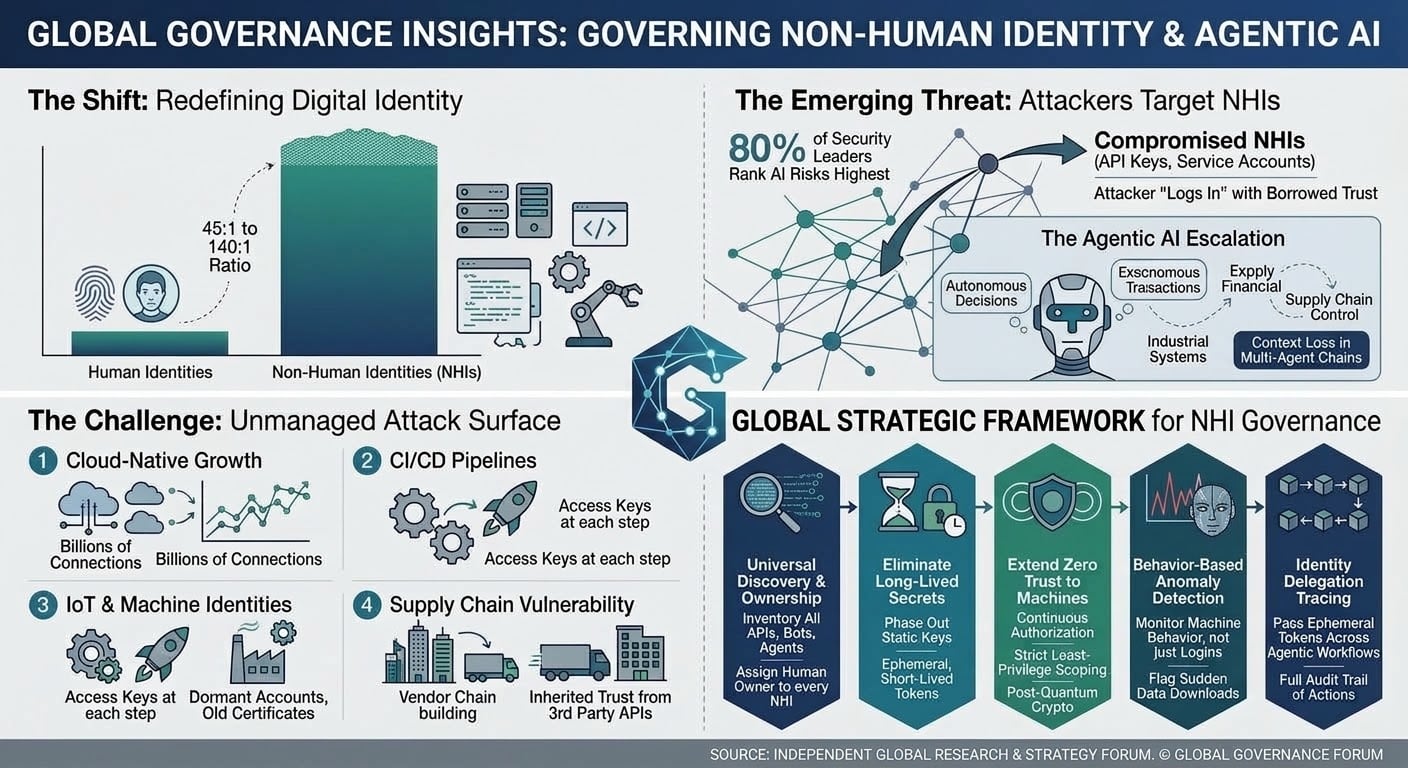
Great breakdown of the NHI problem space, especially the borrowed trust angle. Machine keys dont have contextual expiry, they rarely have two-factor, and once one leaks theres no clean way to trace which agent used it for which downstream call. Most orgs invest heavily in secret rotation and vault hygiene but the delegation tracing gap - who authorized what and from which workflow - is where incidents actually happen. Managed PKI and short-lived certs seal the secret side but leave that whole audit layer untouched. Thats the part that makes NHI management feel like a blind spot despite all the investment in vault tooling. At CAI weve been looking at binding agent identity to verifiable on-chain attestations so every delegation leaves a verifiable trail. Curious if youve explored that direction or if your approach stays in the vault layer.
This is a clear explanation of a problem most small businesses don't realise they have. In the Microsoft 365 tenants I review, non-human identities often hide in plain sight: old app registrations in Microsoft Entra ID, a scanner or backup tool connected years ago, or a third-party app granted broad permissions and never reviewed.
The "assign a human owner to every NHI" point is the one I would underline. When nobody owns an app registration, nobody notices when its secret is about to expire, or worse, when it quietly still has access to every mailbox long after the tool was replaced.
For smaller organisations without dedicated identity teams, where would you suggest starting? A simple quarterly review of app registrations and their permissions feels like the most realistic first step.
Kartik N V J K
AI Developer | Making AI reliable, trustworthy & accessible to everyone | Active community contributor
The 45-to-1, and up to 140-to-1, ratio of non-human to human identities is the stat that reframes the whole access problem, most orgs are securing the smallest slice. Moving from static keys to ephemeral tokens is the right instinct, though the rotation and revocation story is where I've seen it get hard. How are you tracking which NHIs are actually still in use versus abandoned and over-permissioned?