CCyber Knight10h ago · 4 min readA CVSS 10.0 Bug Sat Inside GitLab for 12 Years. It Lived in the Regex Engine.Twelve years ago, somebody compiled a regular expression. Not in a browser. In a server-side library called Onigmo — the Ruby regex engine GitLab bundles — quietly turning patterns into executable matnulltrace.hashnode.dev
SSulakshana Karunarathne10h ago · 4 min readWhy Your Database Will Crash in a Kubernetes Deployment (And Why You Need a StatefulSet)The Naive Mistake: "Everything is a Deployment" When developers first start containerizing applications for Kubernetes, it is tempting to treat every workload the same way: apiVersion: apps/v1 kind: Ddevseccloud.hashnode.dev
KKimchi2d ago · 10 min read12 Security Questions Every AI Coding Agent Needs to Be Able to AnswerOriginally published on the Kimchi blog by JJ Lim. Your security team has a questionnaire. Every vendor gets it, and most AI coding vendors answer it with a trust portal link and a meeting request, nogetkimchi.hashnode.dev
AAmit Shukla2d ago · 9 min readMCP security: how a malicious MCP server can steal your secrets, and how to lock it downAdding an MCP server takes one line. Someone shares a repo, the README says npx -y some-mcp-server, you paste it into your config, and a few seconds later your AI agent has new tools. It feels like inamitshuklabag.hashnode.dev
VVictor Okoroafor3d ago · 6 min readMy Policy-as-Code Check Passed. It Never Read the Policy.In my last post, I showed how OPA and Conftest block over-privileged IAM roles before anything gets deployed. I ended with a warning: there's a case where the check passes when it shouldn't. This is tvictorokoroafor.hashnode.dev
DDibyadipan Bhattacharya3d ago · 10 min readHow AST-Based Static Analysis Catches Dockerfile Vulnerabilities That Regex Scanners MissA multi-stage build with obfuscated instructions or unpinned stage contexts bypasses standard regex linters with minimal effort. Consider this production Dockerfile: # syntax=docker/dockerfile:1 FROM dibyadipan.hashnode.dev
NNaveed Ahmed3d ago · 4 min readHow a Next.js RCE Hijacked Our AWS App Runner ContainerFrom an AWS Trust & Safety alert to a compromised production container: a real-world DevSecOps incident involving Next.js, React Server Components, and AWS networking. The Incident: An Unexpected AWS naveedkumbhar.hashnode.dev
VVictor Okoroafor3d ago · 12 min readI Built an Offline AWS Auditor. It Caught My Mistakes, Then Made Its Own.Originally published on DEV as a submission for the Hacktoberfest Open-Source AI Challenge Week 2: Side Hustle. My first user (it was me) My final-year project was a serverless fintech backend on AWS:victorokoroafor.hashnode.dev
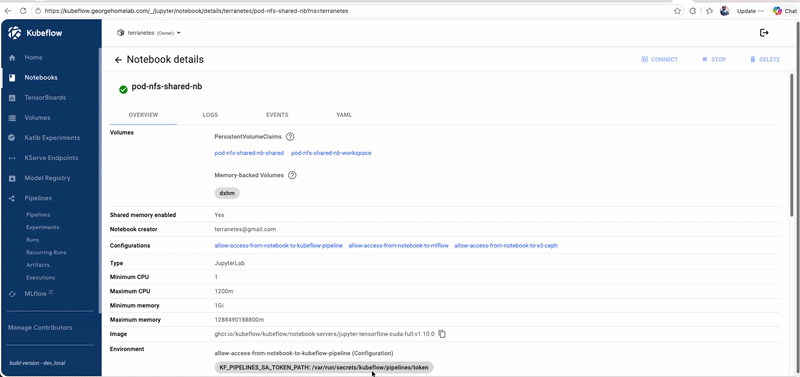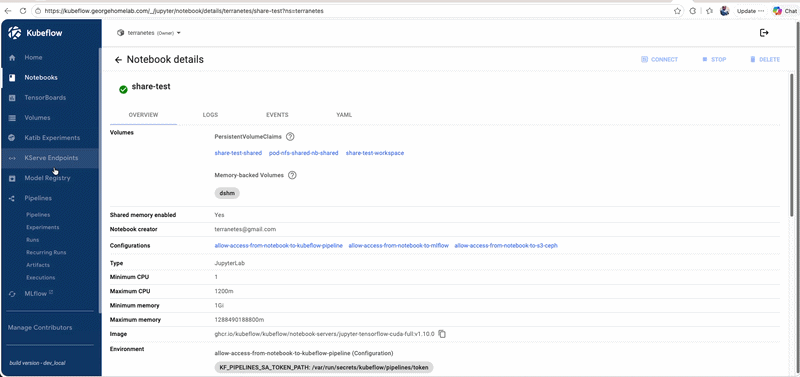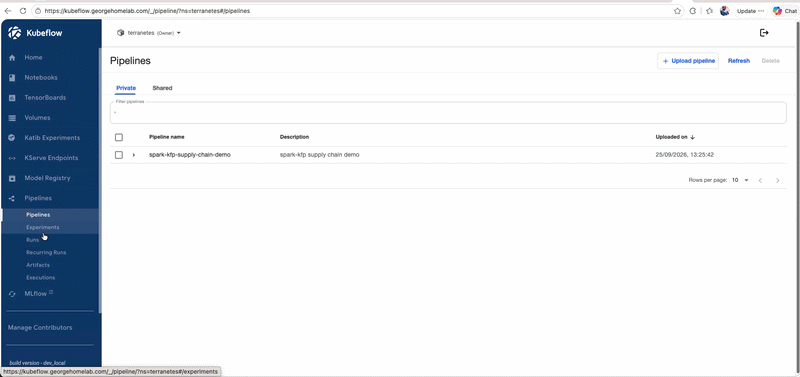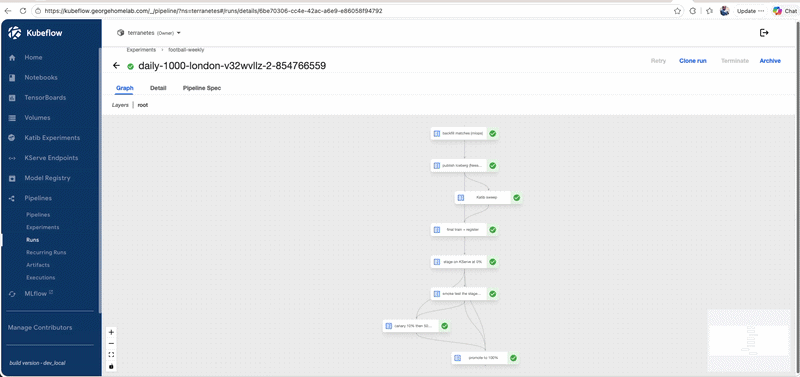
GGeorge Ezejiofor4d ago · 50 min readBrownfield Kubeflow on RKE2: Swapping Dex & SeaweedFS for Keycloak & Ceph RGWUpstream Kubeflow assumes a greenfield cluster and ships its own Dex, SeaweedFS and MySQL, with its own oauth2-proxy in front. My homelab already had better versions of most of those. This is the brow2Ygeorgeezejiofor.com
BBreachLine Labs4d ago · 5 min readYou Fixed the Vulnerability. Now Prove It: A Simple Retest ChecklistA security ticket gets closed. The code was changed. The pull request was approved. Everyone moves on. But was the issue actually fixed? Often nobody checks. At BreachLine Labs we think that last stepbreachlinelabs.hashnode.dev