LTLưu Tuấn Anhinblog.fiscybersec.com·13h ago · 13 min readSparroWocky & SilentMoonwalk Technique: When Backdoor Spoofs Call Stack Disables EDROverview When cybersecurity researchers analyzed the memory of a compromised government server in Latin America, they found Lewis Carroll's nonsense poem Jabberwocky sitting quietly inside a sophistic00
4F404 Foundersin404-founders.com·Sep 28 · 7 min readOperation RapidRust: APT36 Hid Its C2 Inside GitHubThe Pakistani intelligence-linked hacking group APT36 spent August 2026 quietly running four new malware families against Indian and Afghan government networks. The command-and-control infrastructure 00
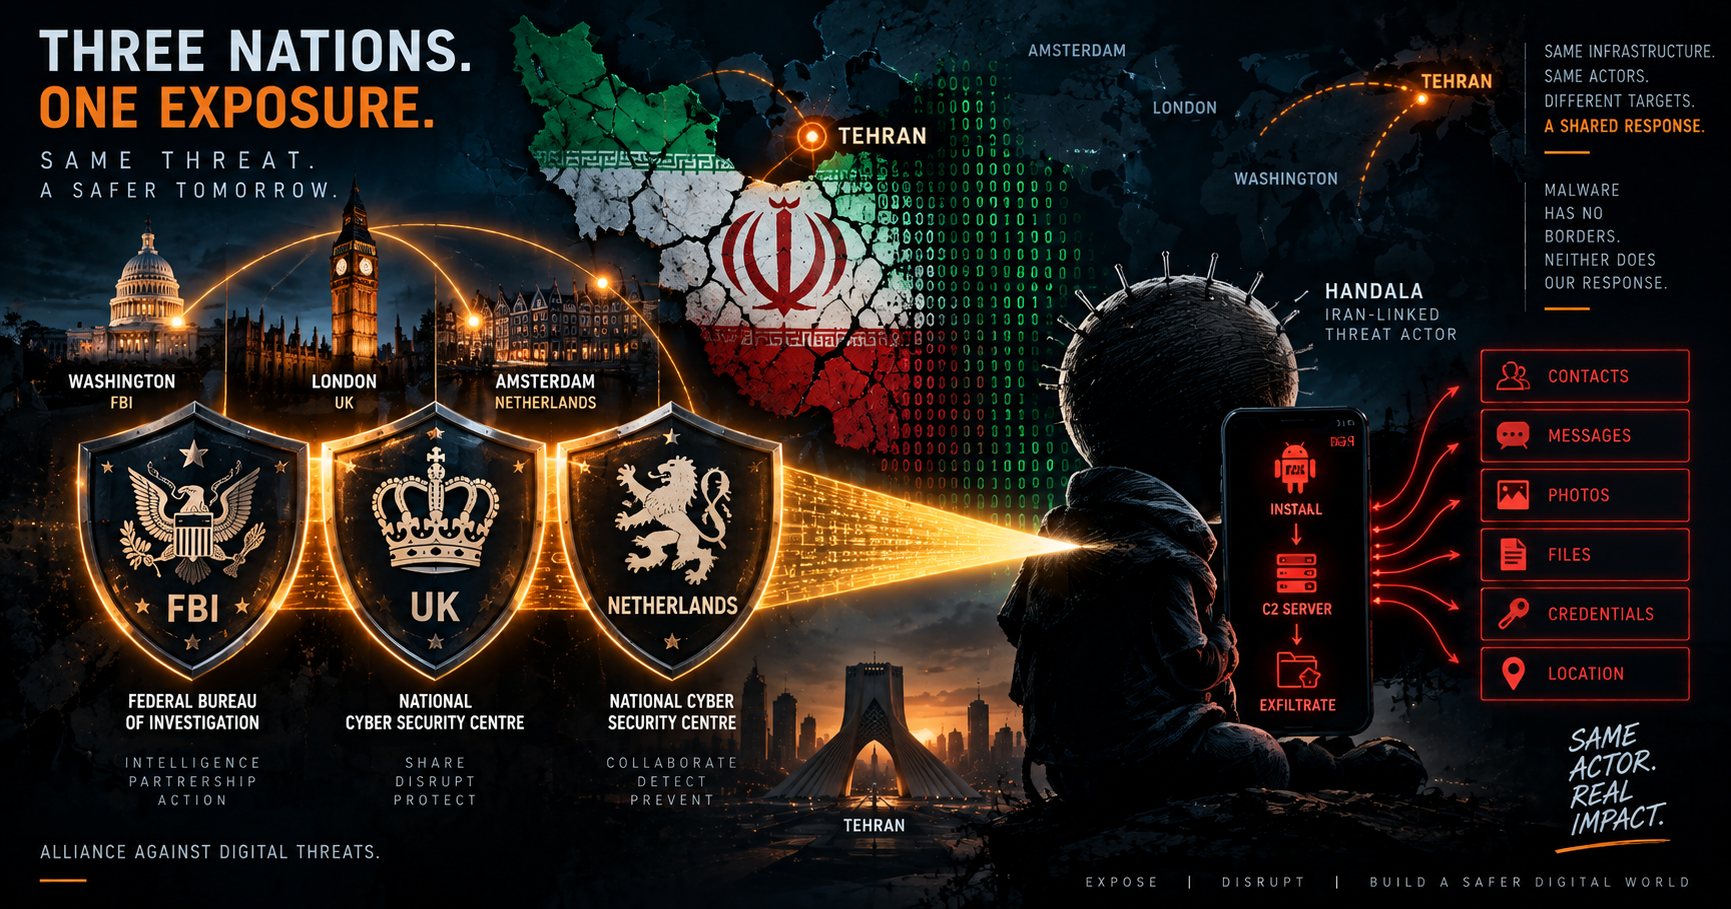
VKVikram Kumar Shuklainvikramkumarshukla.hashnode.dev·Sep 17 · 5 min readIran-Linked Handala Hack: UK, US, Netherlands Expose CHOSEN BRICK Spyware CampaignThe headline: Three Western intelligence agencies just dropped a coordinated advisory naming Iran's Ministry of Intelligence and Security (MOIS) as the force behind CHOSEN BRICK spyware — deployed by 00
VNVũ Nhật Lâminblog.fiscybersec.com·Aug 25 · 22 min readHoneyMyte Takes CoolClient Into the Kernel: When a Rootkit Changes What Windows Lets You SeeSummary CoolClient was already a fully capable espionage backdoor: keylogging, clipboard theft, credential harvesting, file management, system reconnaissance, and a plugin-based extension architecture00
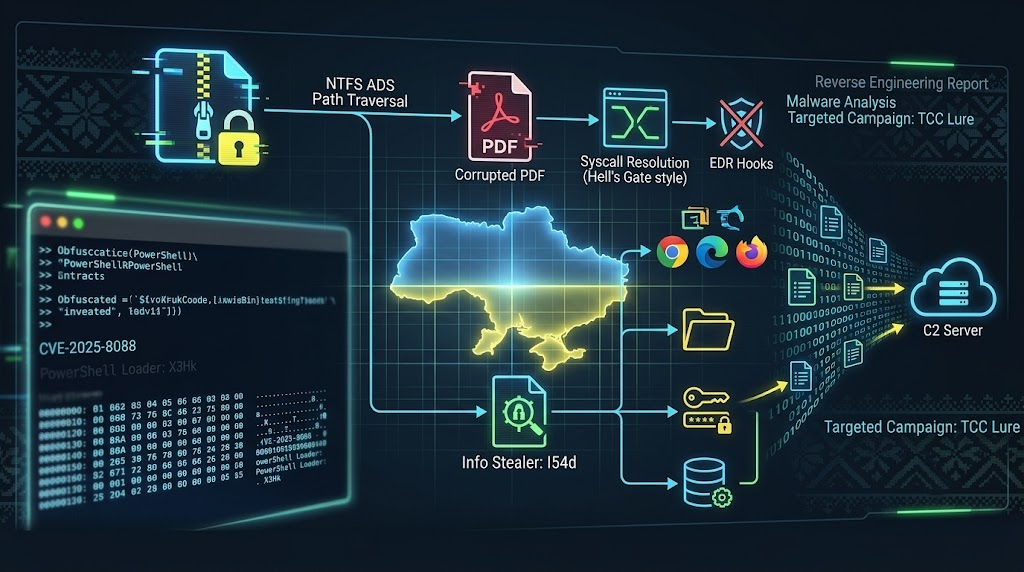
NĐNguyễn Đăng Hưnginbluecyber.hashnode.dev·Jul 22 · 36 min readBeyond the Archive: CVE-2025-8088 Stealer Targeting Ukraine0. Overview This report details a targeted cyber-espionage campaign conducted by the Russia-aligned threat actor group APT SHADOW-EARTH-066 (also tracked by CERT-UA as UAC-0226), delivering an updated00
LTLưu Tuấn Anhinblog.fiscybersec.com·Jun 23 · 14 min readOceanLotus and the remarkable strategic shift in Vietnam's cyberspaceCampaign overview For many years, OceanLotus (APT32) has been known as one of the most prominent cyber espionage groups in Southeast Asia, regularly appearing in reports about intelligence gathering a00
TATameem Amjadinlabsx.hashnode.dev·Jun 15 · 10 min readKG DistributionI Solved 13Cubed's KG Distribution Memory Forensics Lab - Here's the Full Walkthrough Hunting a Sliver C2 implant through a VMware memory dump with MemProcFS, one artifact at a time. The two memory 00
VNVũ Nhật Lâminblog.fiscybersec.com·Jun 9 · 15 min readRemotePE — The Lazarus RAT that lives in memorySummary A subgroup of Lazarus — the North Korea-linked APT known for cryptocurrency heists worth hundreds of millions of dollars — has retired its older tooling (ThemeForestRAT, PondRAT) in favour of 00
VNVũ Nhật Lâminblog.fiscybersec.com·Jun 8 · 13 min readOpen Directory, Open Season: Inside Red Lamassu's JFMBackdoorExecutive Summary A misconfigured open directory did what years of stealth could not: it handed threat hunters the full toolkit of Red Lamassu (also tracked as Calypso and Bronze Medley), a China-nexu00
VNVũ Nhật Lâminblog.fiscybersec.com·May 30 · 12 min readFamousSparrow Targets Azerbaijani Energy Infrastructure: A Three-Wave Chinese APT Espionage CampaignExecutive Summary Between December 25, 2025 and late February 2026, the China-linked APT group FamousSparrow conducted three successive intrusion waves against an Azerbaijani oil and gas company — eac00