Rrathsarainrr-cyber.hashnode.dev·5d ago · 7 min readAnonTestLab: Ten Years, Three Attempts, and One Idea That Wouldn't Let GoTL;DR: the tool is at hashtagrr.github.io/AnonTestLab. The rest of this is how it came to exist. Round one: an idea and no coding experience to build it I got my hands on the Tor Browser almost ten y00
Rrathsarainrr-cyber.hashnode.dev·Sep 3 · 11 min readWindows Memory Forensics: Finding a Live Infection with VolatilityPID 1484 had been running since boot. Nothing about that was unusual: it was Explorer.exe, the process every Windows machine on earth is running right now. What was unusual was the process hanging off00
Rrathsarainrr-cyber.hashnode.dev·Sep 3 · 9 min readGNU/Linux Memory Forensics: Is the Compromise Still Live?It's easy to think of memory forensics purely as a hunt for something malicious. On this case, a GNU/Linux server that had already been through a full attack chain, initial access, privilege escalatio00
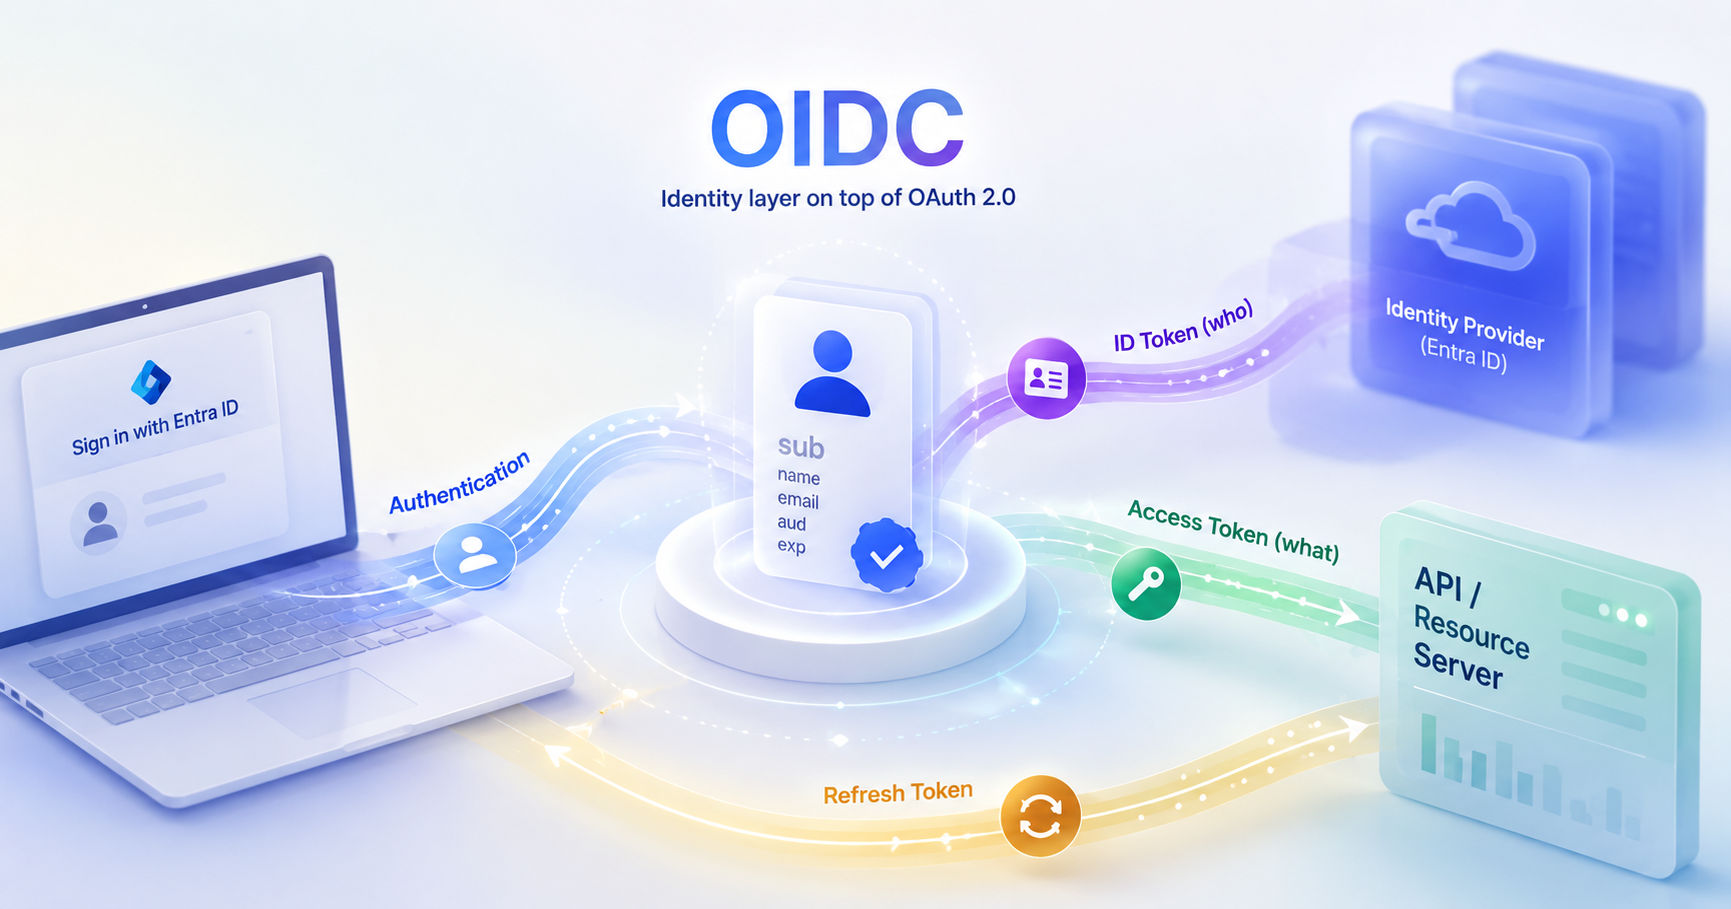
Rrathsarainrr-cyber.hashnode.dev·Aug 31 · 19 min readOpenID Connect: The Identity Layer OAuth Was MissingBy the time I actually heard the word OIDC, I'd already been through OAuth and PKCE conversations I hadn't fully understood, years apart from each other, and this one arrived even later than those. It00
Rrathsarainrr-cyber.hashnode.dev·Aug 15 · 10 min readWhat We Got: From Cloud Security Platform to Operational CapabilityA few months after the operationalizing work covered in the last article, it stopped being a project. It became part of how we worked. This article is about what changed once that happened. The Metri00
Rrathsarainrr-cyber.hashnode.dev·Aug 14 · 31 min readUnderstanding OAuth 2.0: Delegation, Grant Types, and the Attacks That Actually HappenThe first time I heard the term OAuth, I didn't know what it meant. I was in a conversation with a DBA lead about something adjacent to authentication and authorization, and he mentioned, almost in pa00
Rrathsarainrr-cyber.hashnode.dev·Aug 6 · 15 min readIdentity Foundations: Everything Before OAuthBefore any protocol makes sense on its own terms, a few things underneath it need to be settled first: what authentication and authorization actually are as distinct concepts, how identity gets carrie13N
Rrathsarainrr-cyber.hashnode.dev·Aug 5 · 9 min readIdentity Was the Gap I Did Not Know I HadI had worked across cloud security engineering, vulnerability assessment, penetration testing, and application security. I had reviewed IAM configurations across multiple cloud platforms, flagged over11N
HSHarshal Shahindelvingwithharshal.hashnode.dev·Jul 28 · 7 min readRAG Security: Threats, Attack Vectors, and Best Practices for Enterprise AIRetrieval Augmented Generation (RAG) has become the backbone of enterprise AI applications, enabling Large Language Models (LLMs) to provide accurate, context aware responses using organizational data00
Rrathsarainrr-cyber.hashnode.dev·Jul 22 · 9 min readEverything Passed. Then the End-to-End Ping Failed.I dedicated my final year project to an unsung hero. Stanislav Petrov, the Soviet lieutenant colonel who prevented nuclear war by deciding not to trust a system that told him it was certain. My superv10