MTMuhammad Tahirinmtdeveloper.hashnode.dev·5d ago · 12 min readZero-Trust API Security: OAuth 2.1, Distributed Rate Limiting, and Automated Threat MitigationThis article was originally published on Muhammad Tahir's Portfolio. Introduction & Industry Context The modern digital ecosystem in 2026 is defined by decentralized networks, globally distributed edg00
AArshadinblog.arshadakl.in·Sep 5 · 6 min readHow a Profile Update Feature Could Drain a Company's Bank AccountI was looking at one of the most normal features you can find in almost any application: Update Profile. Nothing exciting. A user changes their name, profile picture, maybe email, and the backend upda00
AArshadinblog.arshadakl.in·Sep 3 · 8 min readOTP Bypass : When Client-Side Validation Becomes a JokeOTP flows make developers feel safe. They look secure. They feel secure. They even demo well. But here’s the uncomfortable part: sometimes an OTP flow can become almost useless if the actual security 00
Cchaitalisinghaniaincybersecuritydigest.hashnode.dev·Sep 1 · 5 min readAPI Penetration Testing vs Web Application Penetration TestingModern applications are a network of APIs; APIs tend to connect the user, service, database, and even external/ third-party software. APIs need to be secure because of the level of access and control 00
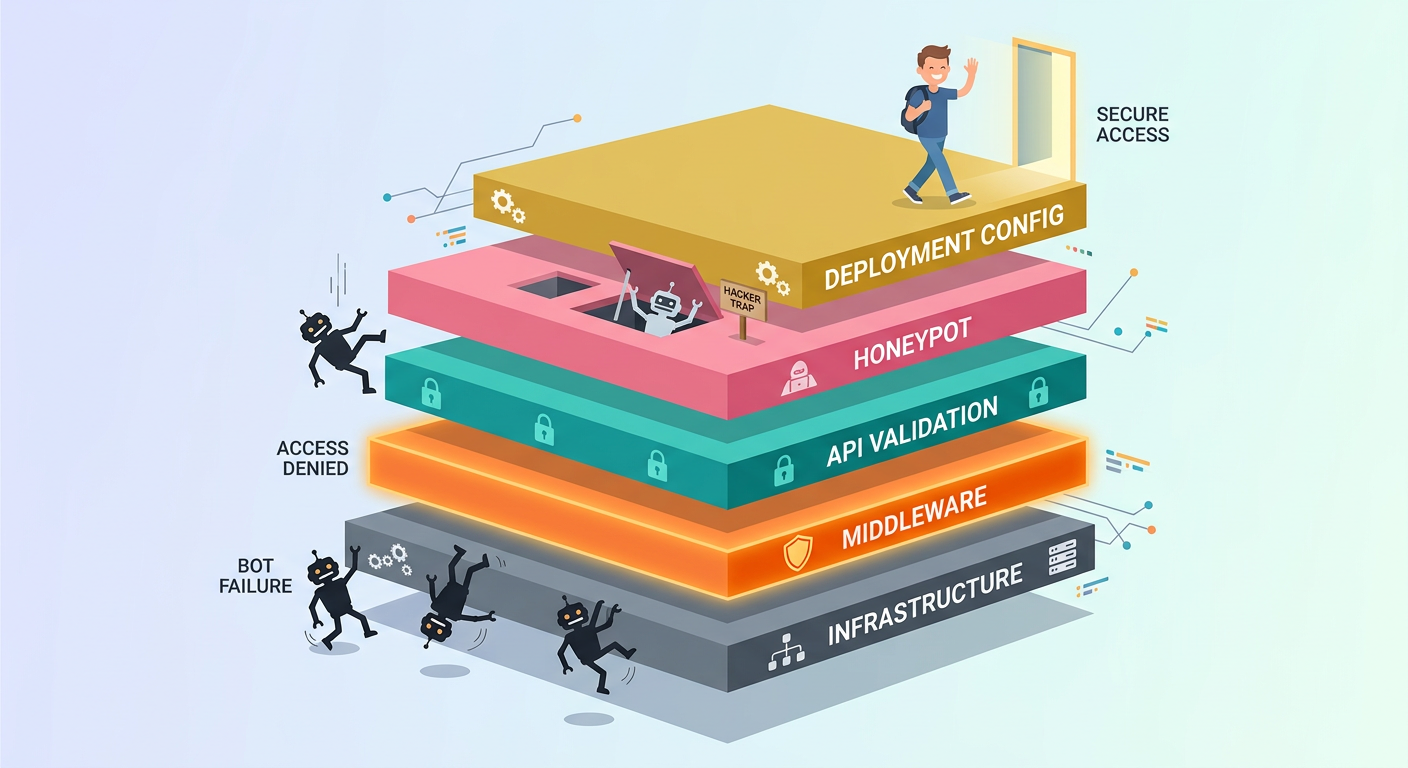
JSJaber Saidinjabersaid.hashnode.dev·Aug 31 · 20 min readI Built a Prompt That Makes AI Agents Harden Any Web App Against Bot Abuse — Here's the Full System, the Tests, and What I LearnedHow suspicious traffic on my production sites led me to build a universal, framework-agnostic abuse deterrence system that any AI coding agent can implement — and the verification tests that proved my00
CSConverge Solutioninconvergesol.hashnode.dev·Aug 31 · 5 min readWhat Makes ASP.NET Core APIs Secure in Production?Securing an ASP.NET Core API isn't simply about adding JWT authentication and enabling HTTPS. Once an API becomes part of a larger application ecosystem, it may communicate with web and mobile clients00
CDCoding Dropletsincodingdroplets.com·Aug 30 · 10 min readPreventing Path Traversal in ASP.NET Core File Download APIsEvery API that serves a file eventually grows an endpoint that takes a filename from the client. It ships as a two-line convenience, it works, and it becomes the most dangerous route in the service. P00
SSSandra Sydneyinsandrasydney.hashnode.dev·Aug 24 · 3 min readTier-1 SOC Playbook: Detecting and Containing DDoS & Mass Assignment Attacks using NIST SP 800-61Detecting and Containing DDoS & Mass Assignment Attacks using NIST SP 800-61 This standard operating playbook defines the containment protocol for neutralizing high-impact REST API security incidents 00
Ccontactinpykero.hashnode.dev·Aug 23 · 6 min readRate Limiting AI Features: Stop One User From Draining Your BudgetRate-limit AI features at the user, session, and endpoint level, not just by trusting your LLM provider's account-wide API limit. A single compromised account, a scraping bot, or a client-side bug tha10
CDCoding Dropletsincodingdroplets.com·Aug 22 · 10 min readSecuring an MCP Server in ASP.NET Core: OAuth, Scopes and Tool AuthorizationThe thing that makes MCP servers so quick to build is also what makes them dangerous. You decorate a method, the SDK generates a tool definition, and a language model somewhere can now invoke it. That20