TLTirthak Likharintirthaklikhar.hashnode.dev·6d ago · 6 min readWhat EDR Reveals After a Suspicious Document OpensWhen a Word document launches a command shell and that shell retrieves an executable, there is already a sequence worth investigating. The next question is how far it went. A downloaded file and a run00
JJebitokinsharonjebitok.com·Sep 23 · 3 min readPortal Drop - subdomain, grep, EDR, Access Log Analysis (TryHackMe)Link to the challenge on TryHackMe: Portal Drop You are on the day shift in the ProbablyFine when the monitoring dashboard flashes red. A new alert appears in the WAF summary, reporting a web scan on00
HCHazel Chirindainhazelsec.hashnode.dev·Sep 17 · 9 min readSecurity Tools Don’t Fix Bad Security ProcessesOne thing I've learned from working across different cybersecurity environments is that organisations can have very good security tools and still have security gaps. You can deploy EDR. You can implem00
SSunnyincybersecurity-learning.hashnode.dev·Sep 14 · 20 min read🛡️ TryHackMe — Introduction to EDR | Learning GuideSpoiler-Free Learning Guide: This article contains no TryHackMe flags, dashboard-specific answers, malware paths, URLs, or direct task solutions. It focuses on EDR architecture, telemetry, detection, 00
AKAndriy Kovalenkoindeadpacket.hashnode.dev·Sep 4 · 24 min readThe Ransomware Attack Starts Before Encryption: The Warning Signs Security Teams Cannot Ignore in 2026Most people still picture ransomware as a malicious program that suddenly lands on a computer and starts encrypting files. That image is dangerously incomplete. In a modern enterprise attack, encrypti00
CIChris Isaiasindarkscene.hashnode.dev·Aug 15 · 25 min readSigned, Staged, and Weaponised: Inside an ACRStealer CampaignBy C. Isaias, and A. Soloviev Introduction Earlier this month, claims circulated on X describing a BYOVD EDR killer said to enumerate and terminate the products of more than 140 security vendors, deli00
EEEa Etin0xnull-security.hashnode.dev·Jul 18 · 3 min readEDR Bypass in 2026: How Attackers Evade Modern Endpoint DetectionTL;DR: EDR tools are more powerful than ever — but so are bypass techniques. Here's what defenders need to know to stay ahead. Why EDR Alone Is Not Enough Endpoint Detection and Response (EDR) platfo00
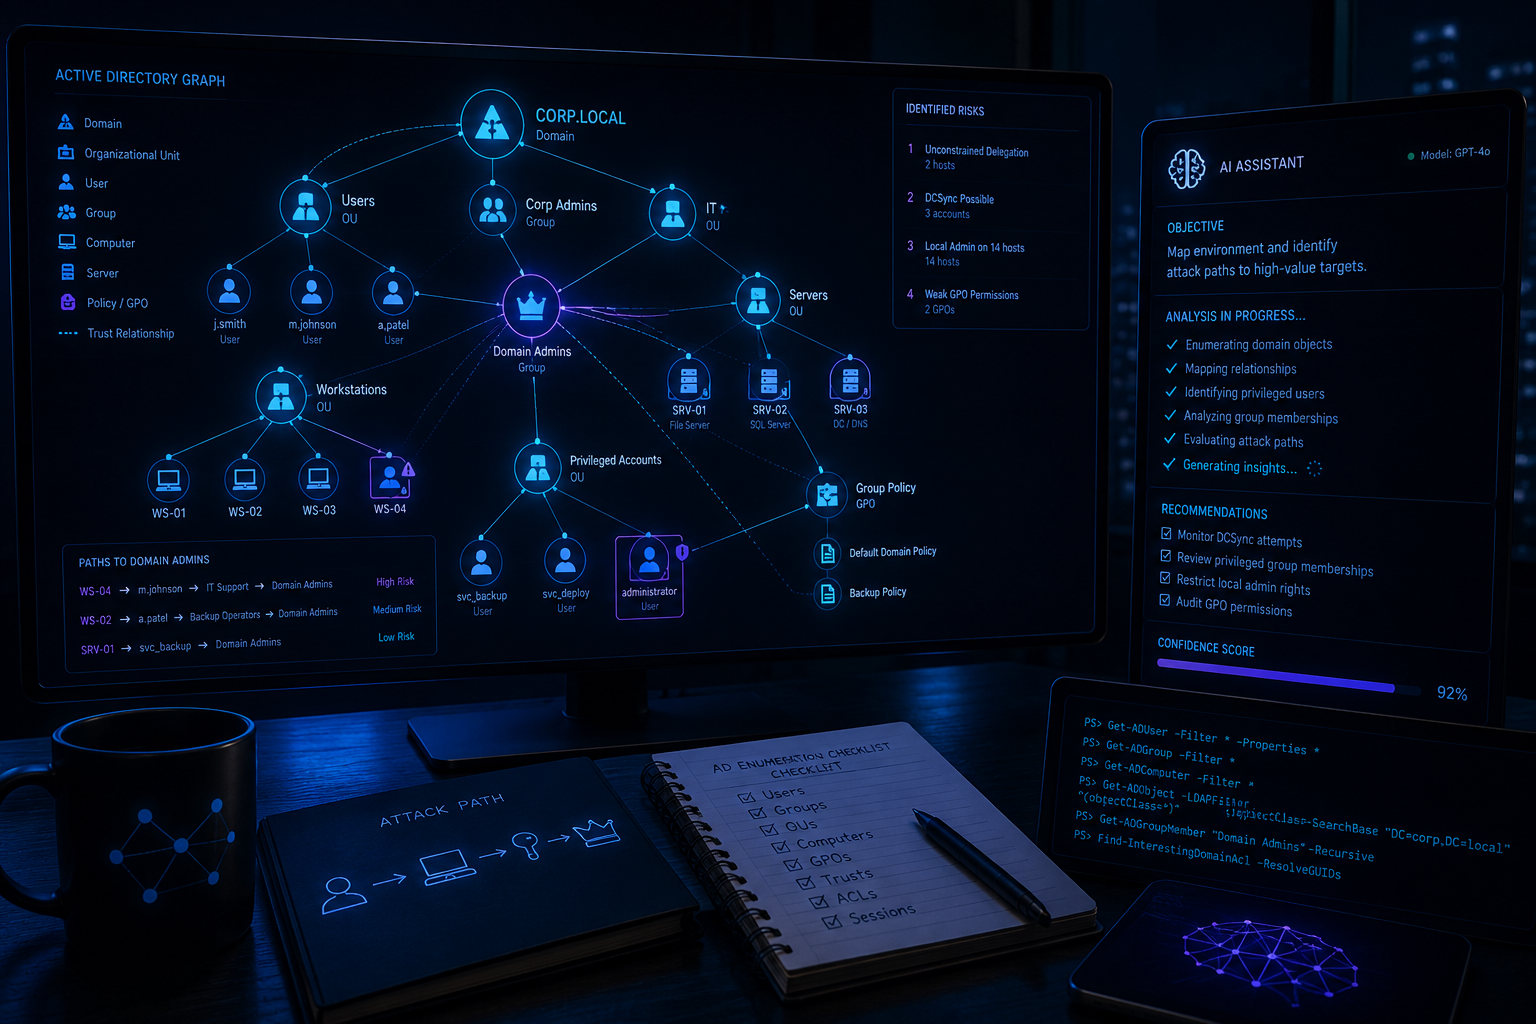
4F404 Foundersin404-founders.com·Jun 5 · 3 min read The AI Intern Just Joined The Red Team The New Workflow For years, breaking into a network was only part of the job. Attackers still needed to: map Active Directory identify privileged accounts understand trust relationships locate sensit00
PPromiseinpromise-security.hashnode.dev·Apr 11 · 4 min readAnonymous but Not Invisible: A Simple Tor Lab With ShodanFor beginners, most of the time its heard to use Tor to stay anonymous on the internet. But are you really anonymous? I’m running this lab inside a Kali Linux VM. I installed Tor and Tornet, then star00
LTLưu Tuấn Anhinblog.fiscybersec.com·Apr 9 · 8 min readHow was the defense system disabled? Inside the campaign of Qilin & WarlockSummary of the campaign Two notorious Ransomware-as-a-Service (RaaS) groups, Qilin and Warlock (also known as Water Manual), are independently deploying the "Bring Your Own Vulnerable Driver" (BYOVD) 00