KKazem Mortazavi·2d agoITDR Explained: Detecting Attackers Who Sign In With Valid CredentialsAn attacker who holds a system administrator's password does not need to break through any wall; they simply sign in. To the firewall, the EDR agent and even the identity management system, an authori2 min read·securityland.hashnode.dev
HHazel Chirinda·5d agoBeyond MFA: What Occurs After an Attacker Gains Access?Discover how attackers exploit stolen sessions, malicious OAuth apps, and compromised accounts, plus ways to strengthen Microsoft 365 security.10 min read·hazelsec.hashnode.dev
CCyber Knight·Nov 3The AI Agent Didn't Break the Product. It Walked Into the Sales Tool.WorkOS builds the login layer for thousands of companies. The breach it disclosed on 2 November didn't touch that product — it reached an internal sales app instead, and what that app held is exactly what makes the next phishing email believable.5 min read·nulltrace.hashnode.dev
ZZero Trust Threads·Oct 26Least Privilege Sounds Simple Until You Have to Implement ItLearn what least privilege really means, why privilege creep happens, and how access reviews, roles, and temporary elevation reduce risk.6 min read·zerotrustthreads.hashnode.dev
ZZero Trust Threads·Oct 26Service Accounts: The Accounts Nobody Notices Until Something BreaksLearn what service accounts are, why non-human identities matter, and how ownership, credentials, monitoring, and least privilege reduce risk.5 min read·zerotrustthreads.hashnode.dev
HHazel Chirinda·Oct 23When a Password Is Not Enough: Understanding Identity-Based AttacksLearn how identity-based attacks compromise Microsoft 365 accounts and how MFA, Conditional Access, and monitoring help strengthen security11 min read·hazelsec.hashnode.dev
ZZero Trust Threads·Oct 9Temporary Access Has a Way of Becoming PermanentTemporary admin rights, firewall rules, vendor accounts, and exceptions can quietly become permanent. Learn why access needs owners and expiration.8 min read·zerotrustthreads.hashnode.dev
AAdeshina Emmanuel·Sep 13How AWS Actually Evaluates IAM Policies (Identity vs Resource)How AWS evaluates IAM policies: implicit deny, explicit deny priority, and the union of identity-based and resource-based policies in the same account7 min read·eadeshina.hashnode.dev
YYury Butuzov·Sep 10The Anatomy of Exposure: Why the Market Cannot Agree on What Counts as OneTwo exposure-management tools can examine the same environment and return very different numbers. That does not necessarily mean that either is wrong.10 min read·yurybutuzov.hashnode.dev
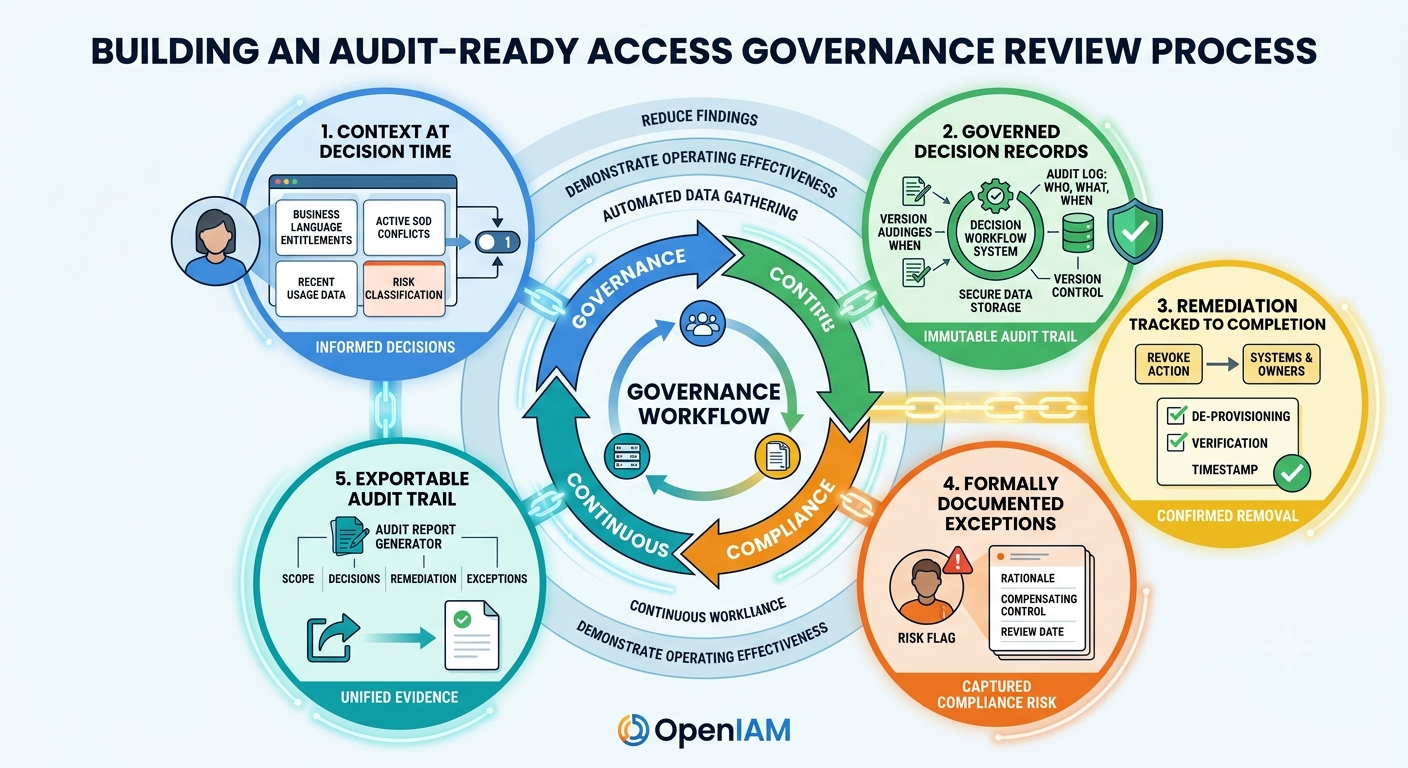
TTushar Openiam·Sep 10The Access Review Your Auditor Cannot Rely OnDiscover why 100% access review completion still leads to audit findings. Learn how to transform rubber-stamp certifications into audit-ready evidence7 min read·openiam.hashnode.dev